Owner and Connector Names for Gateway Accounts
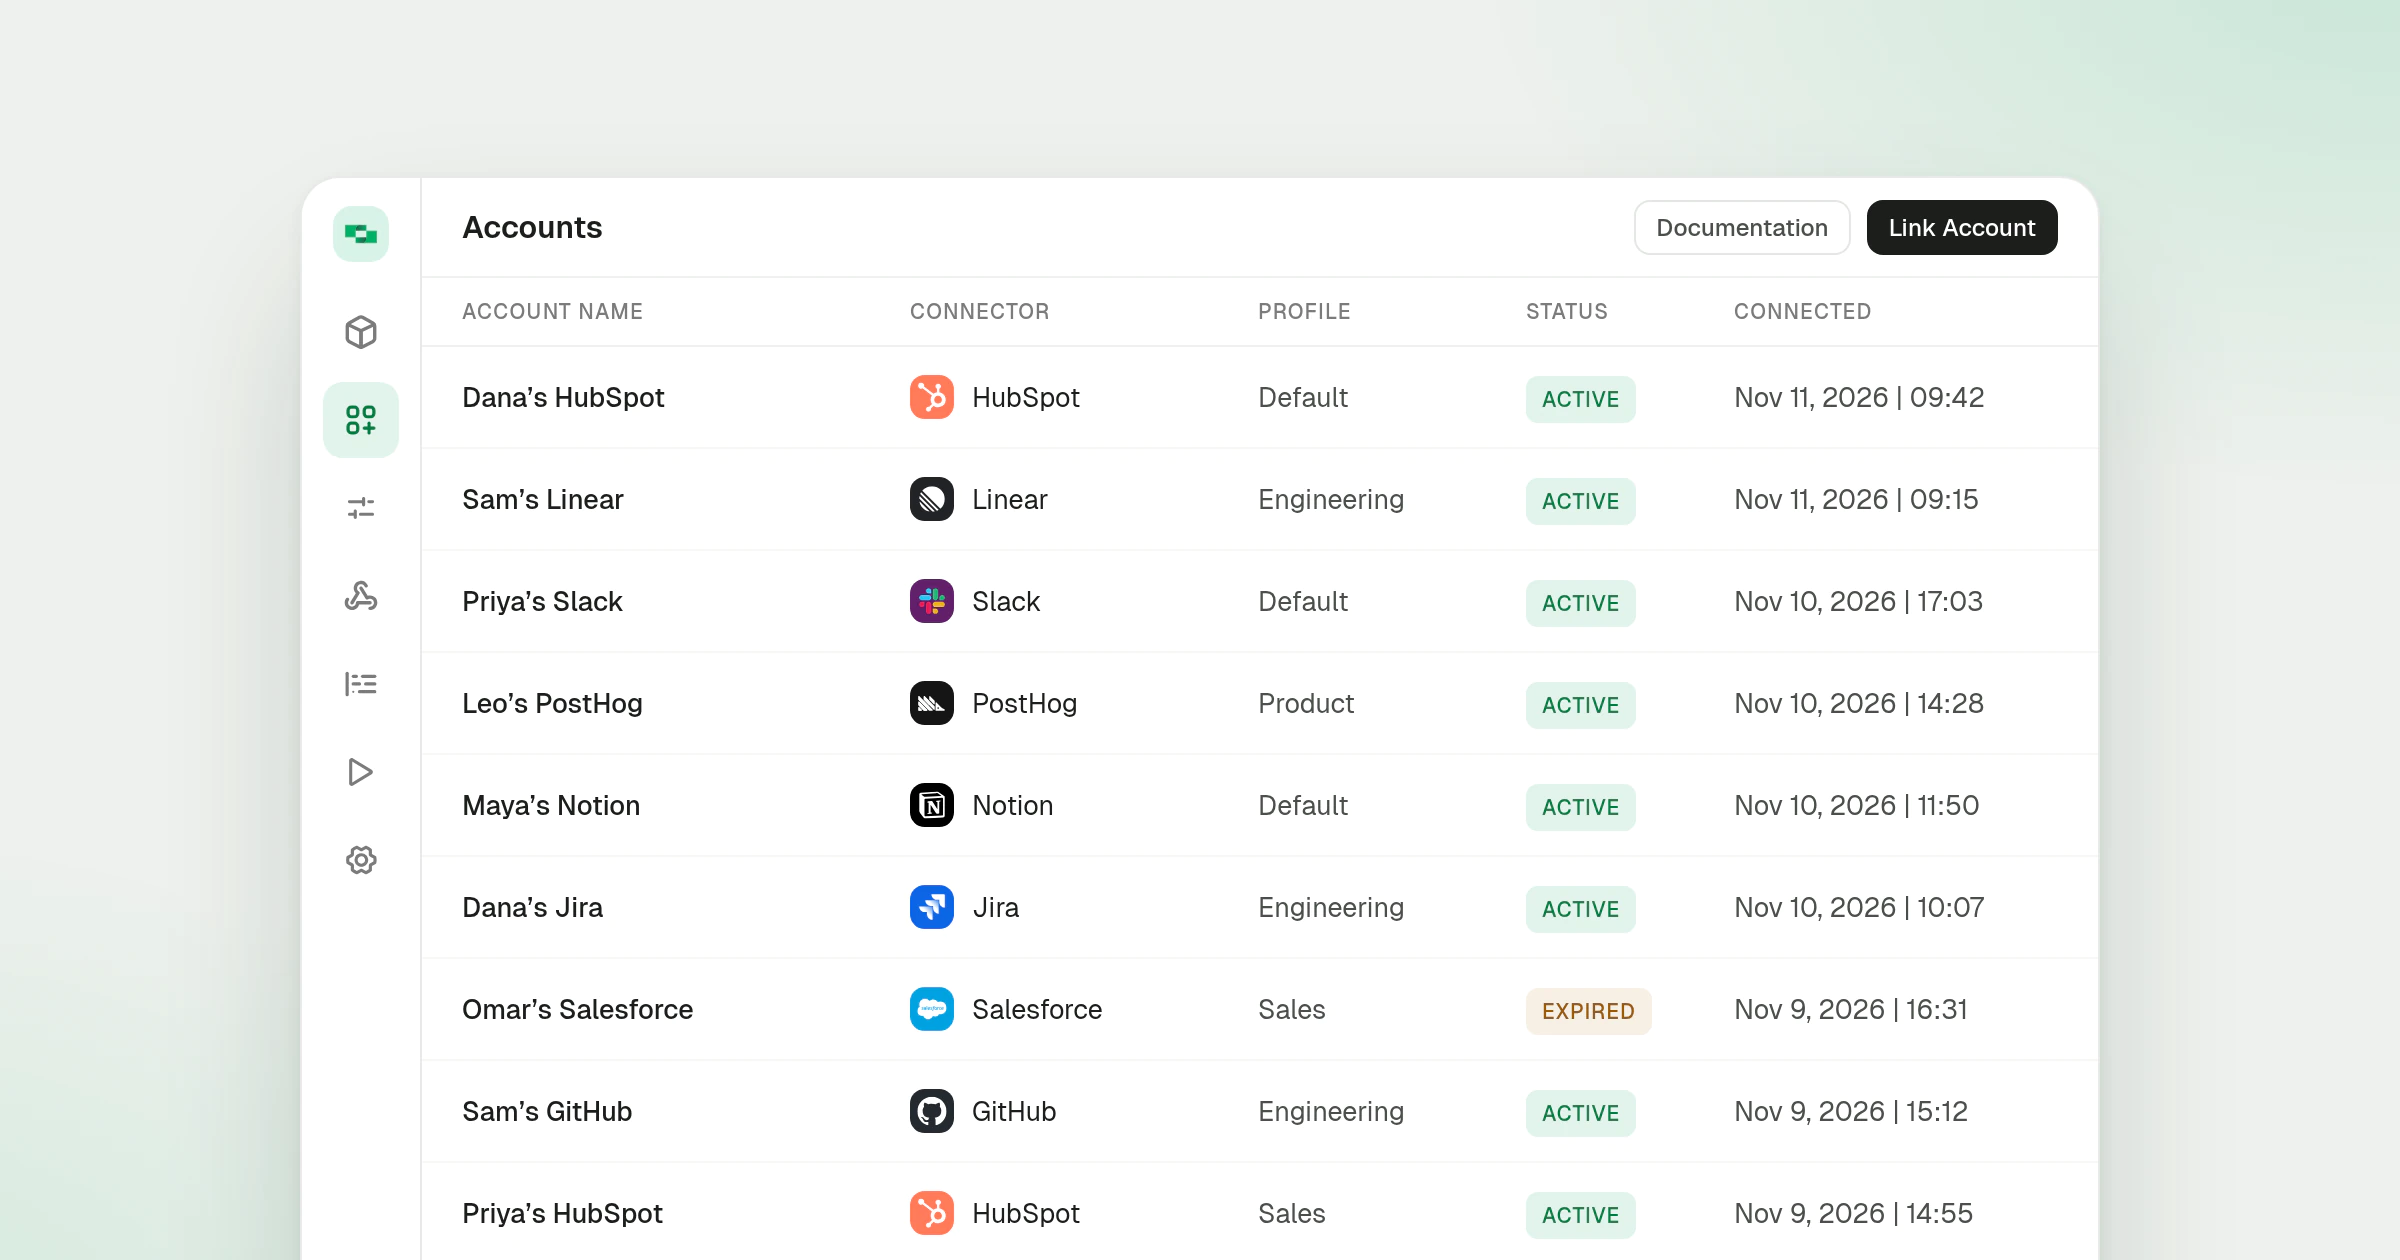
In Gateway organizations, a newly linked account is now named after its owner and its connector, such as Dana's HubSpot, when the owner links it.
Read about Gateway account namesChangelog
A rundown of the latest features, fixes, and improvements from StackOne.
In Gateway organizations, a newly linked account is now named after its owner and its connector, such as Dana's HubSpot, when the owner links it.
Read about Gateway account names
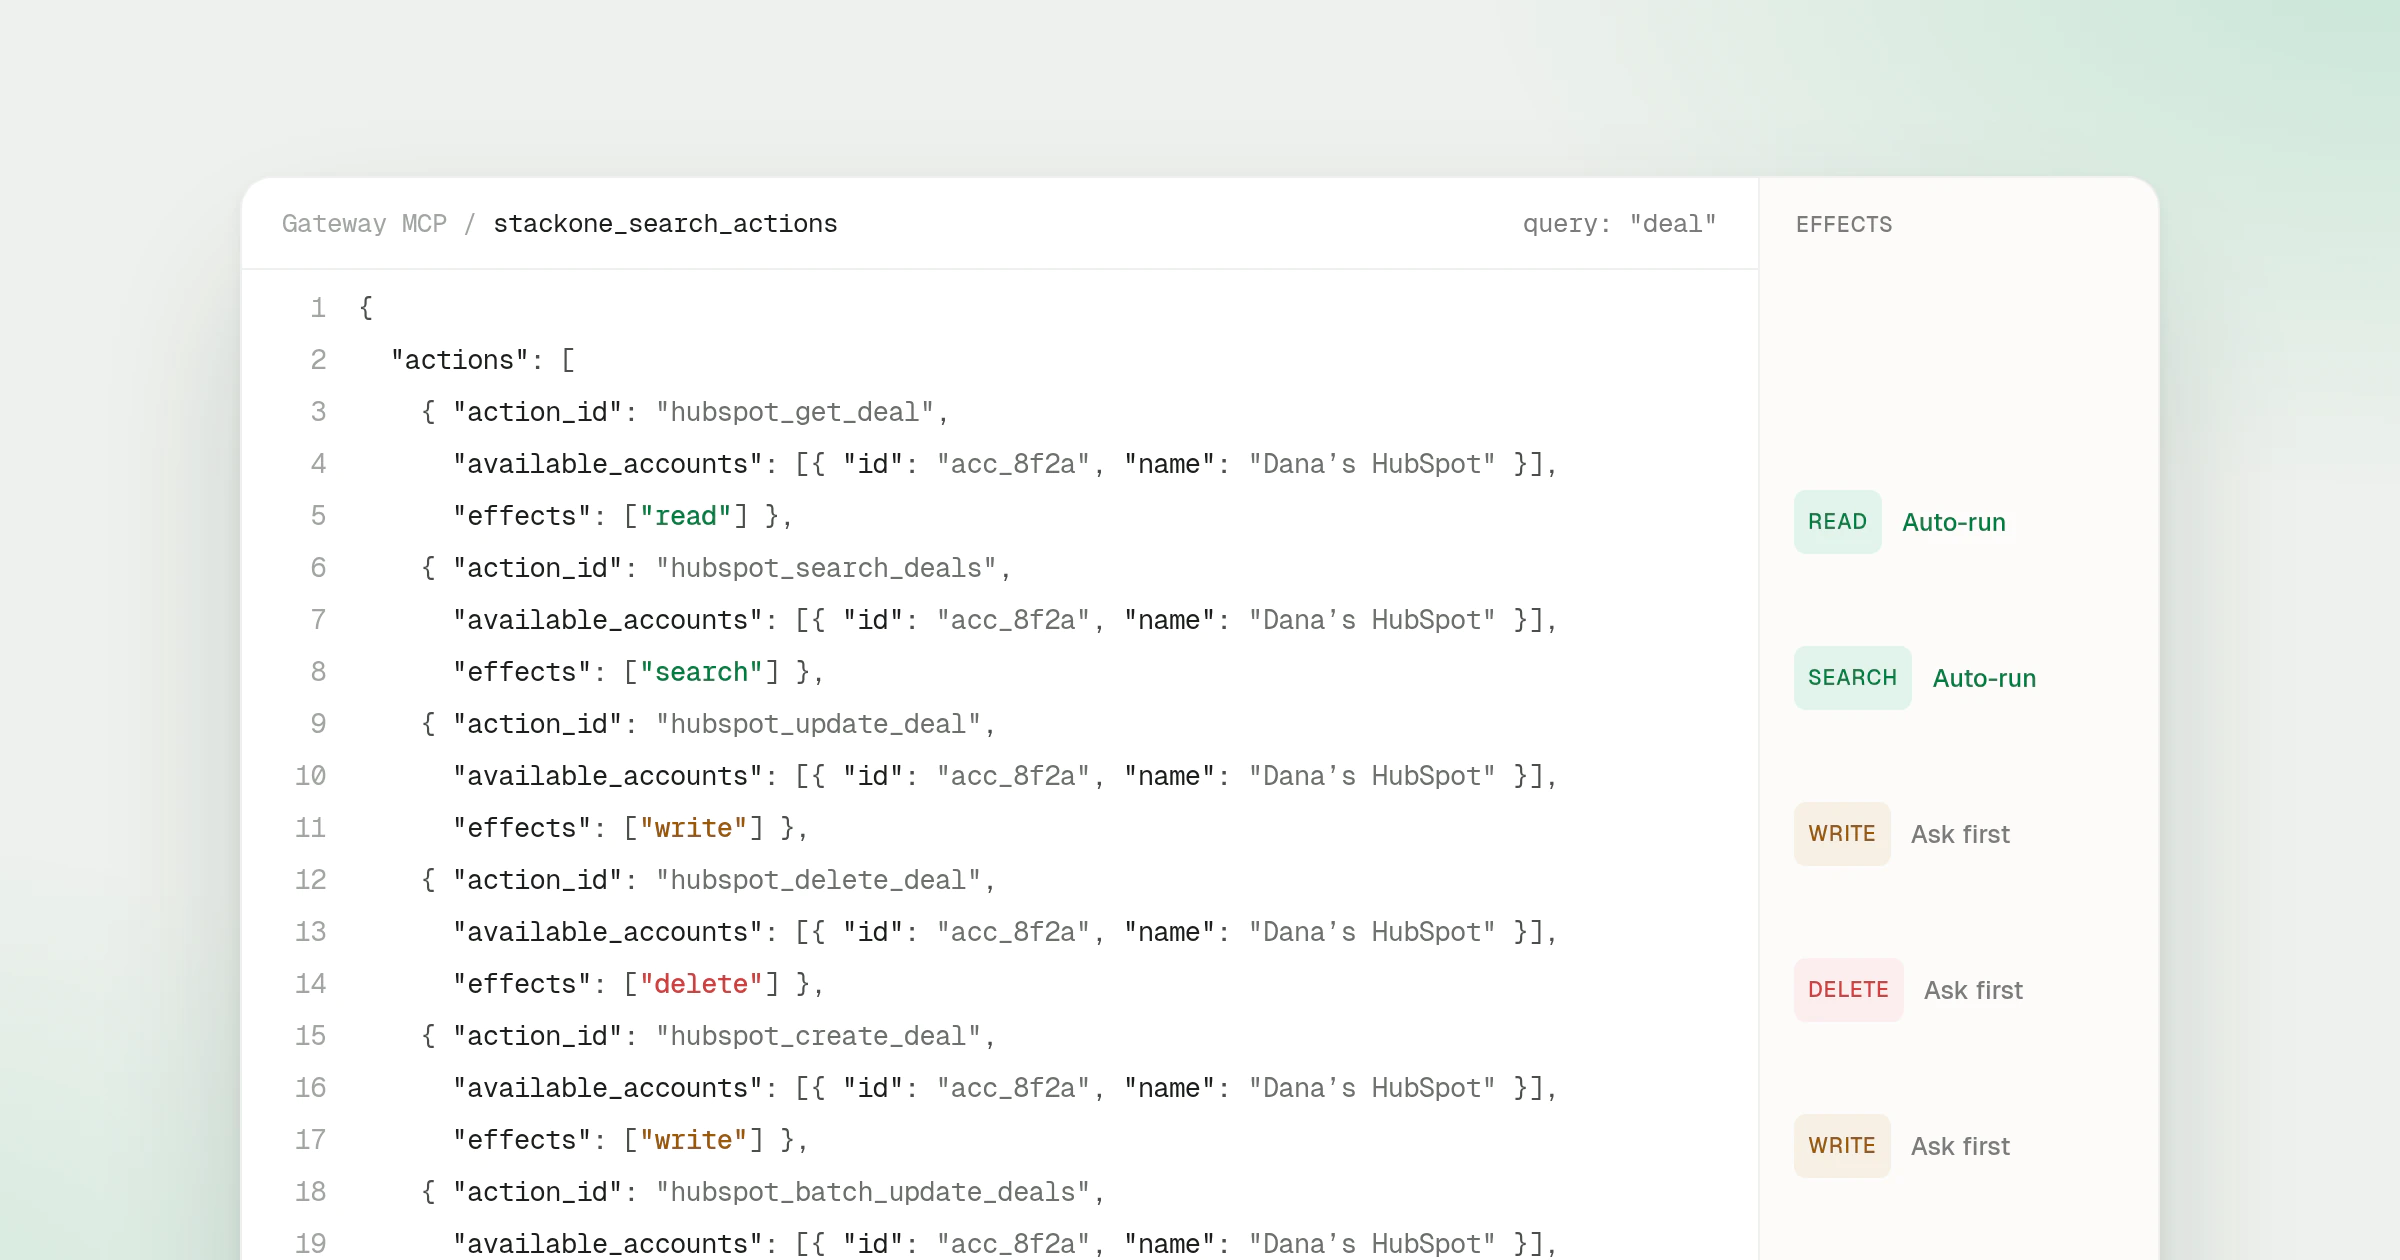
Each action returned by search on the Gateway MCP endpoint now lists its effects, so an agent knows if it reads, writes or deletes before calling it.
Read about MCP search action effects
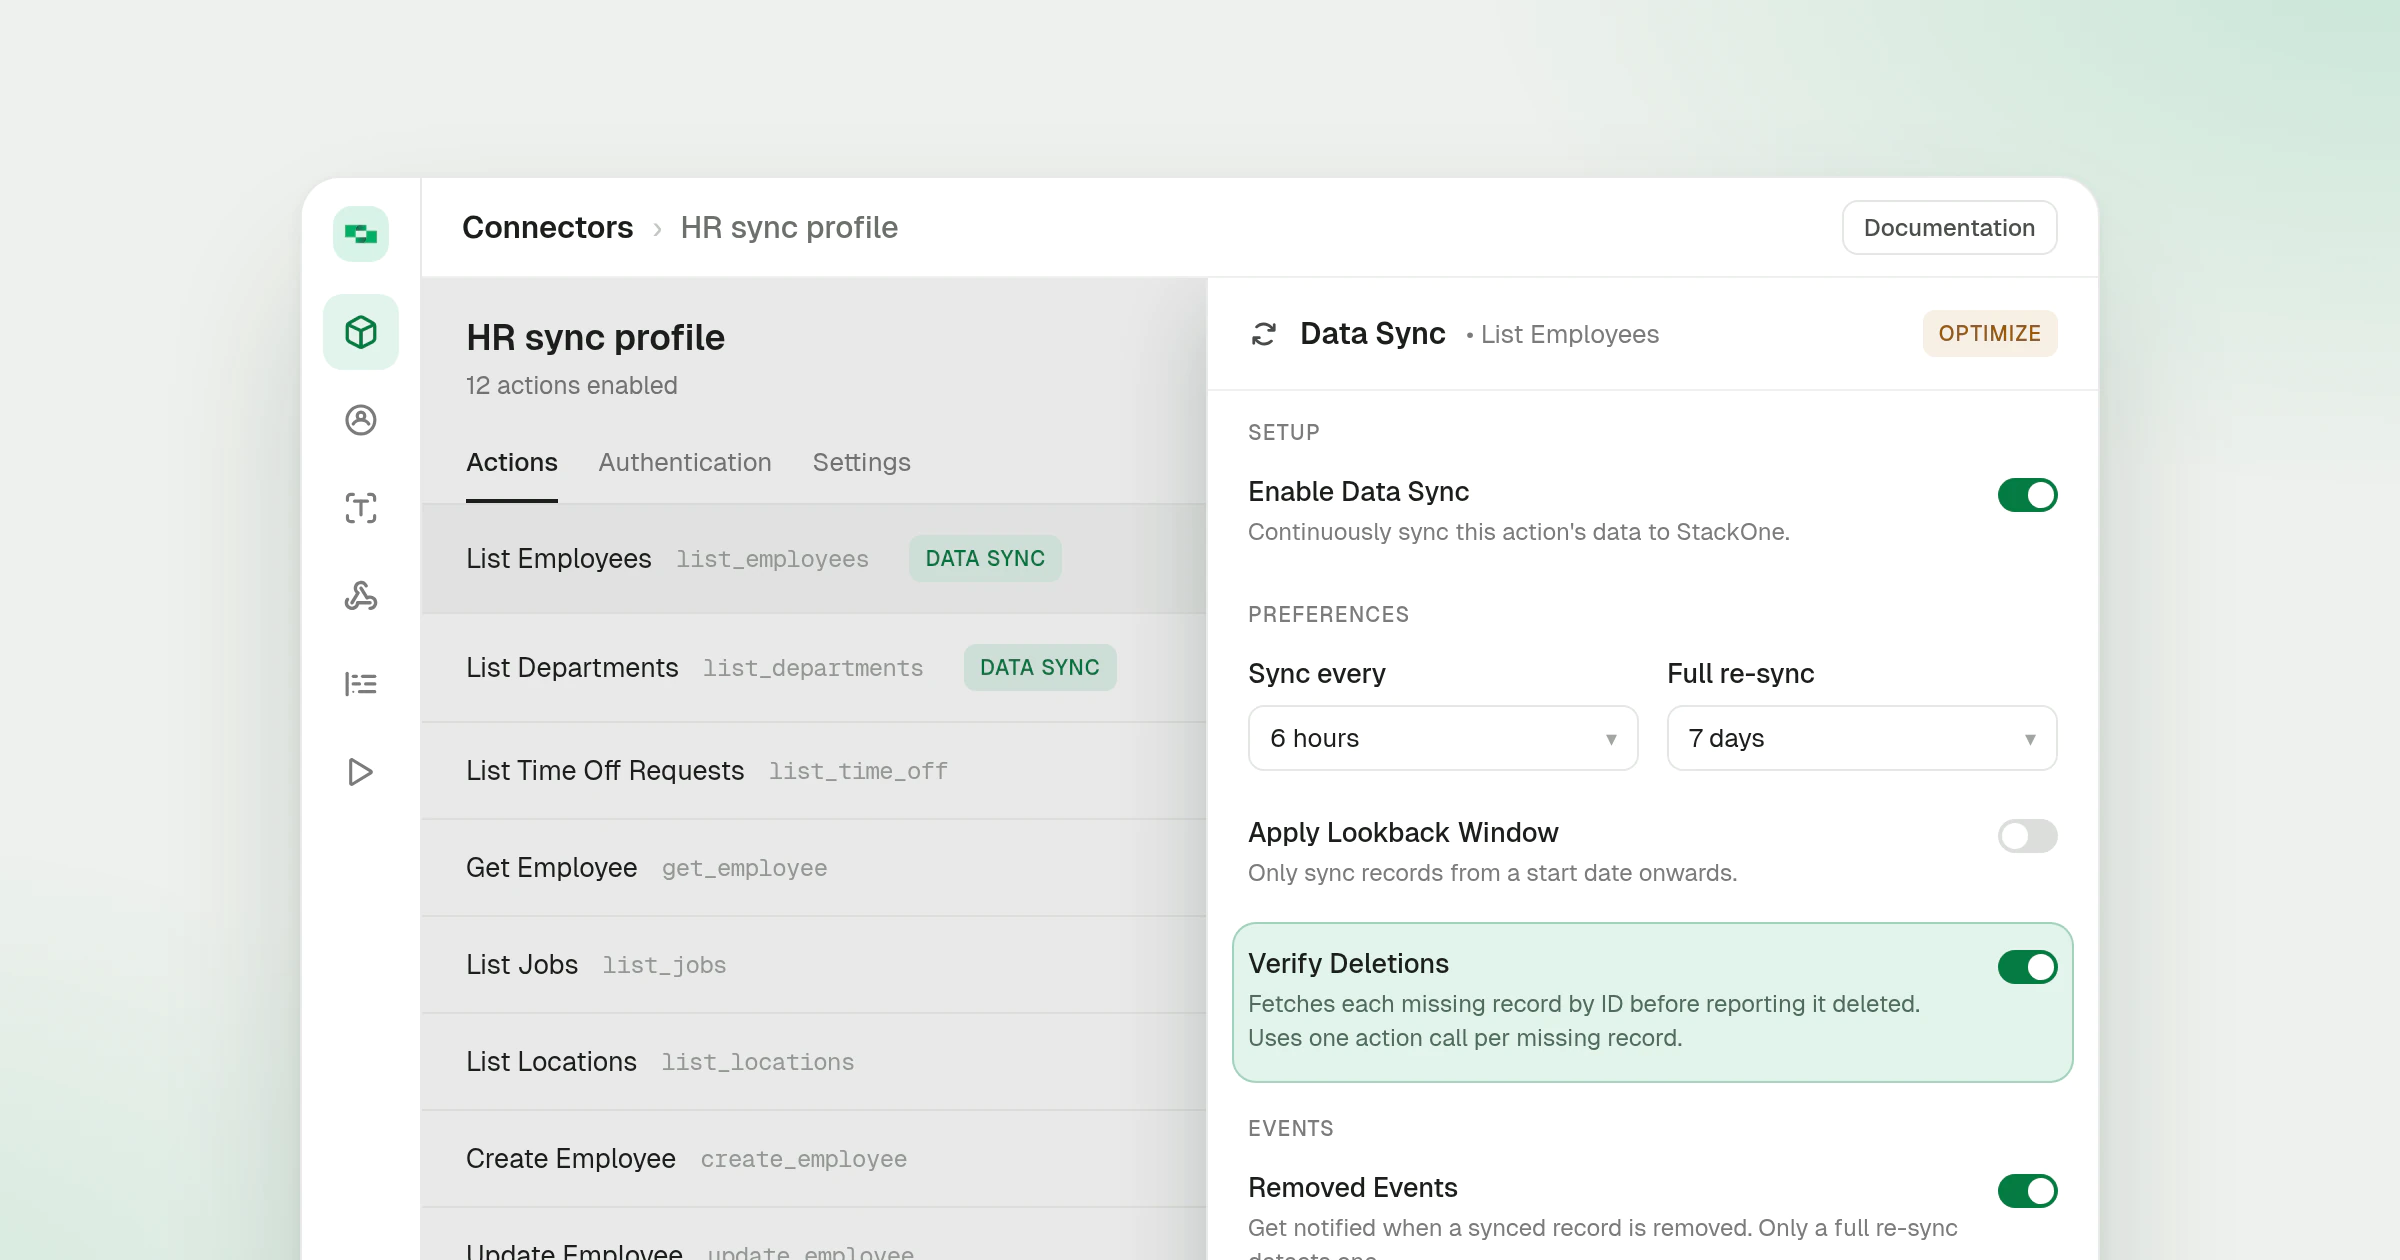
Data Sync can now fetch each missing record by ID before reporting it deleted, so a record a provider list skipped is not reported as removed.
Read about Data Sync verify deletions
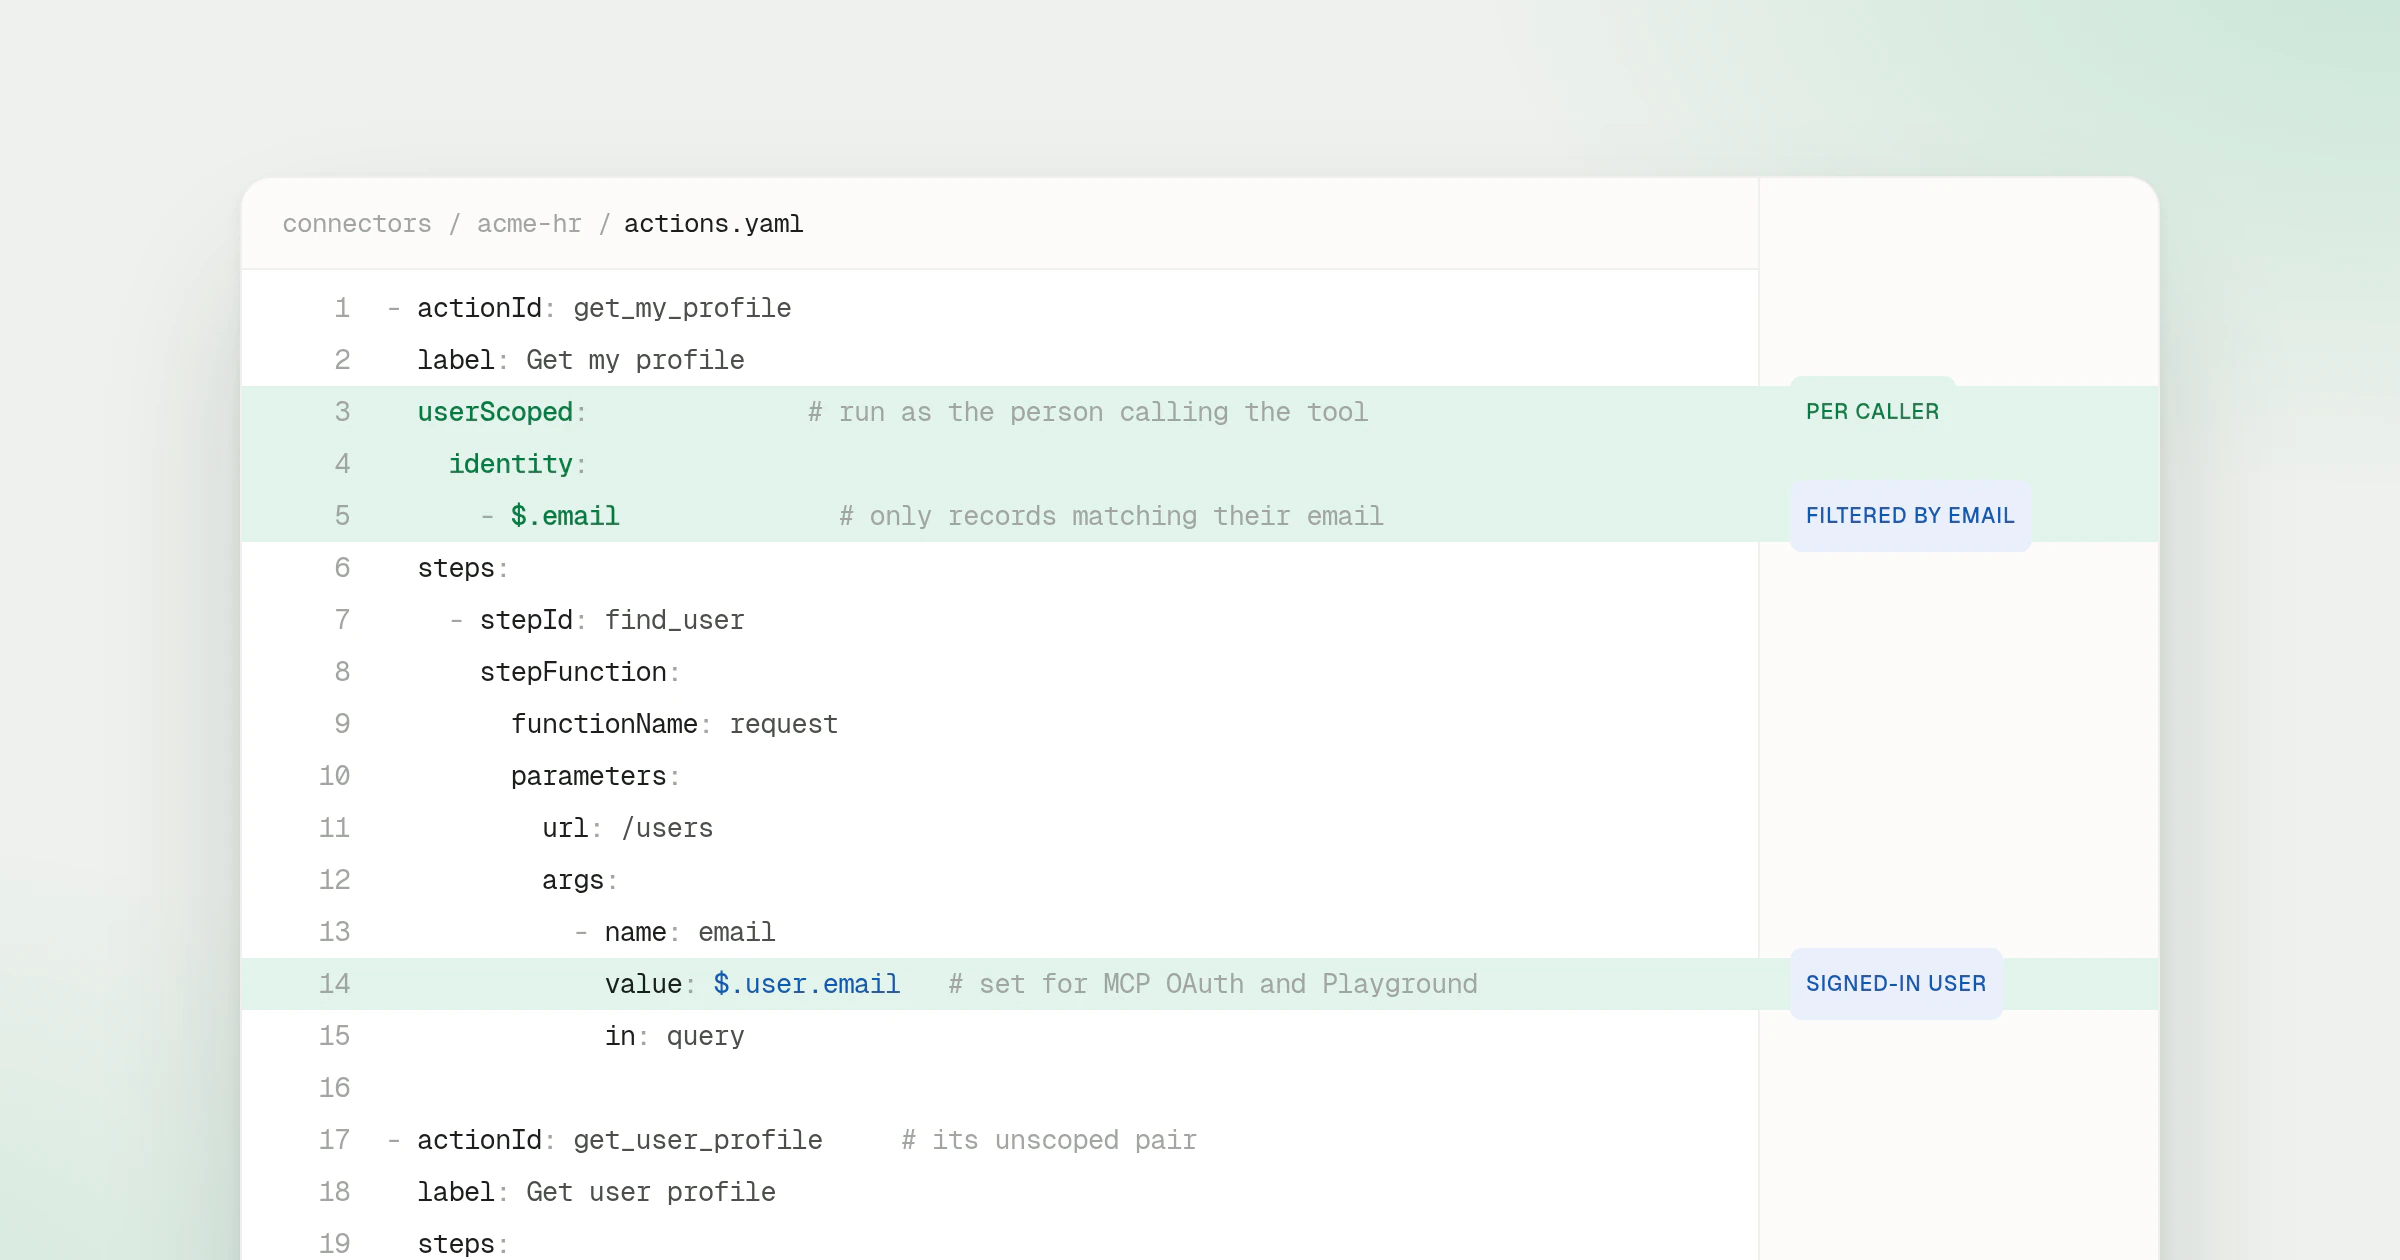
The connector YAML reference now explains userScoped actions, which answer for the person calling the tool, and what $.user holds for each way of calling.
Read about userScoped connector actions
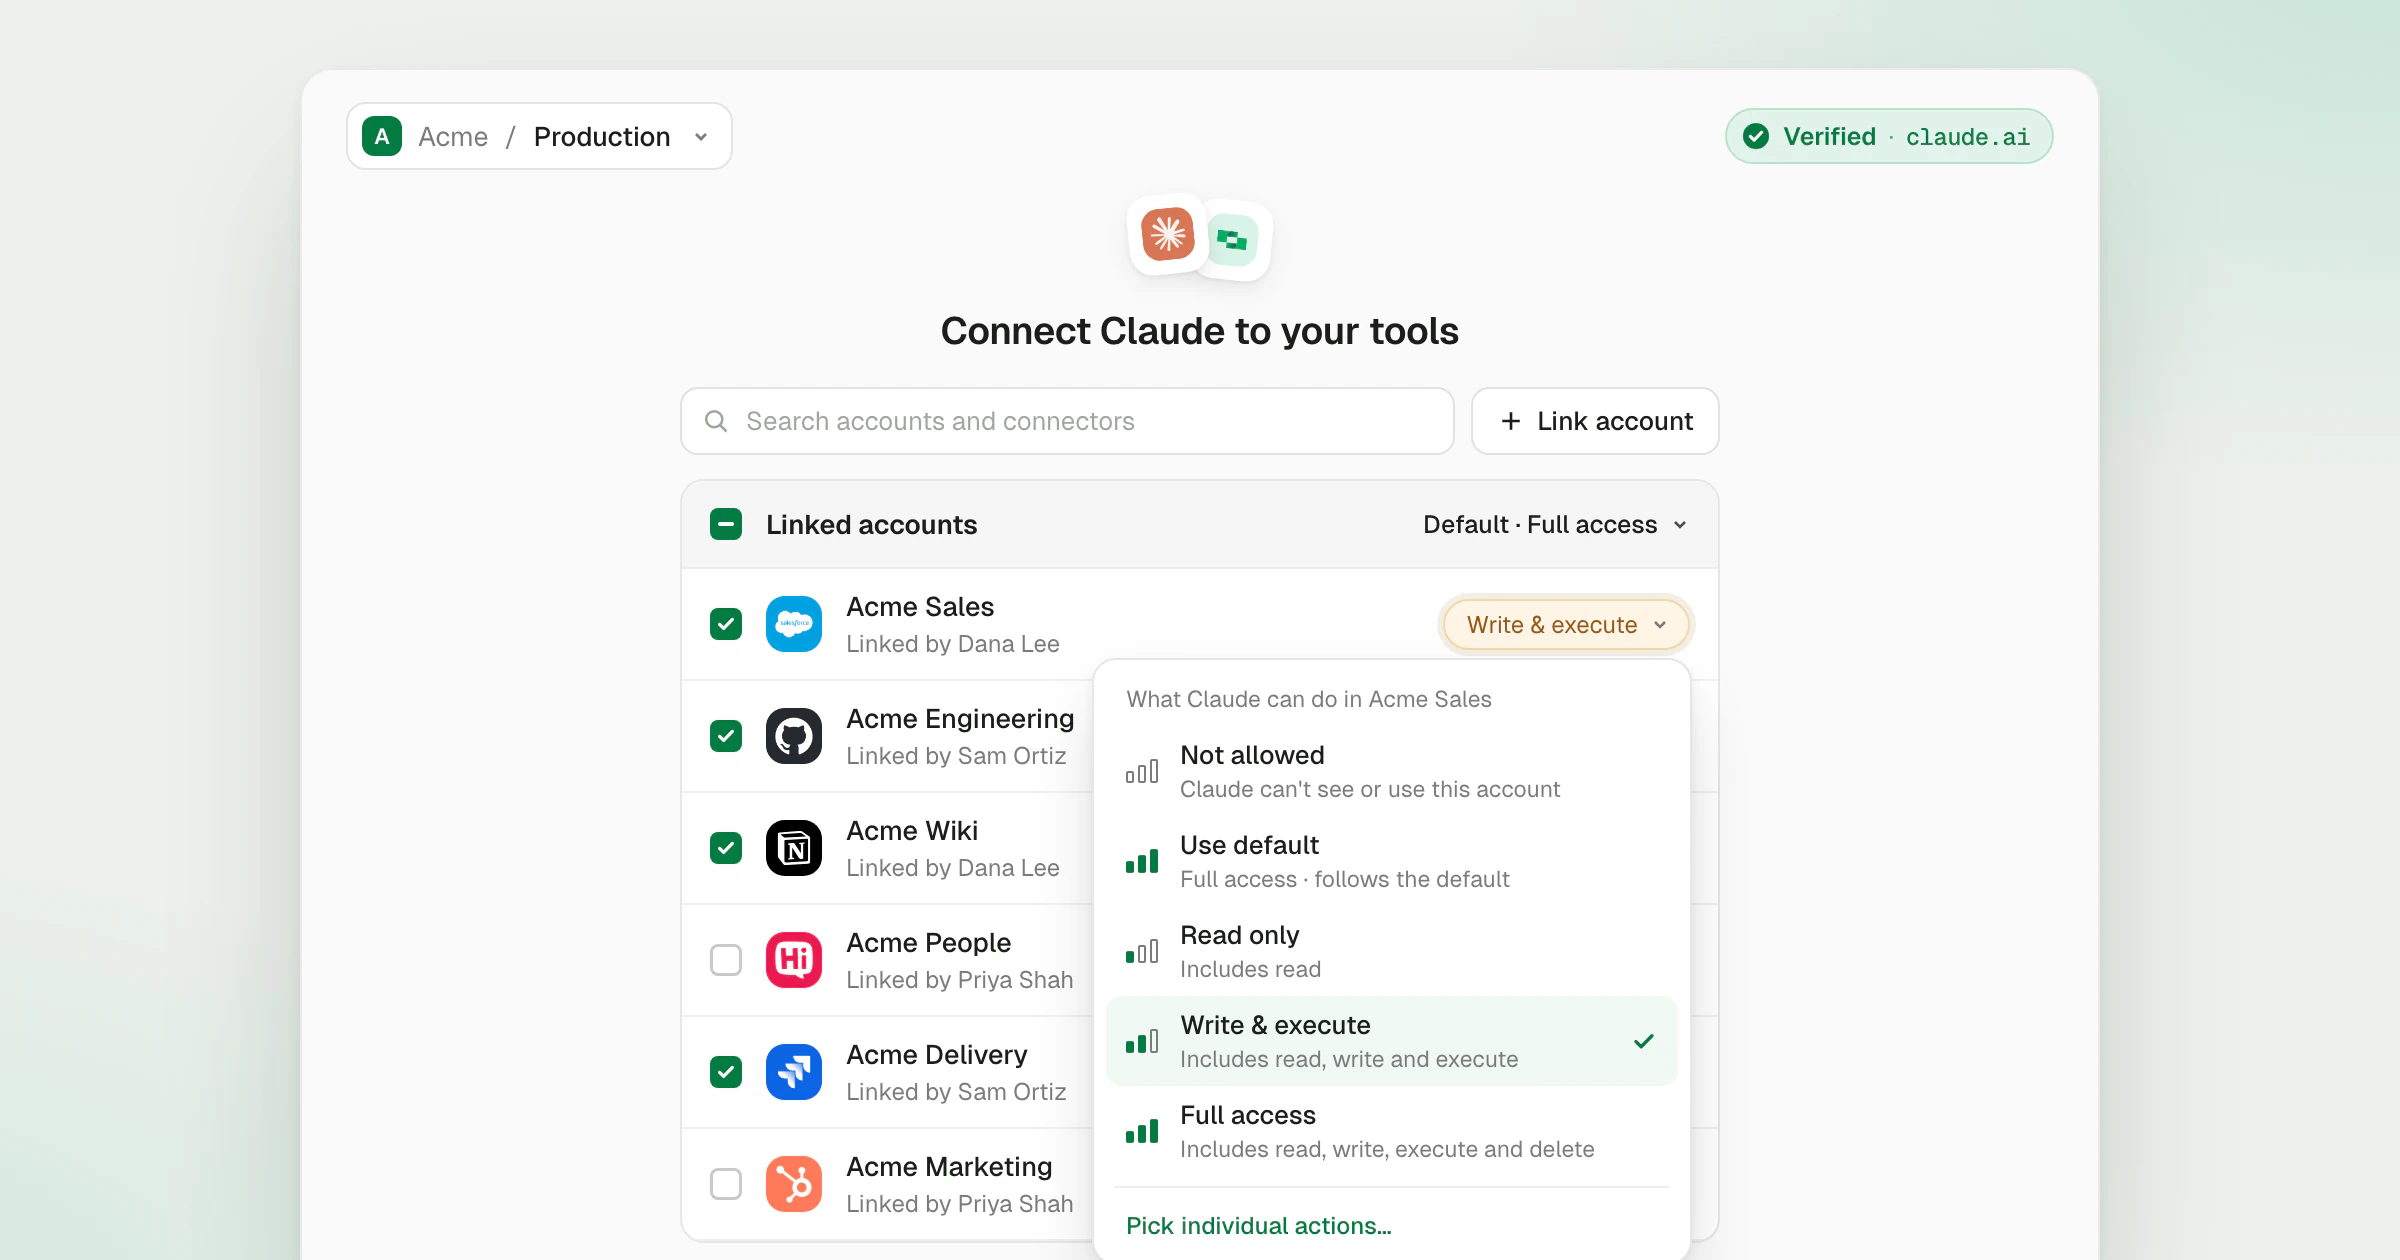
The MCP consent page now sets read, write or delete access per account, links accounts in place, applies access to your other AI apps and shows whether StackOne has verified the app.
Read about MCP consent page
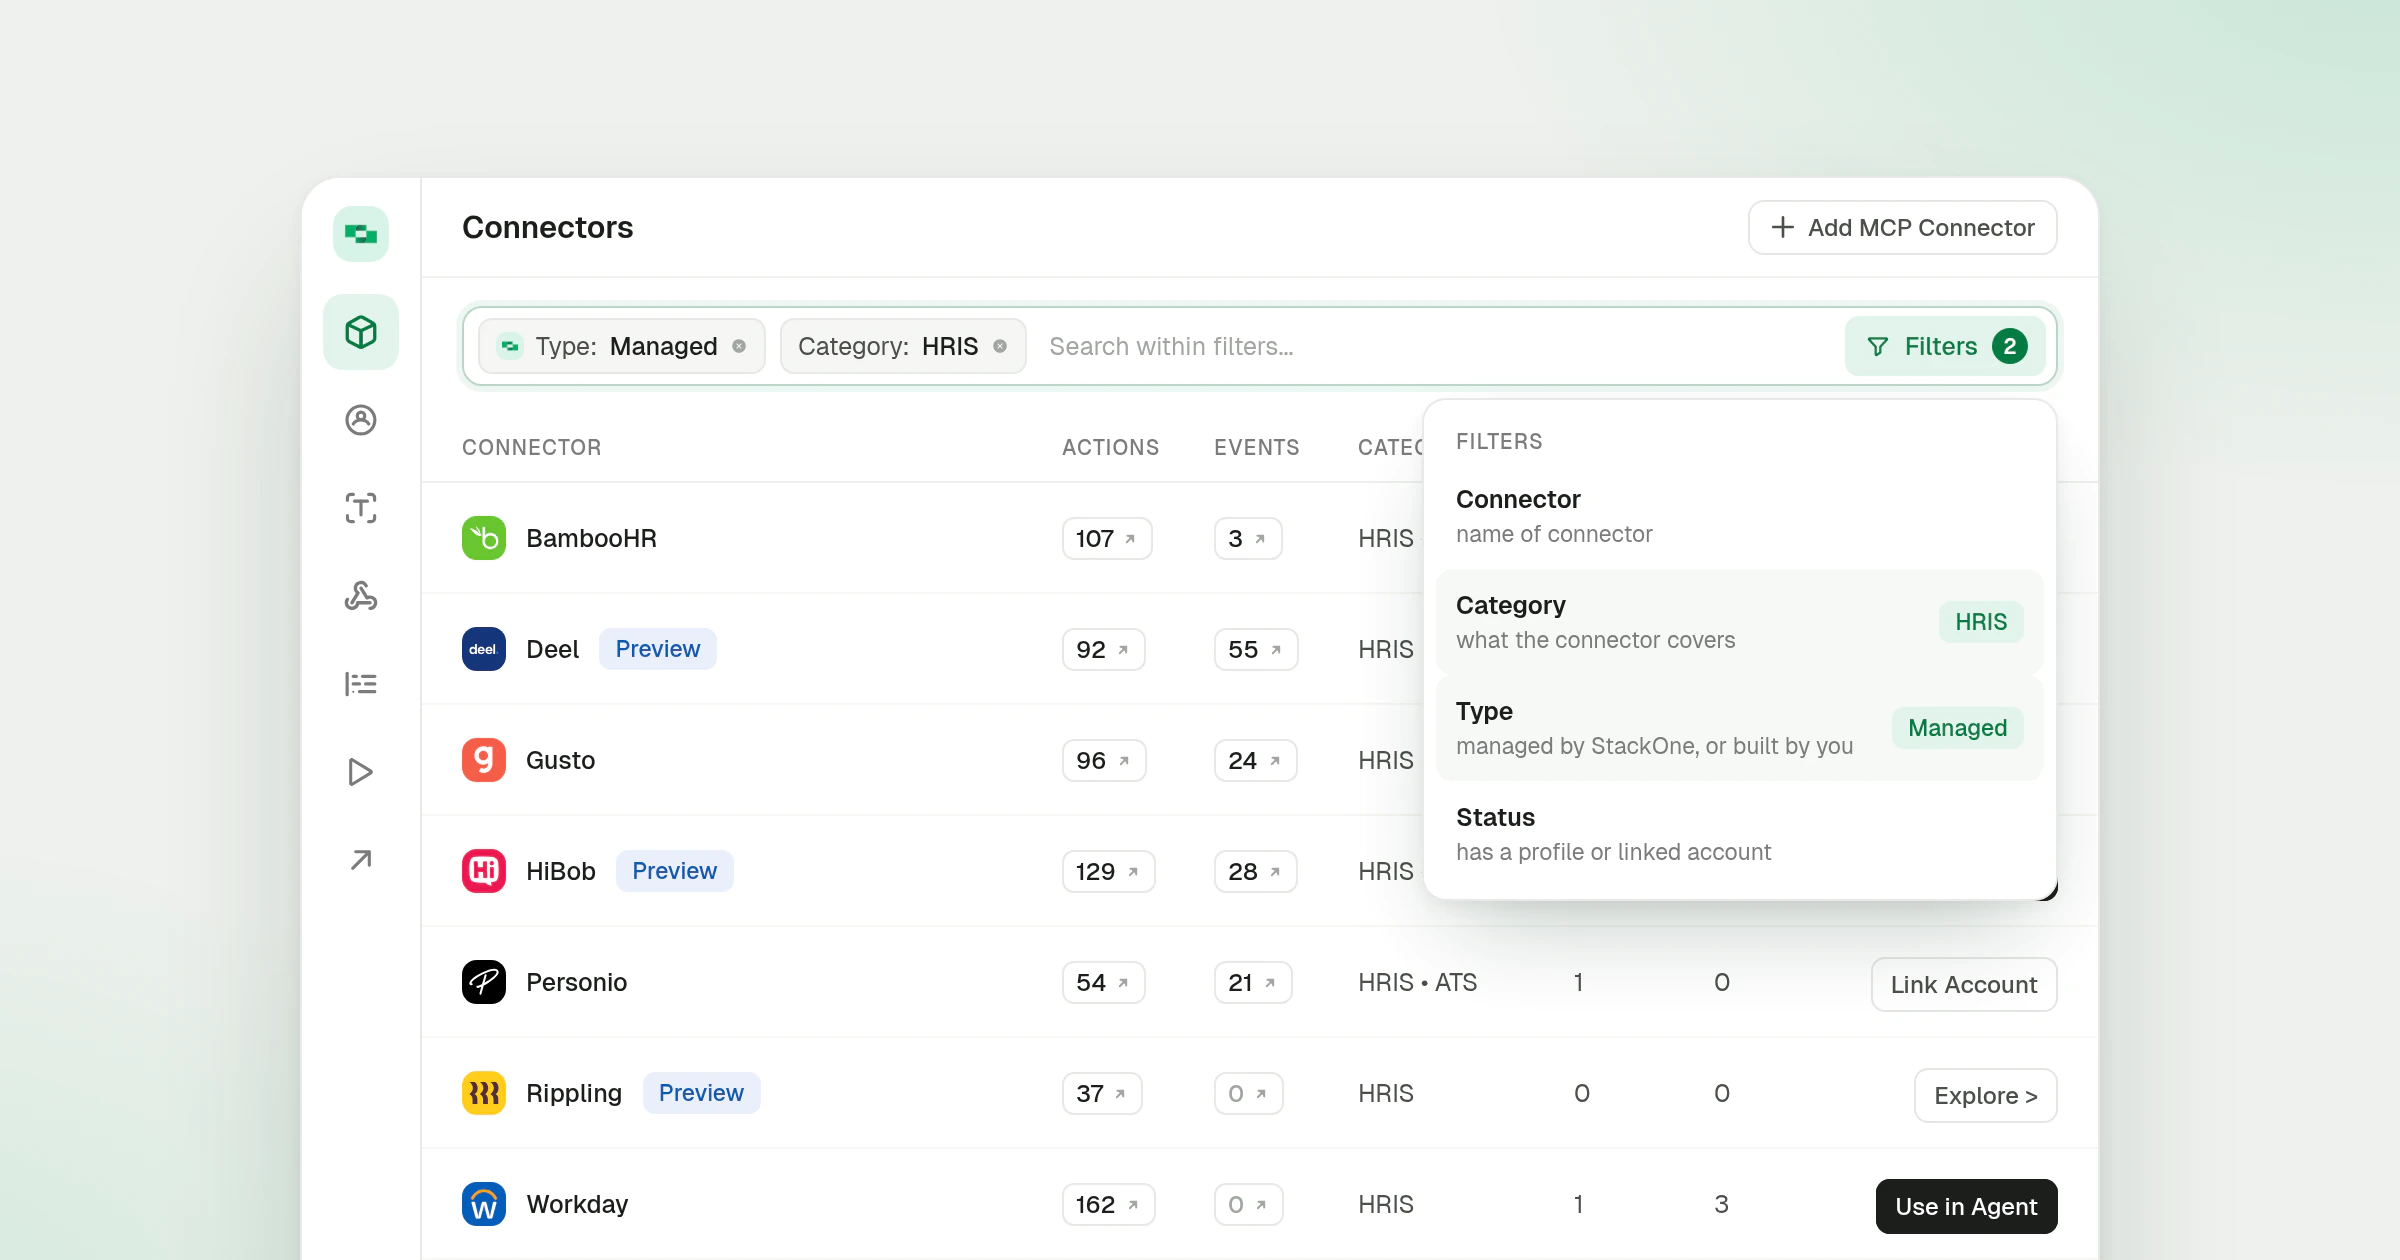
The Connectors page now searches and filters from one field, with a Type filter for custom connectors, chips with logos and filters kept in the URL.
Read about Connectors page filters
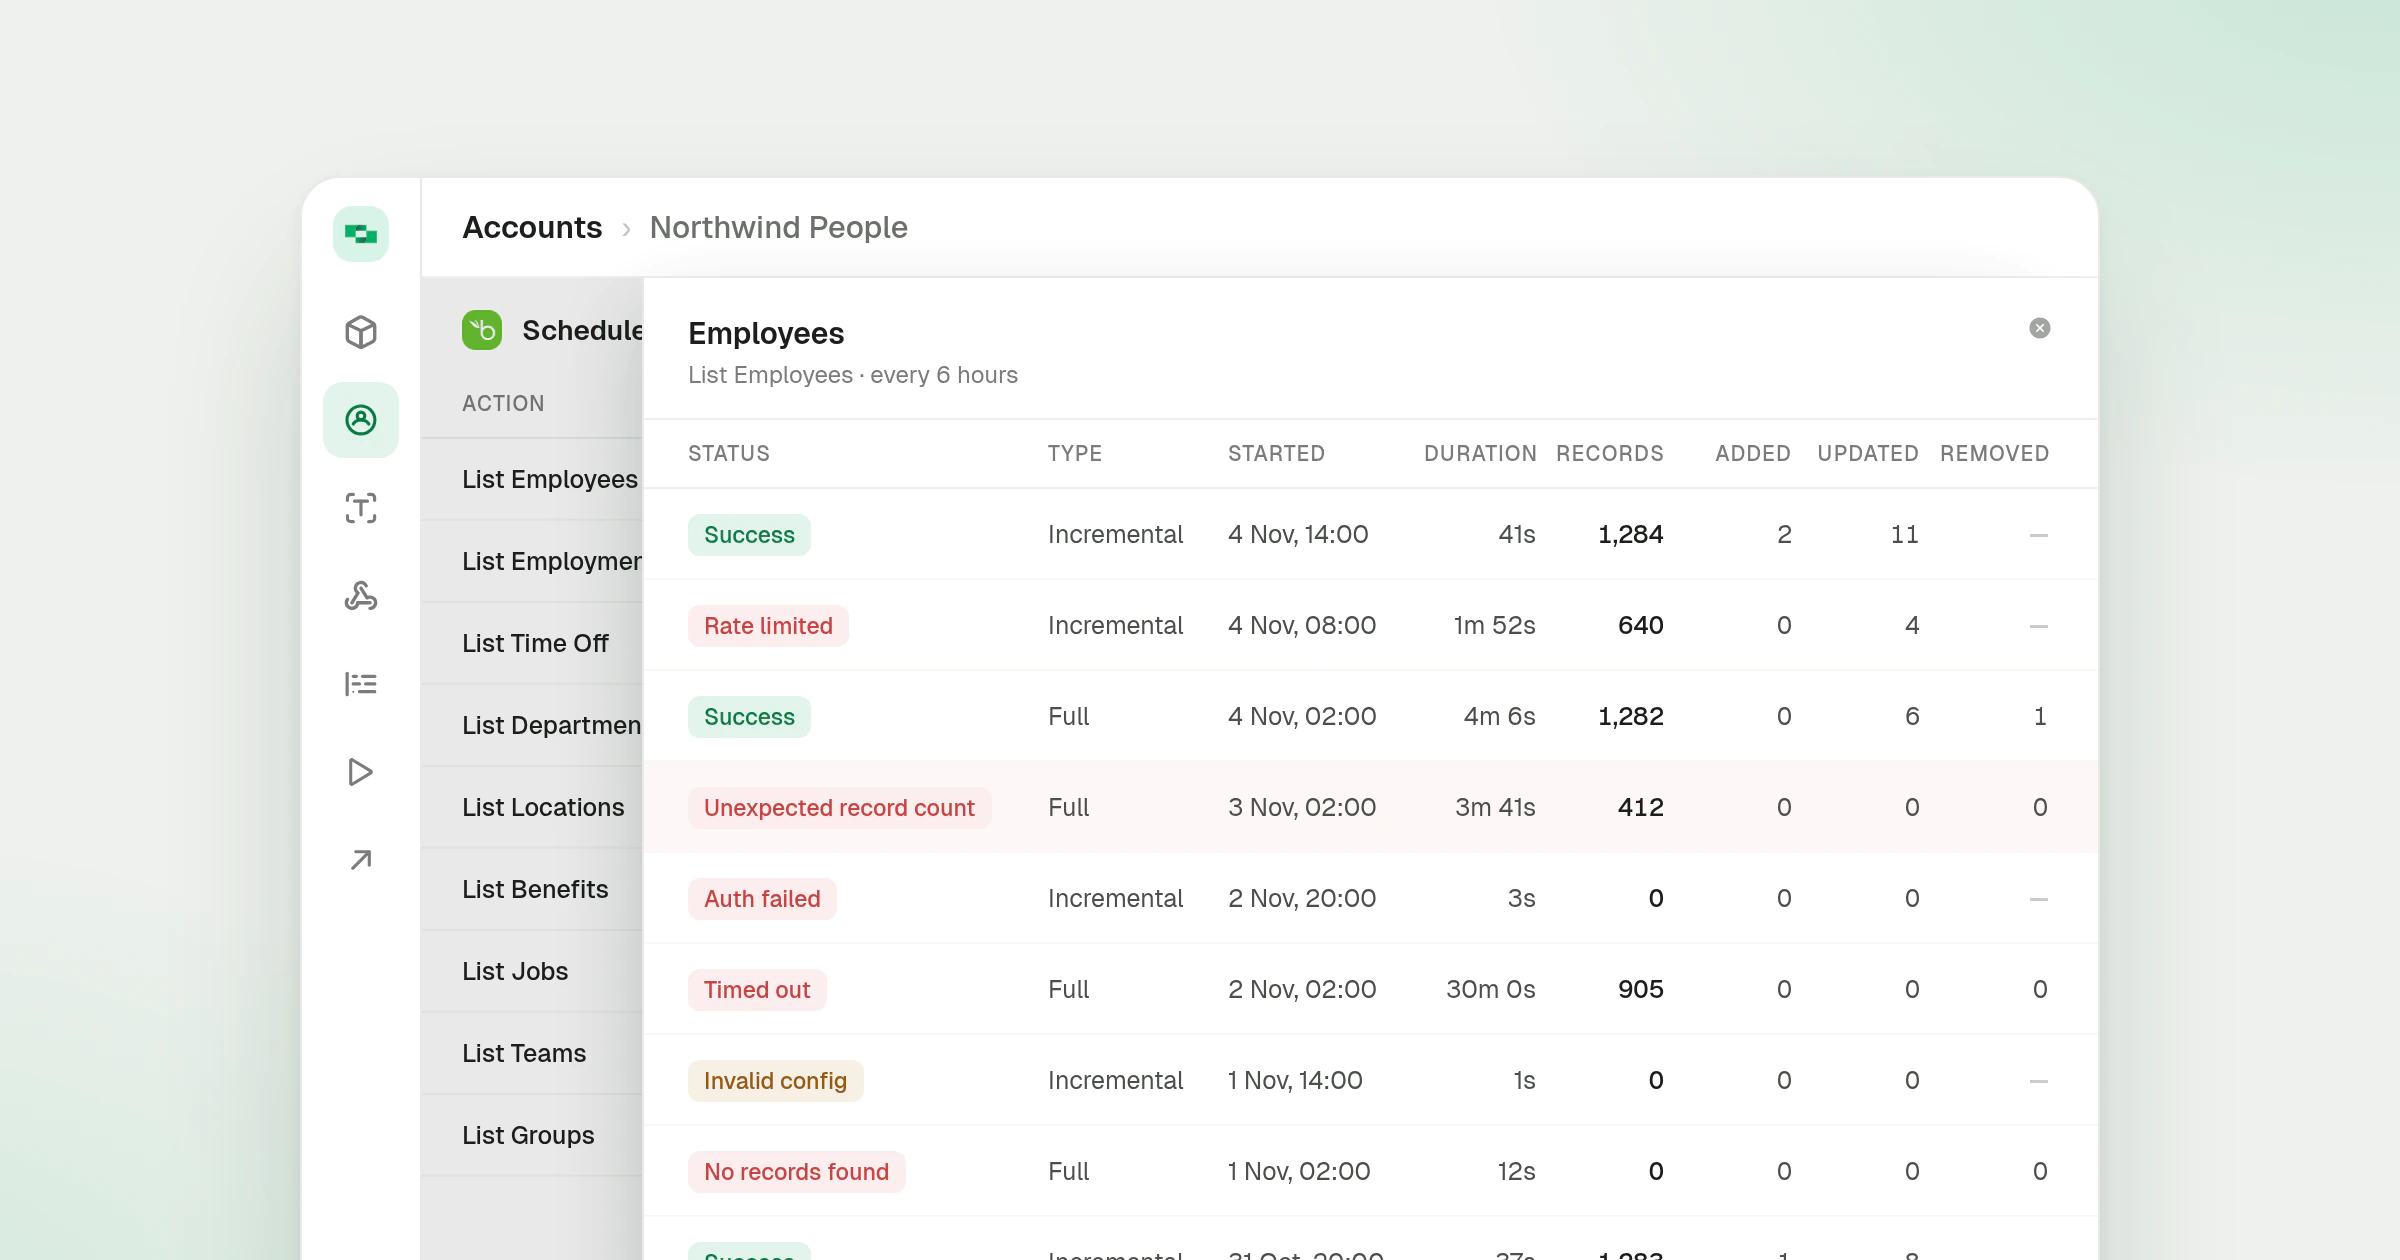
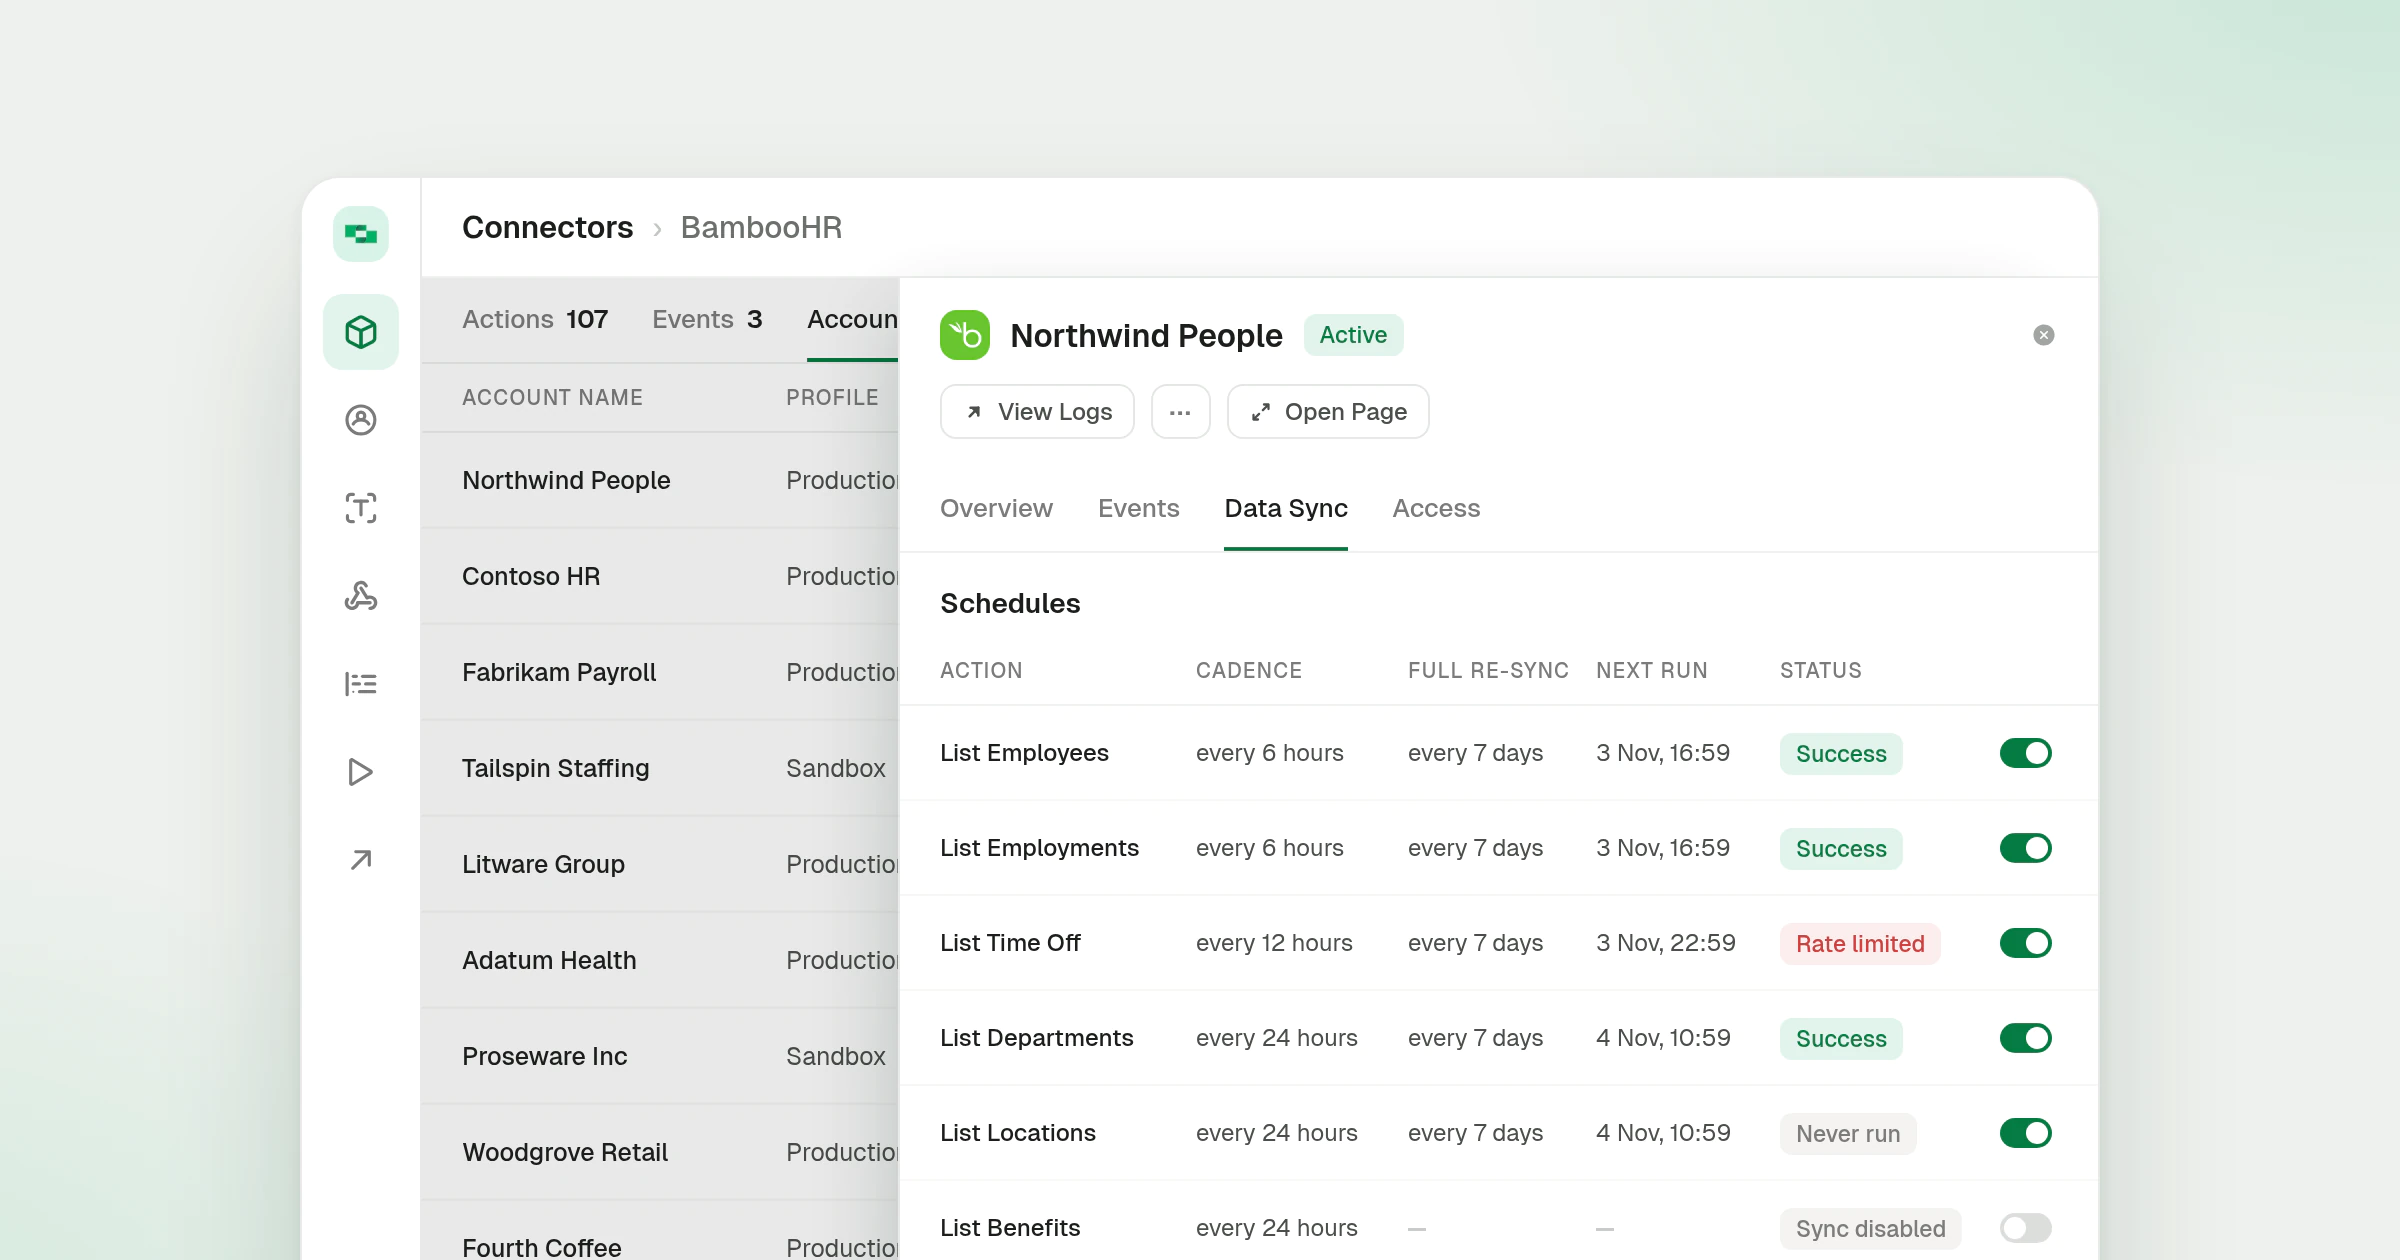
The Data Sync docs now list every run failure status, explain when a full run is held for its record count and give the limits a plan can change.
Read about Data Sync run statuses
Clicking an account on a connector's Accounts tab opens it in a side panel with the account page's tabs and actions, so you stay on the connector.
Read about Account side panel
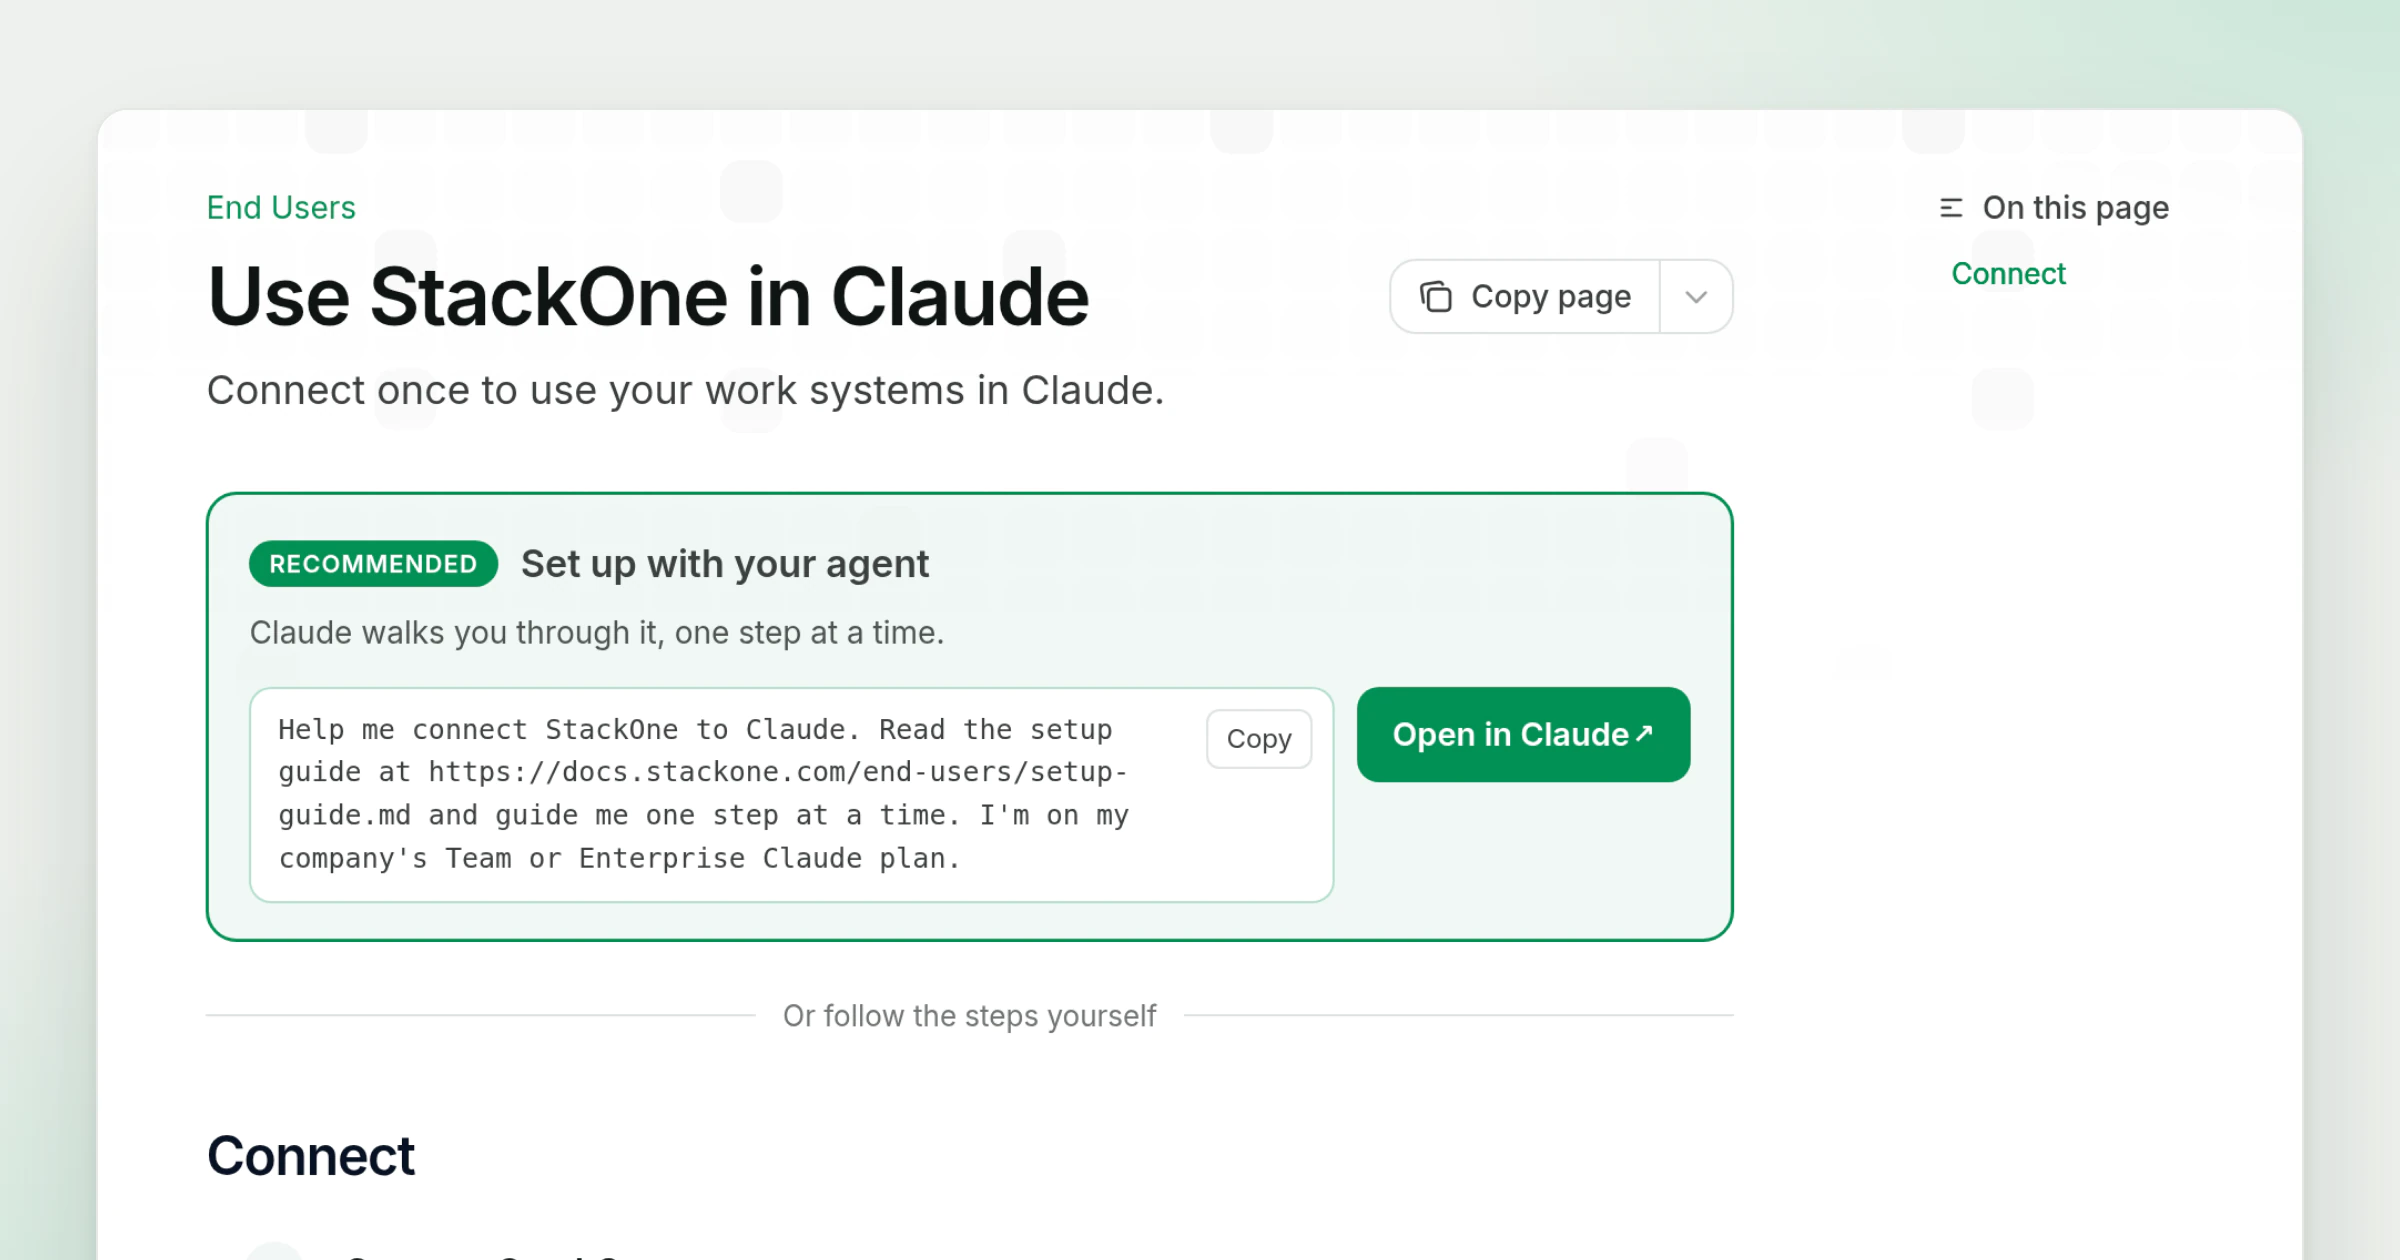
A new docs page shows end users how to connect StackOne to Claude, starting from an Open in Claude button that walks them through each setup step.
Read about StackOne in Claude
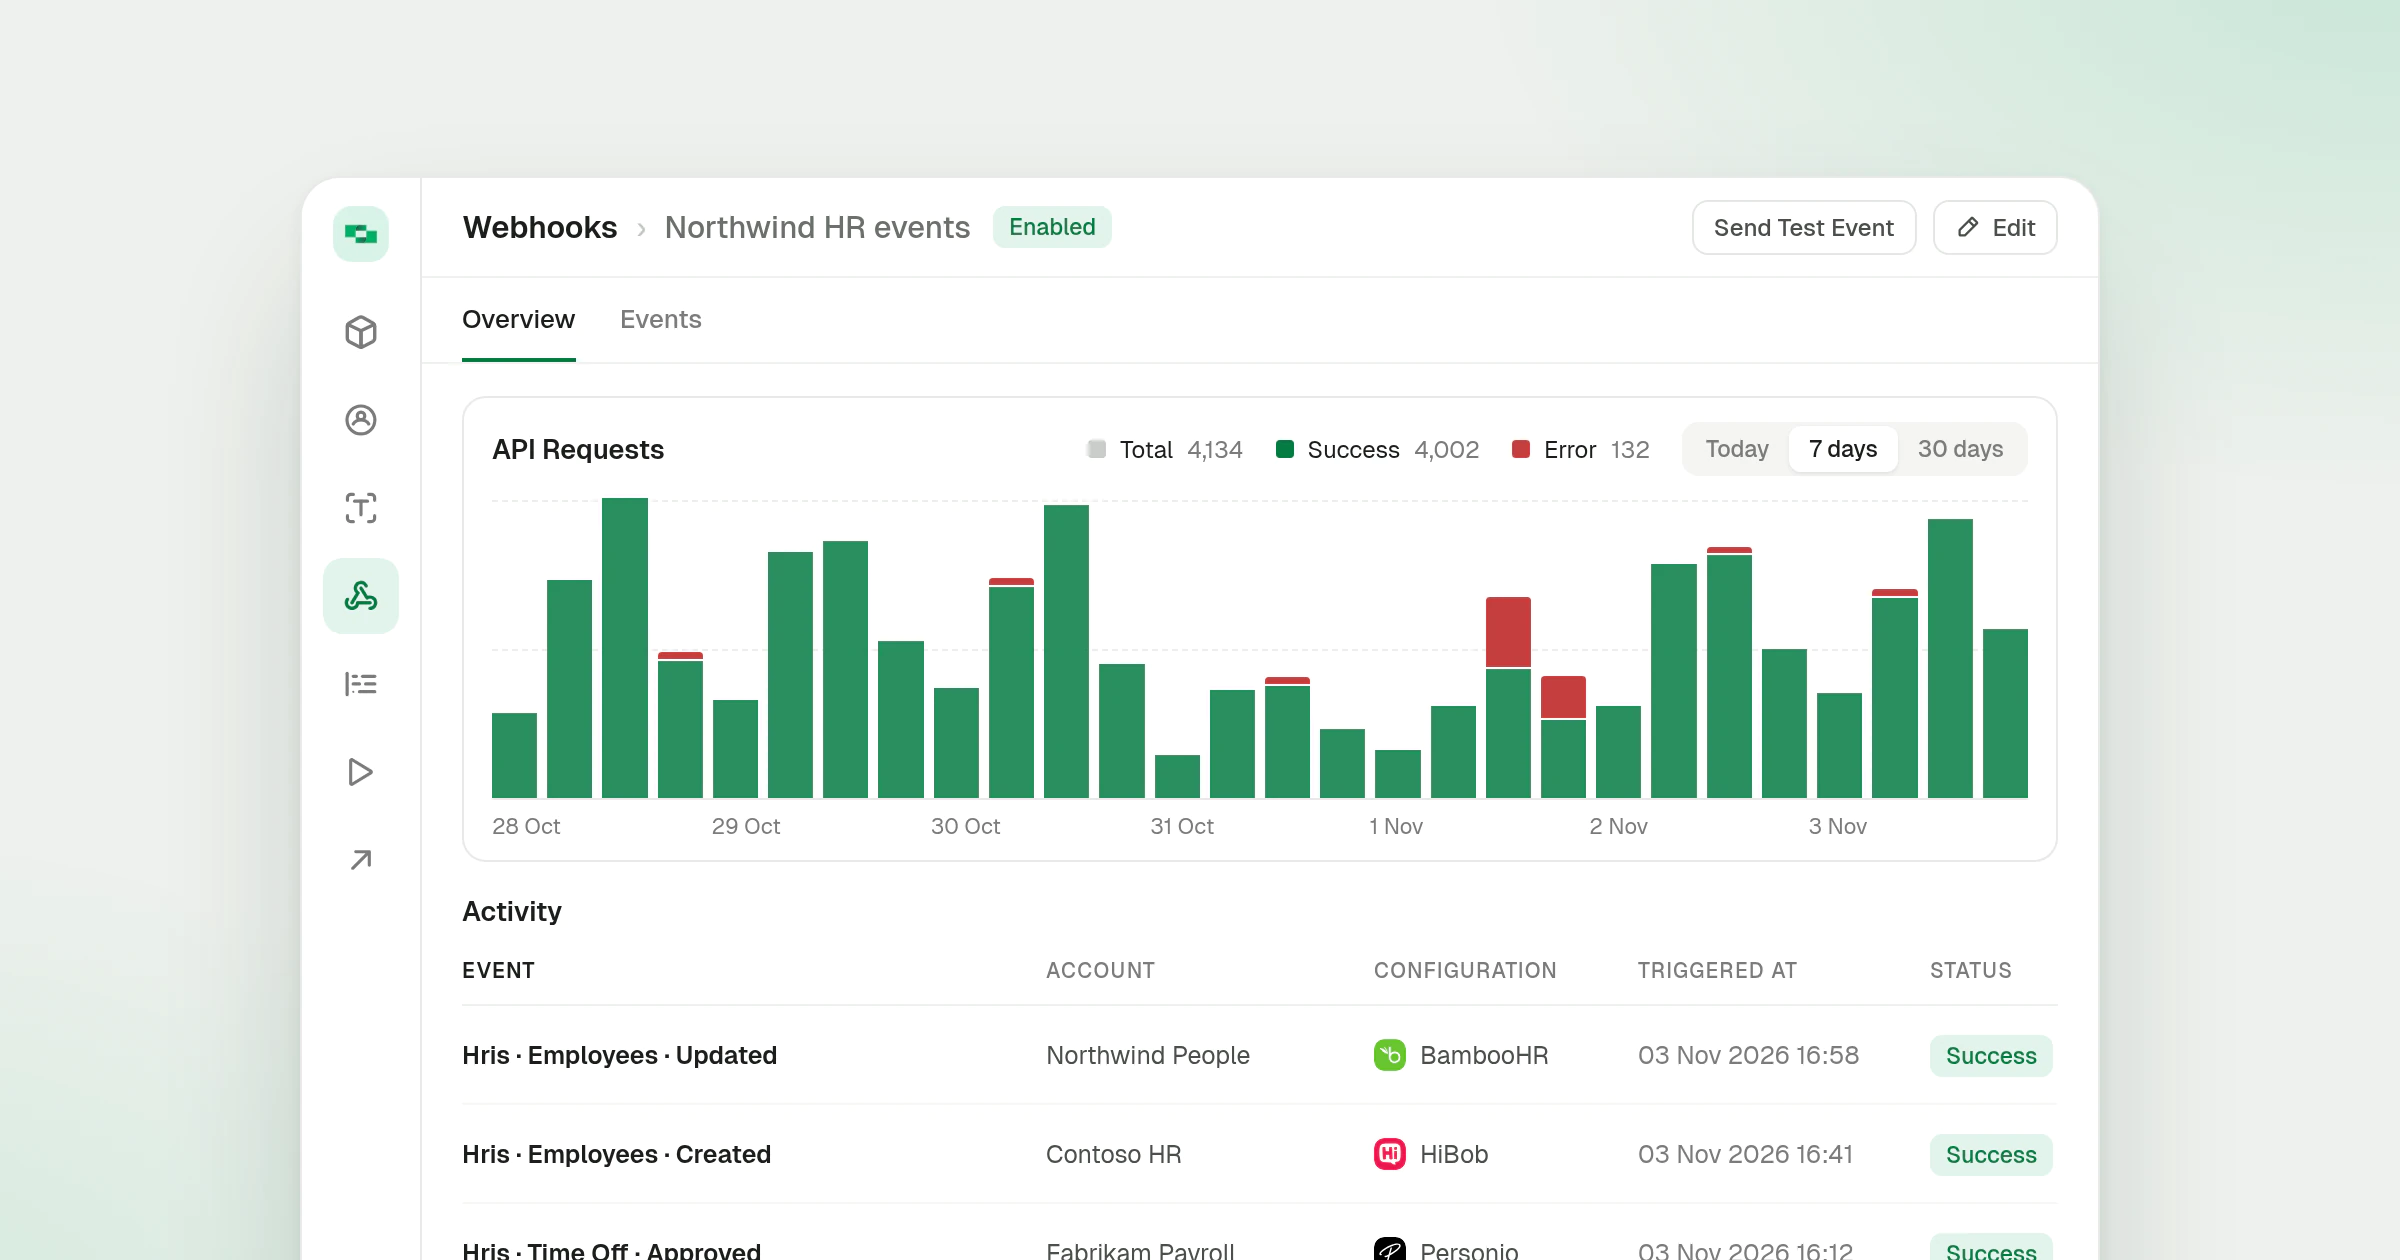
The Webhooks list and detail pages are rebuilt. The Overview chart switches between Today, 7 days and 30 days, and failed deliveries show in red.
Read about Webhooks pages
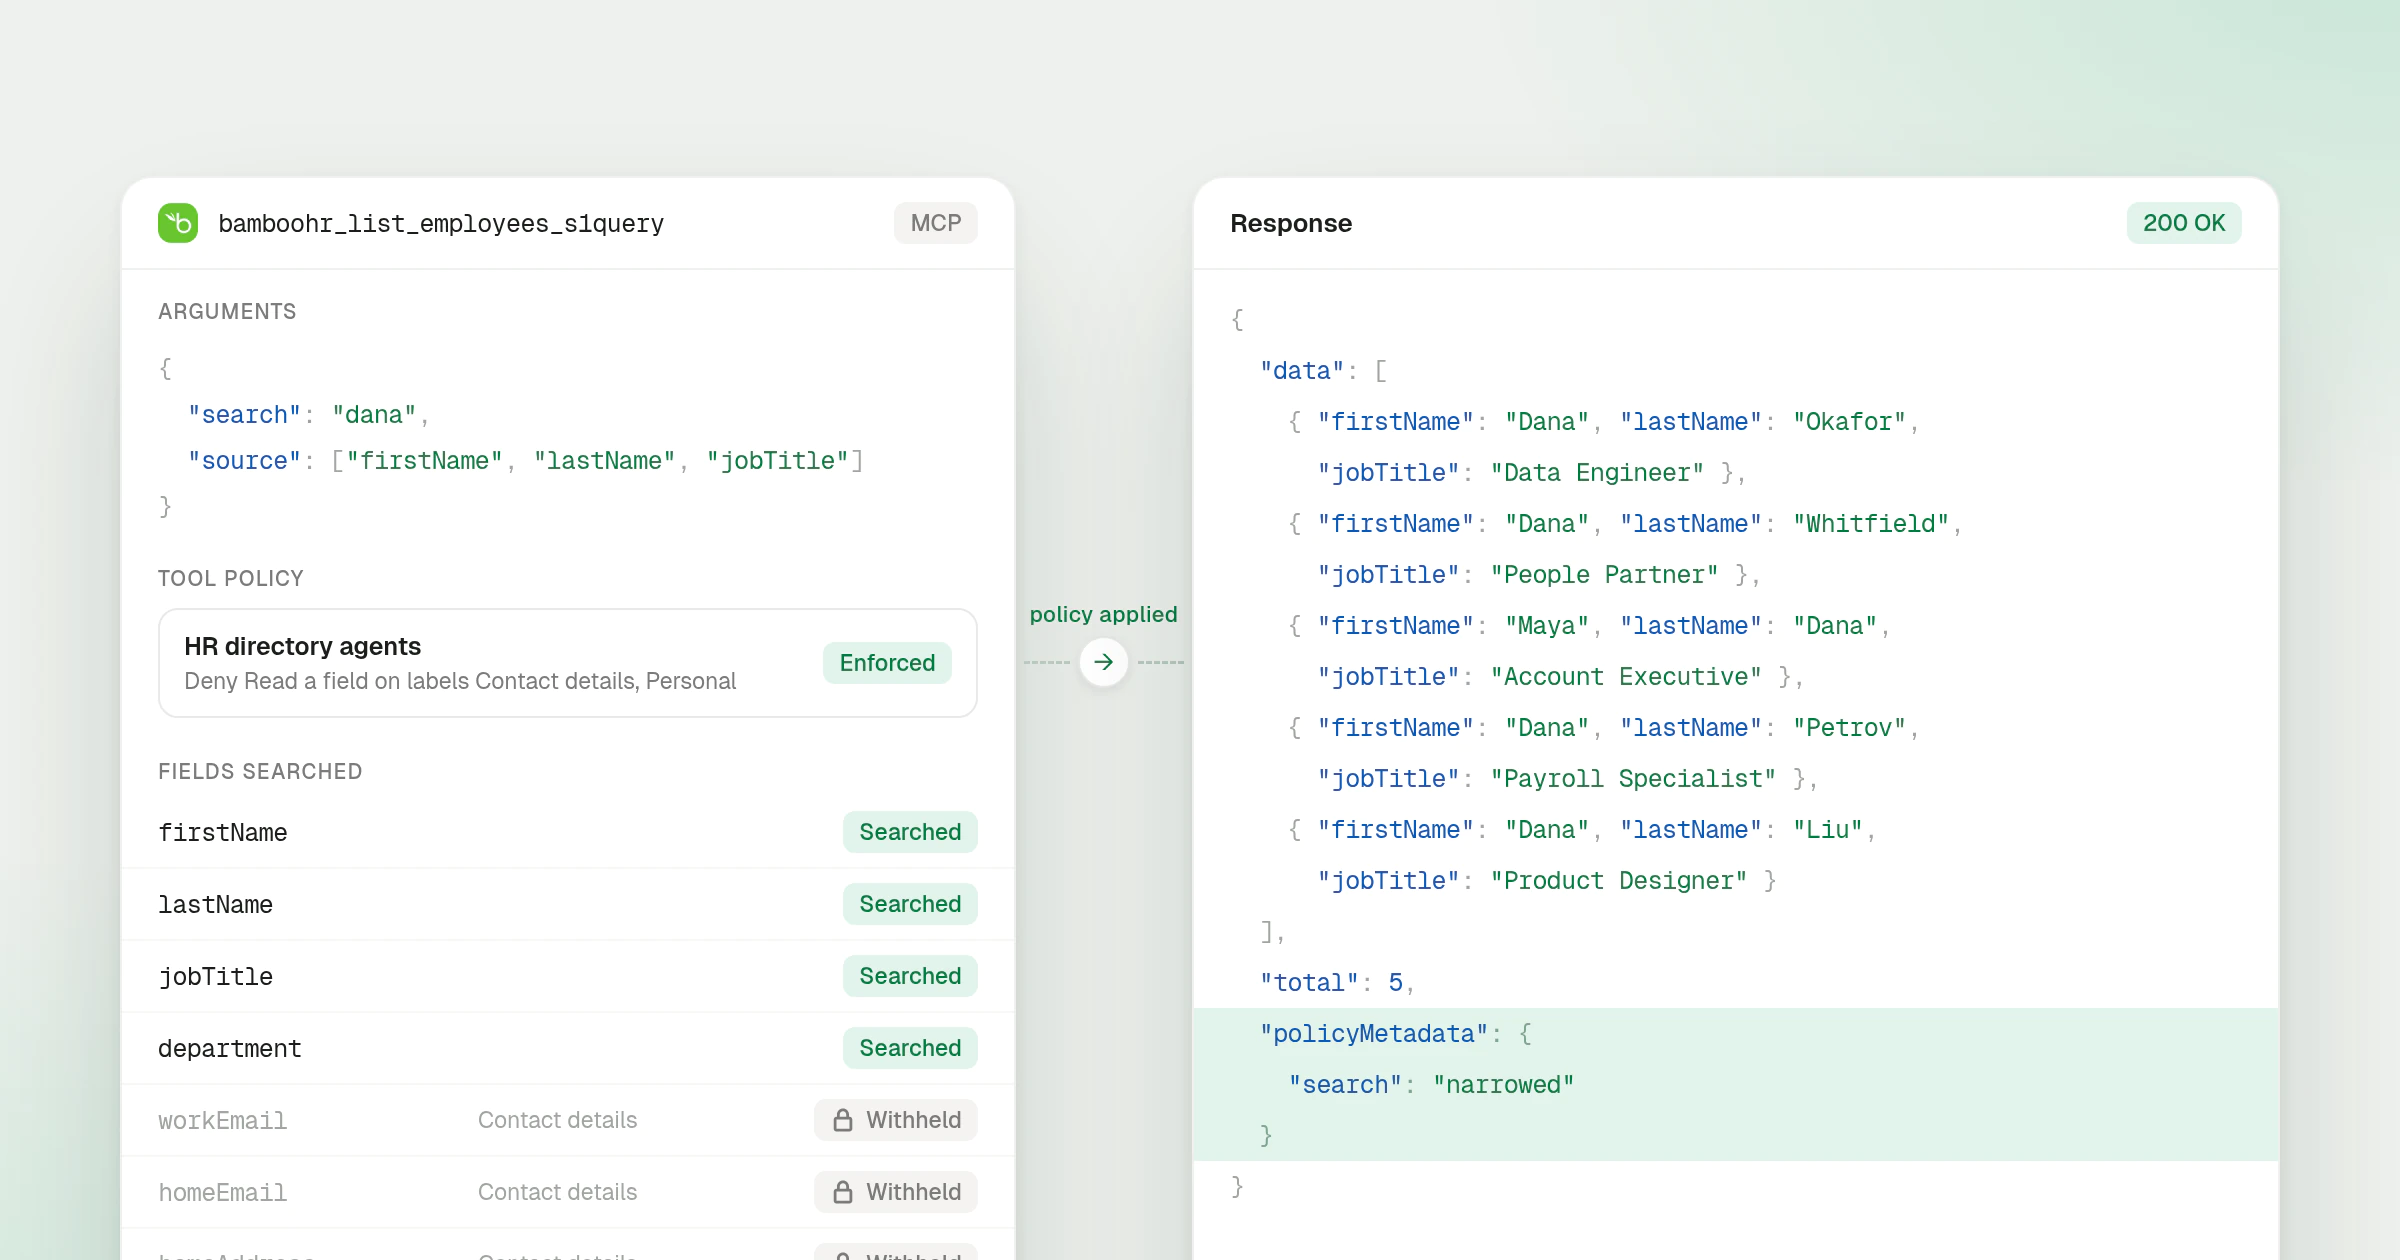
A synced search under a tool policy now runs only over the fields the policy allows, and policyMetadata.search says when the policy narrowed it.
Read about Synced search policies
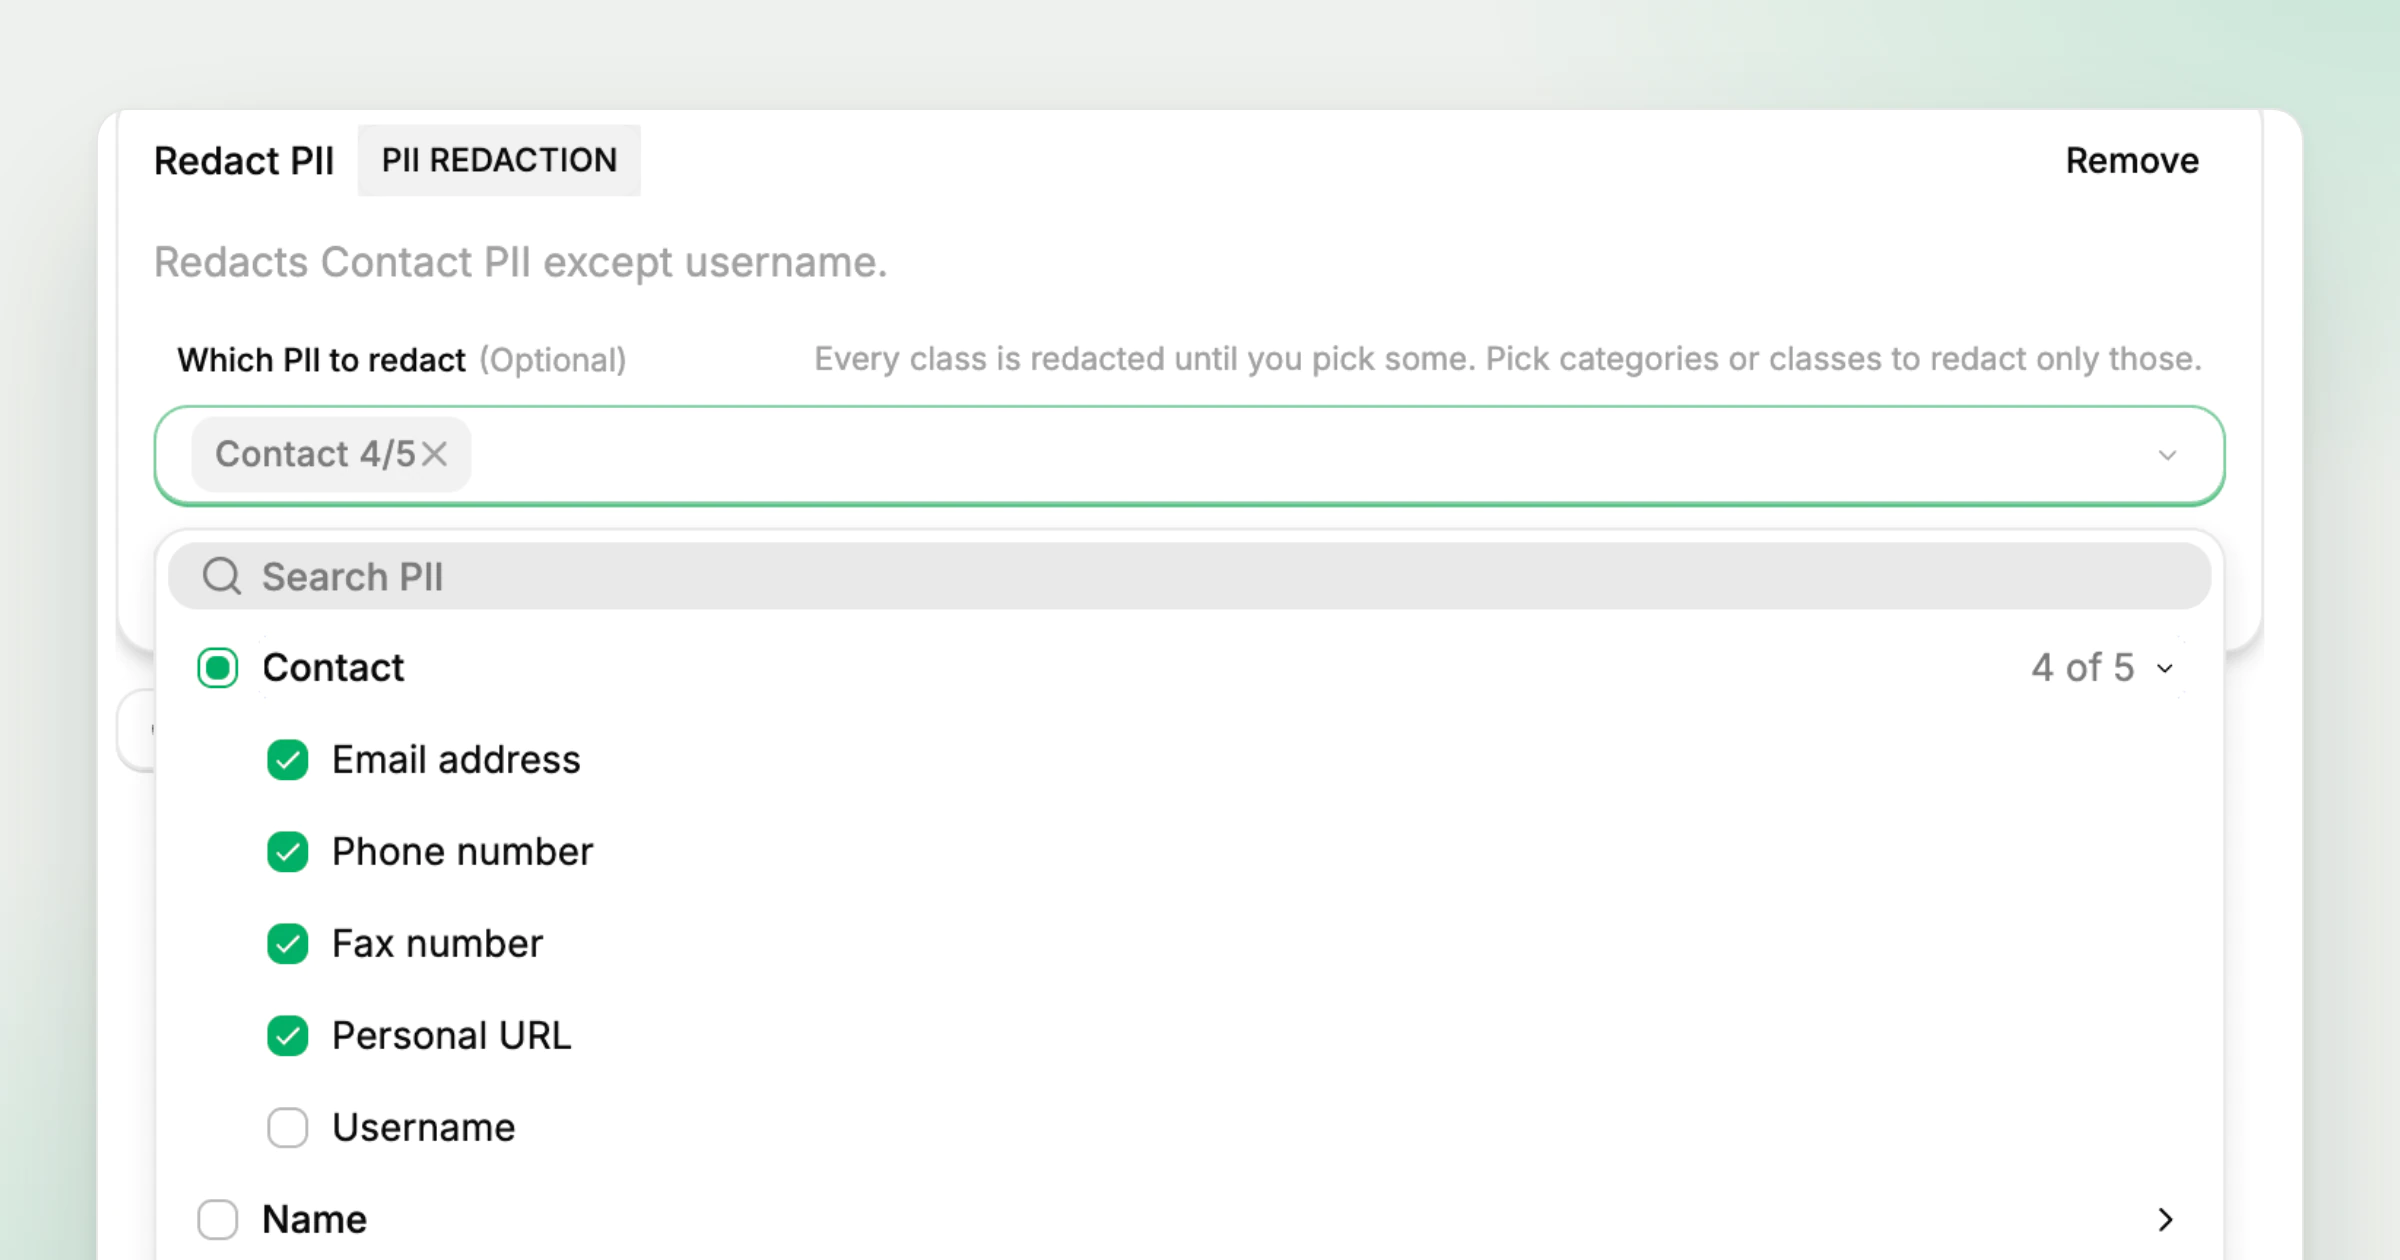
Redact PII rules in Tool Policies now pick from 26 PII classes in 8 categories, and can redact a whole category while keeping named exceptions.
Read about PII redaction categories@stackone/ai 3.1 gives the model one search tool and one execute tool across every account in scope. stackone-ai 3.0 for Python runs every tool over MCP.
Read about StackOne AI SDK
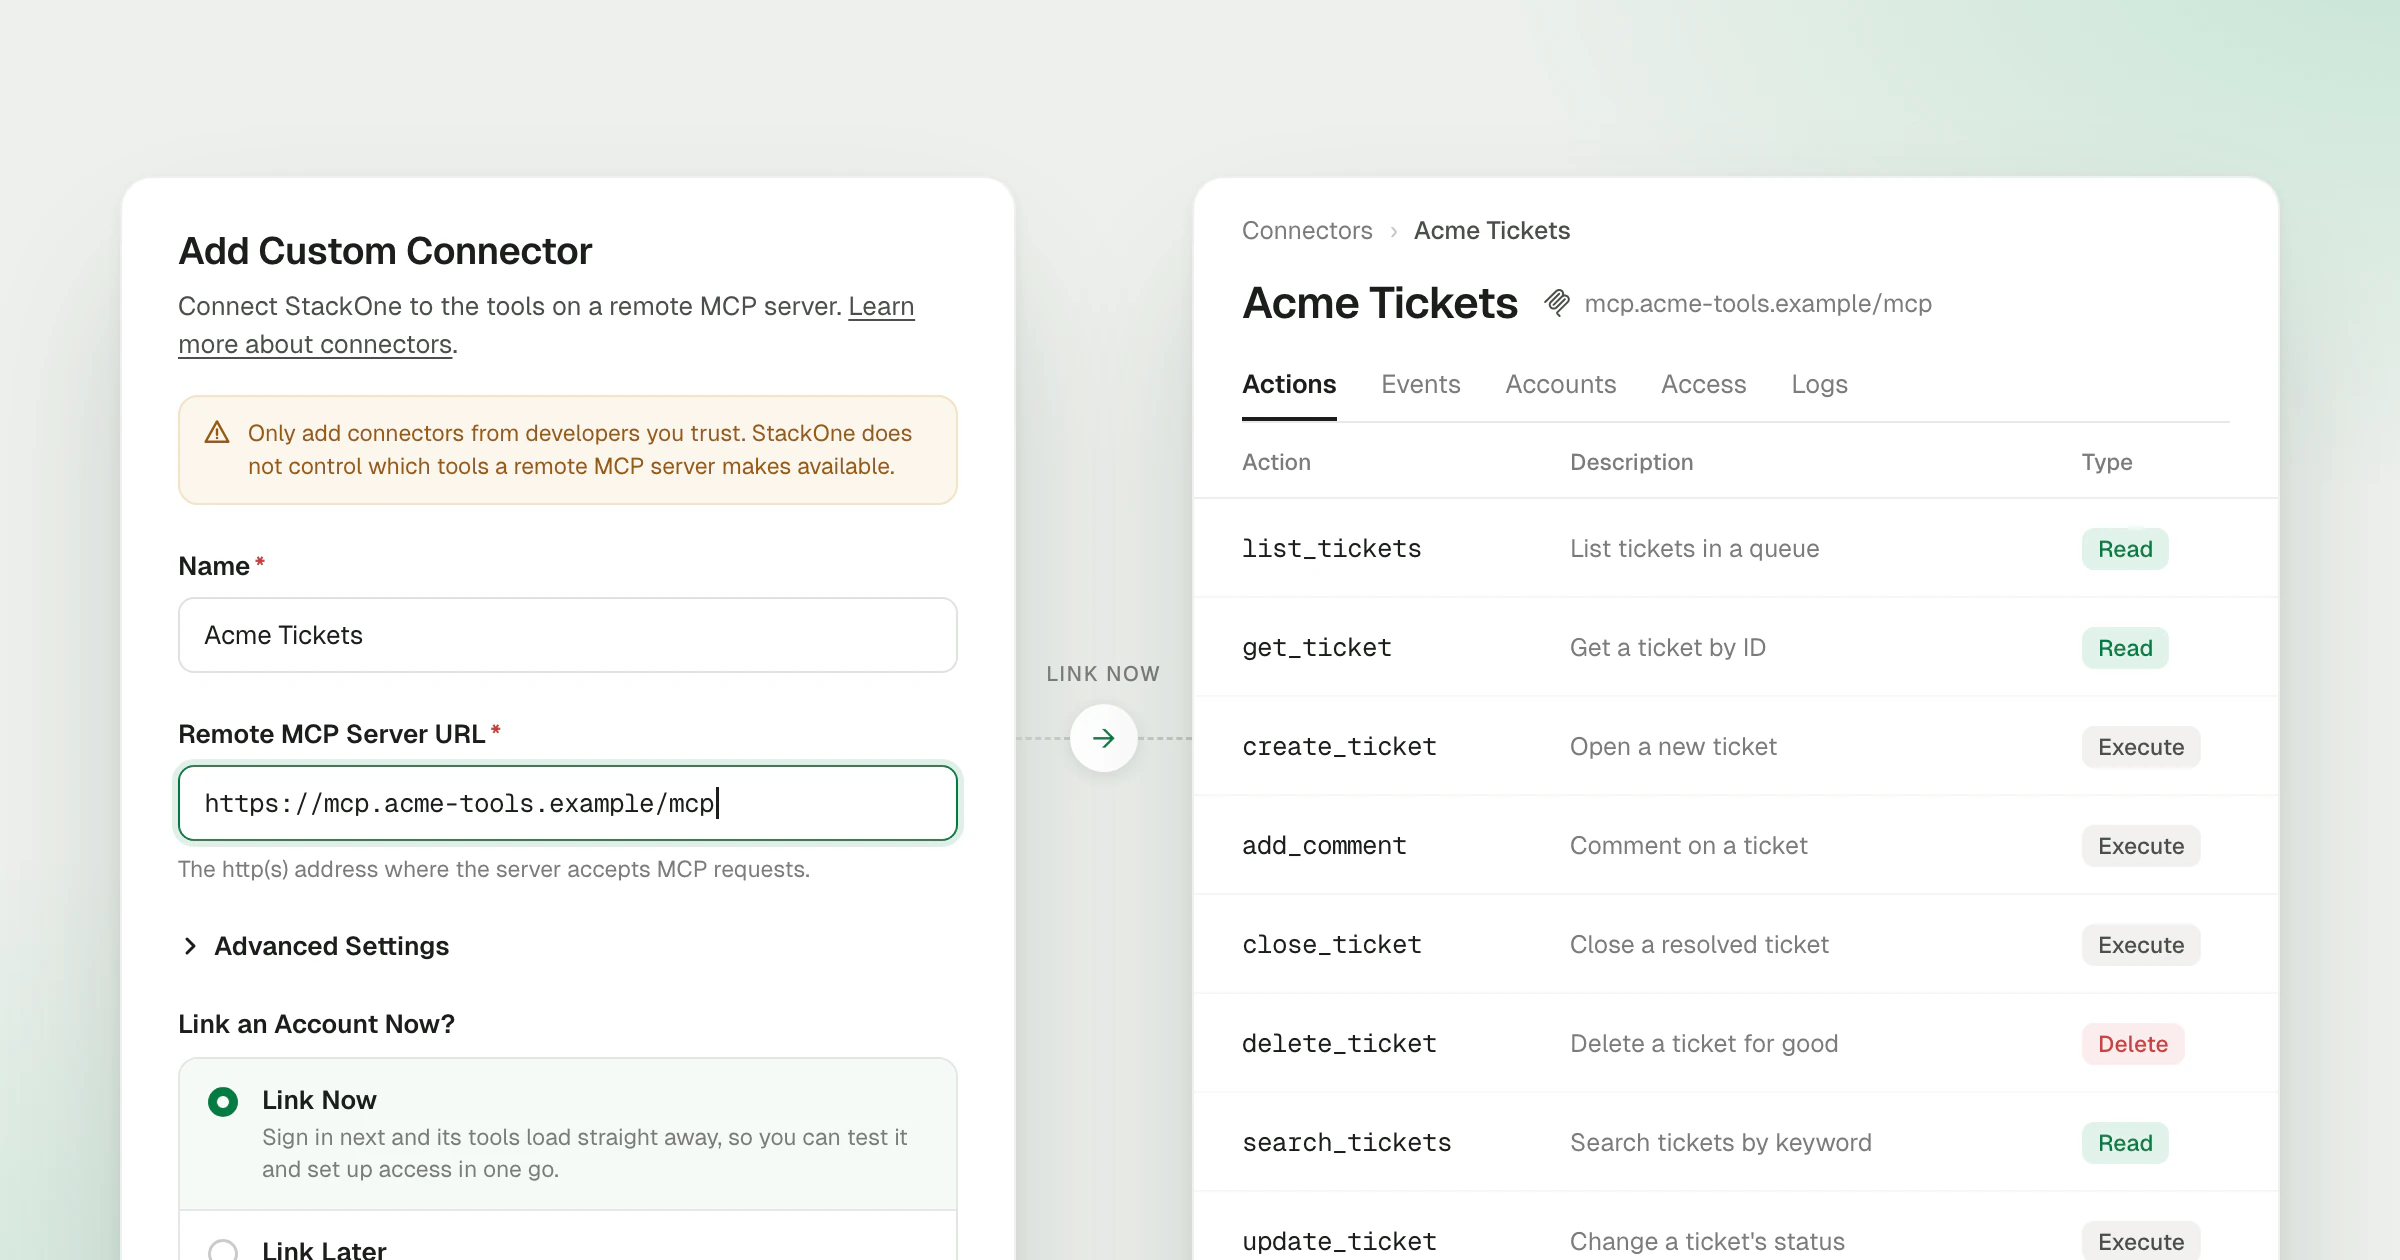
Add any remote MCP server to StackOne by its URL and govern its tools like any connector, with connector profiles, Tool Policies, Defender and logs.
Read about MCP ConnectorsLabel rules in Tool Policies now check the fields an agent writes, and synced reads follow the rules of the action they copy.
Read about Tool Policies writes
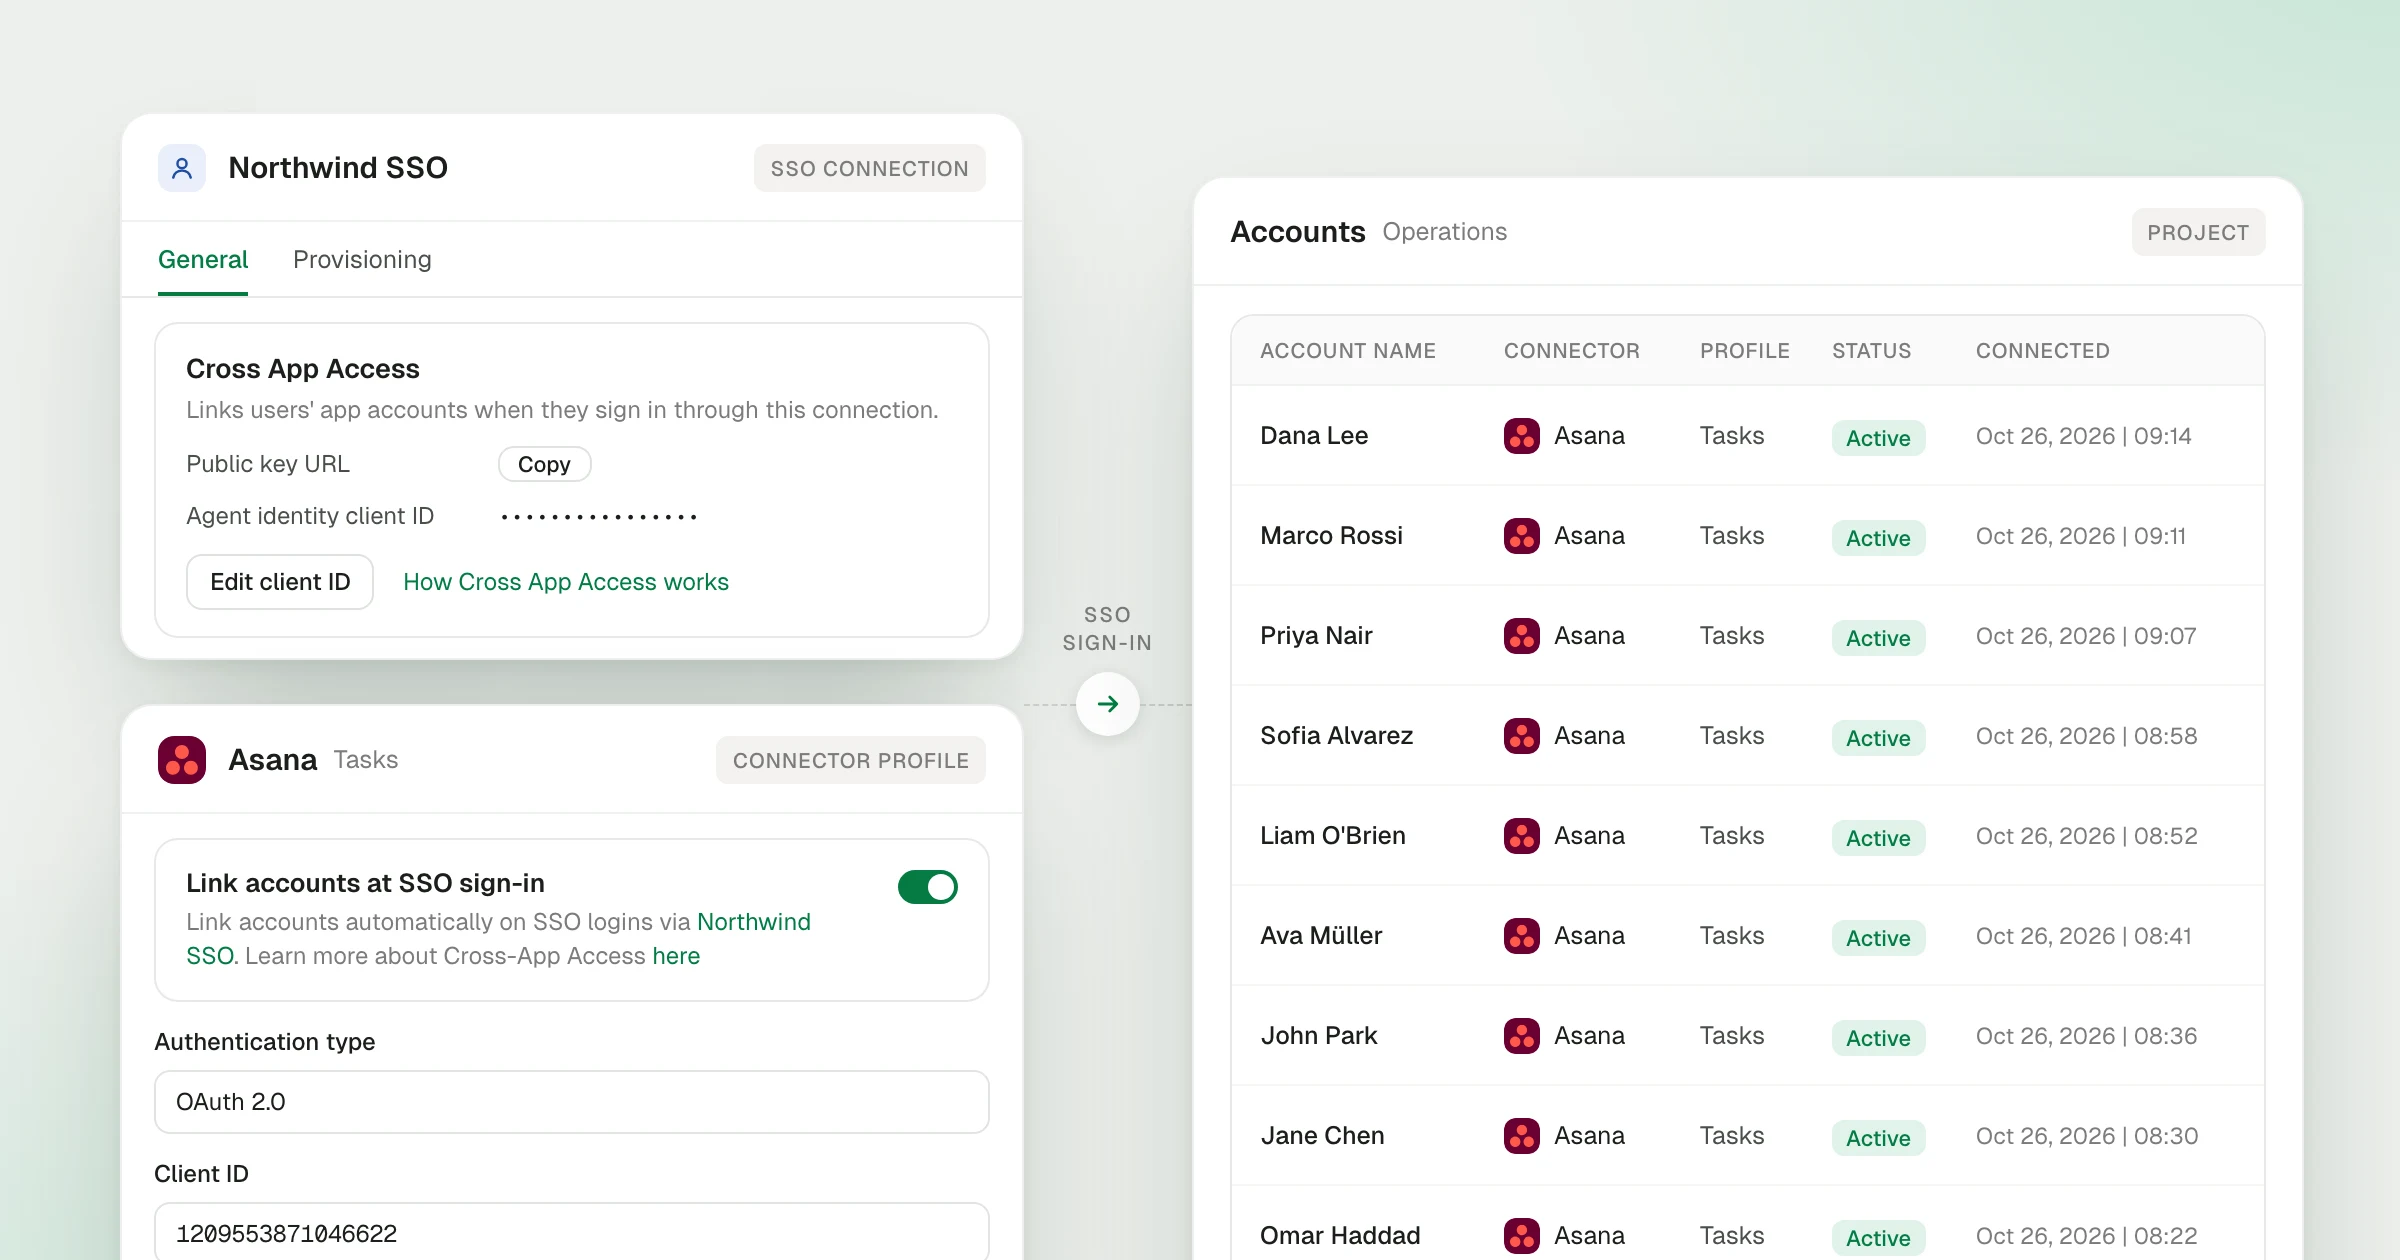
StackOne links each person's apps at SSO sign-in, as your identity provider allows. Works with Okta and other identity providers that support Cross App Access.
Read about Cross App Access
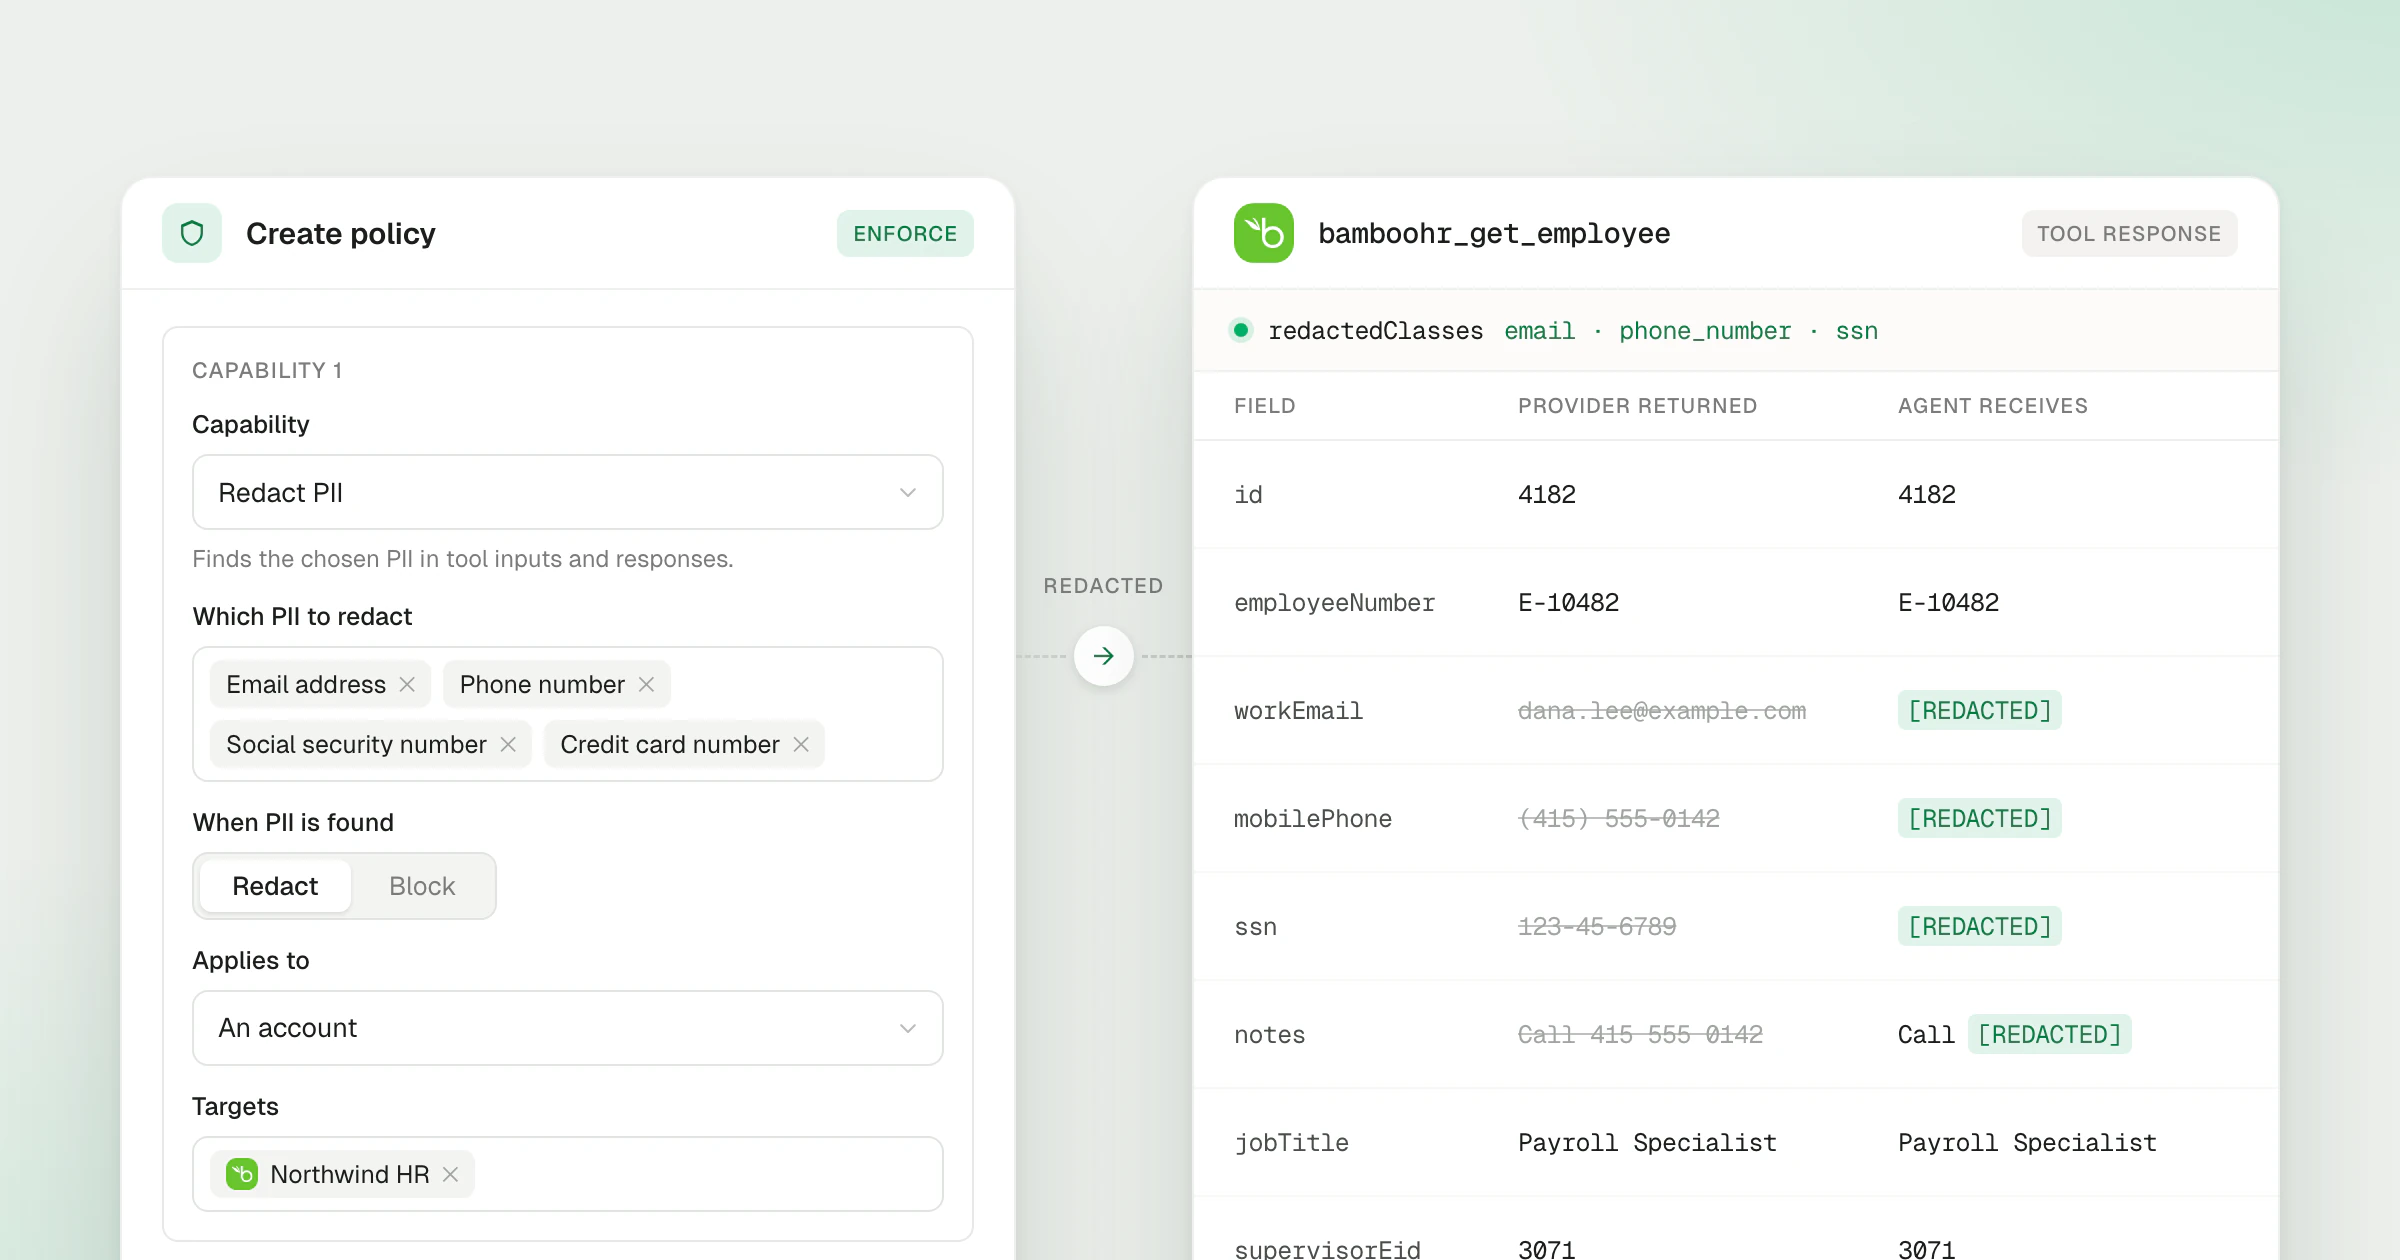
A Redact PII policy rule and an Advanced Logs setting replace each personal value with a tag that names its type in tool calls and stored logs, keeping order numbers, record references and keys intact.
Read about PII redaction
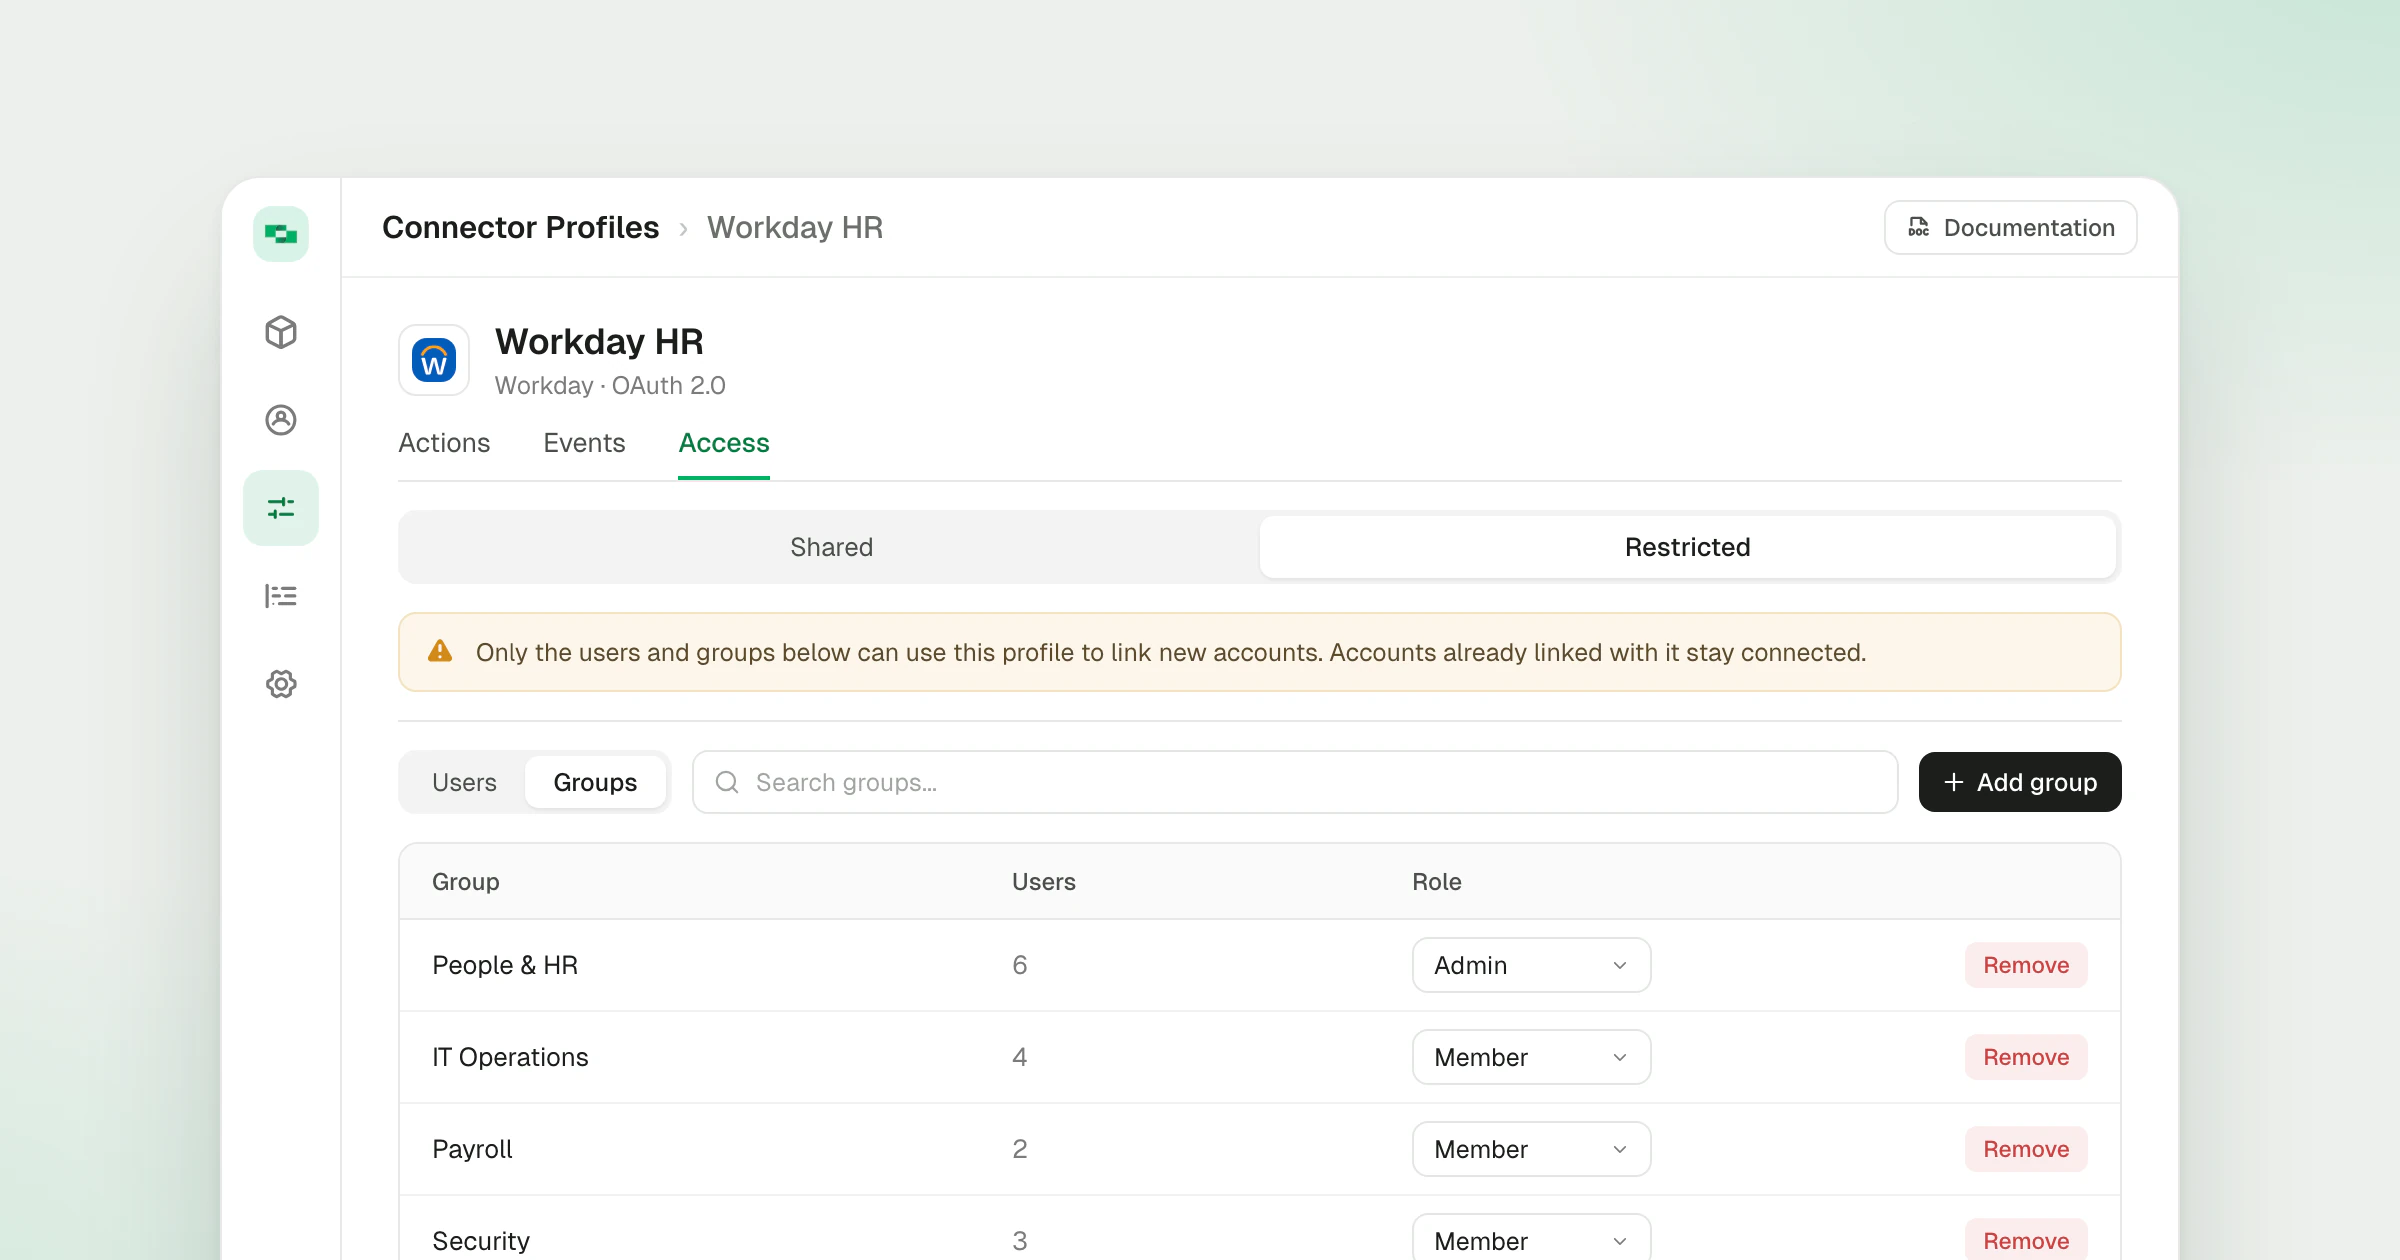
Restrict a connector profile to the users and groups who may link through it, and share a linked account so several people act through one login.
Read about Connector Profile Sharing
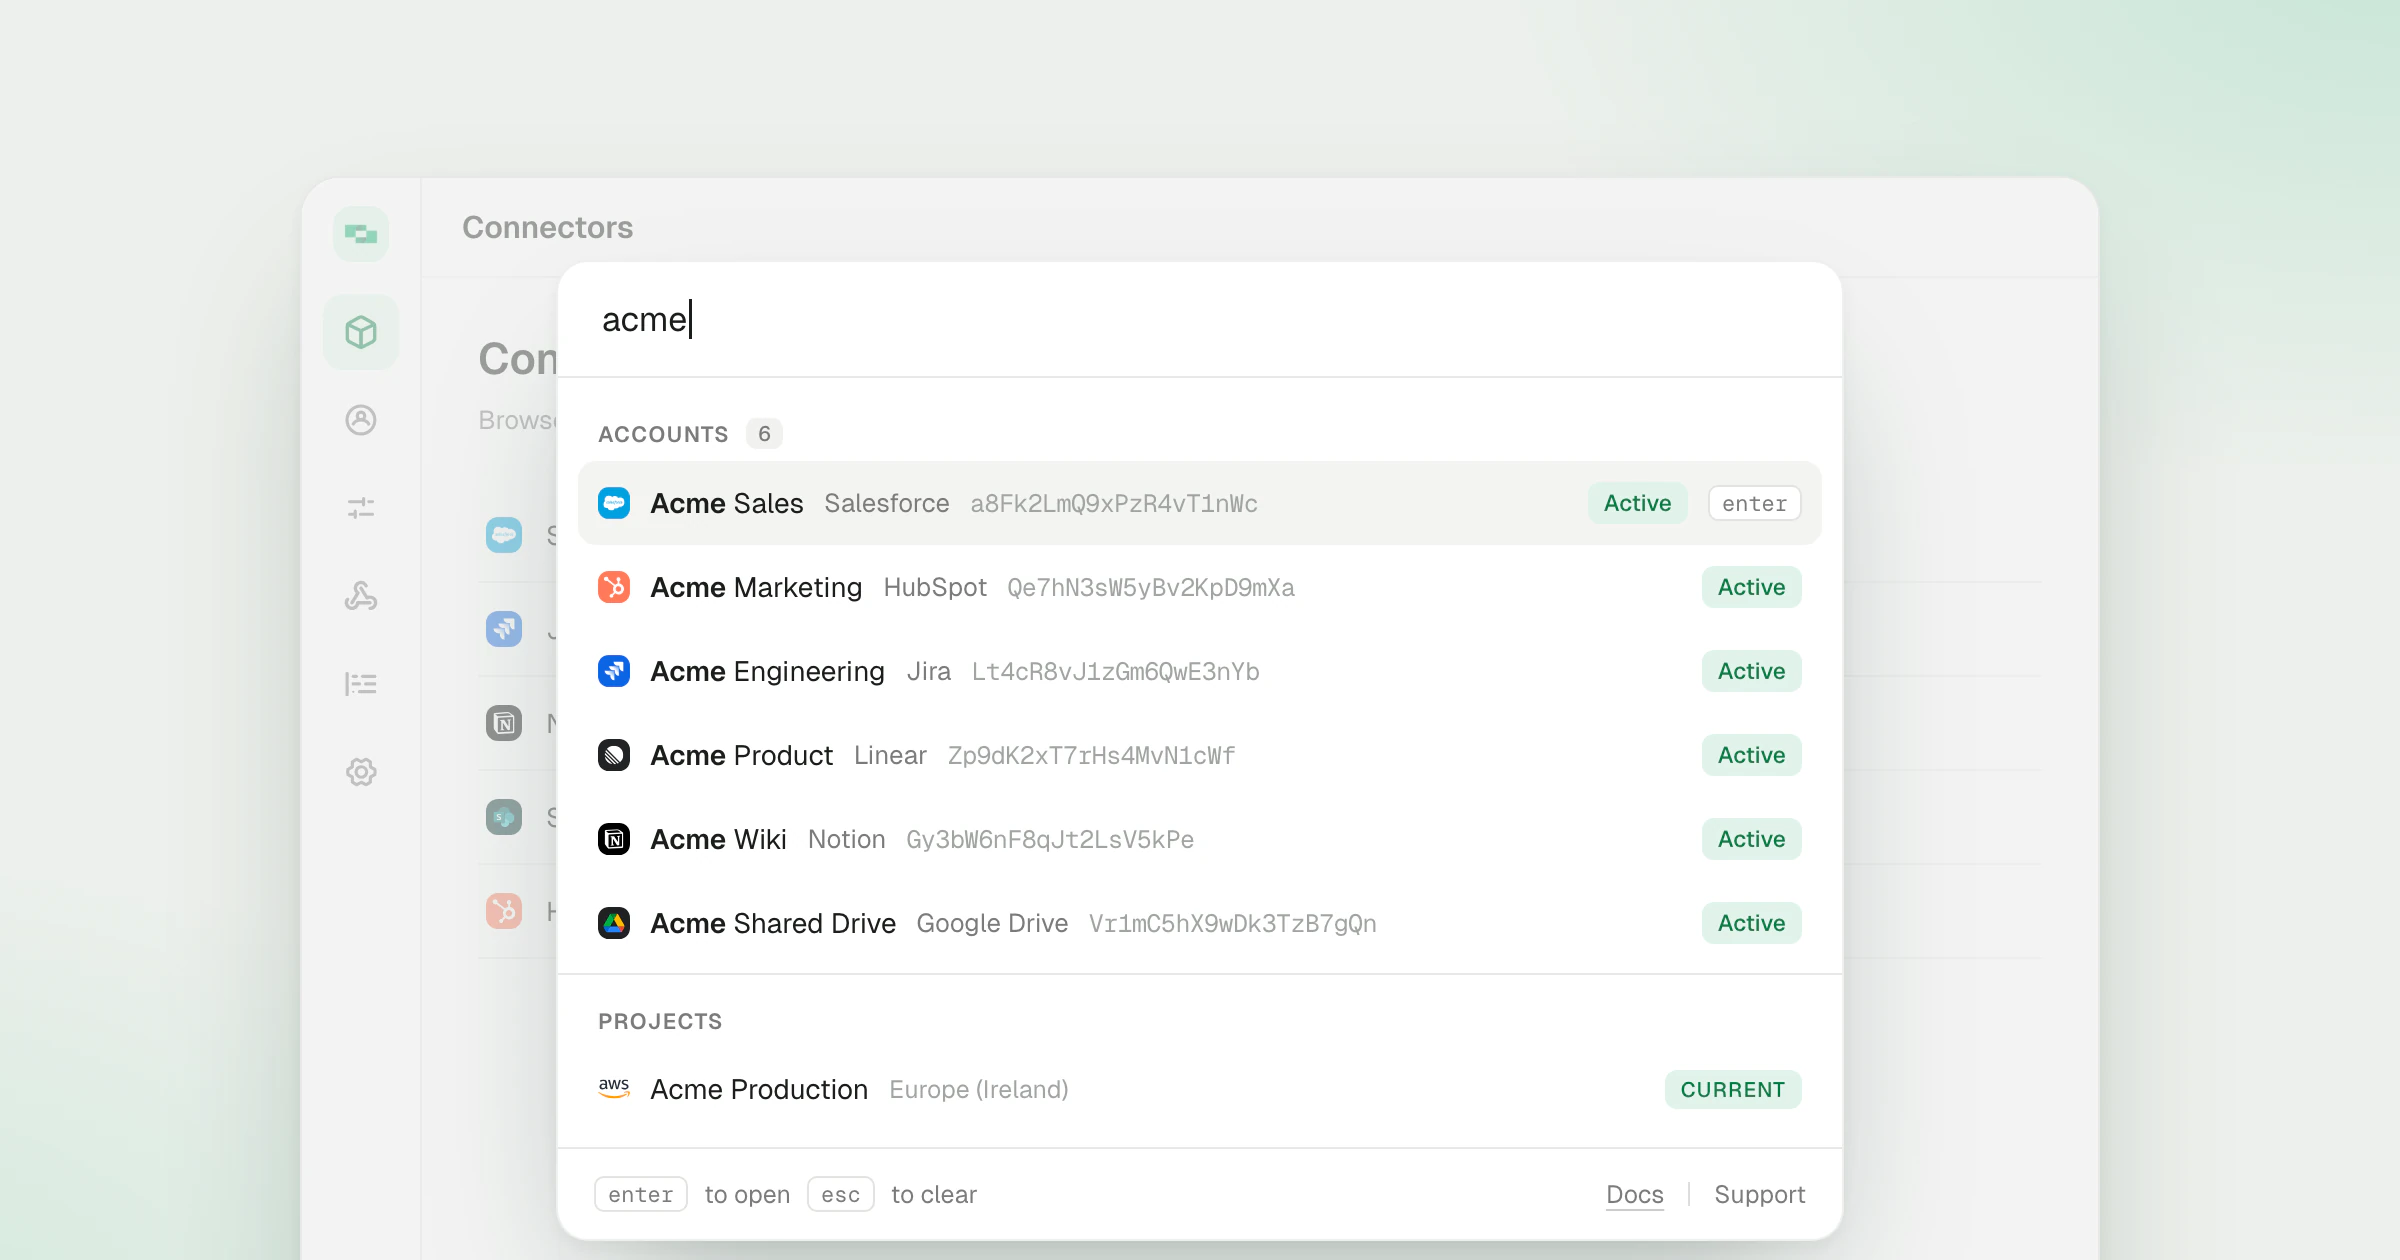
Cmd+K on Mac or Ctrl+K on Windows finds accounts, connectors, projects and organizations, and offers only the pages and actions your role allows.
Read about Command Palette
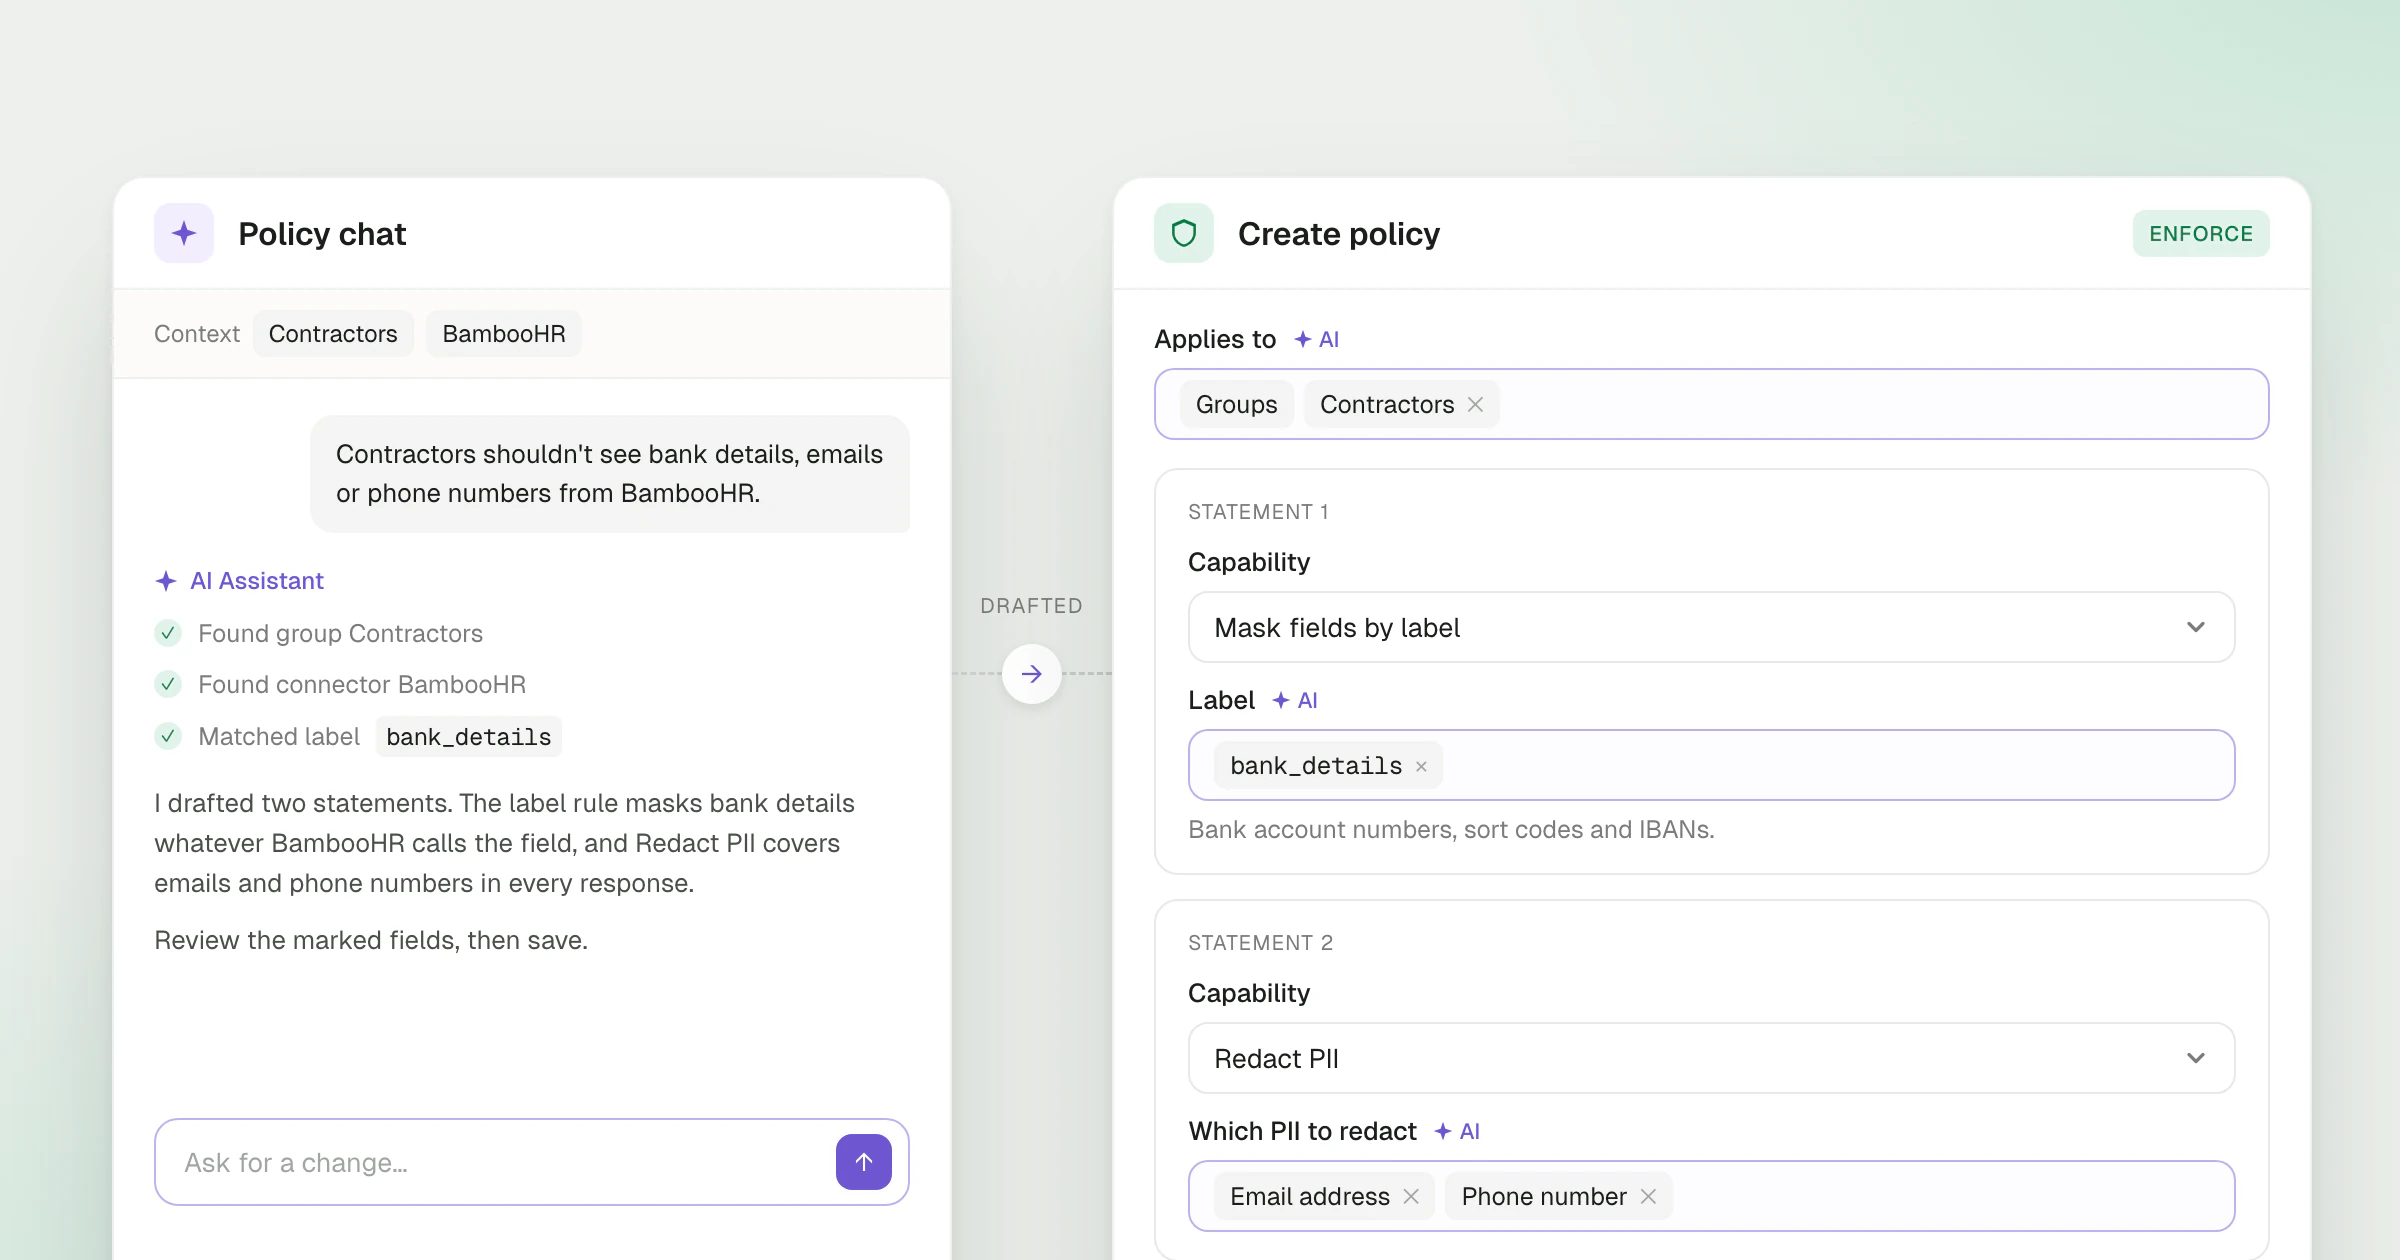
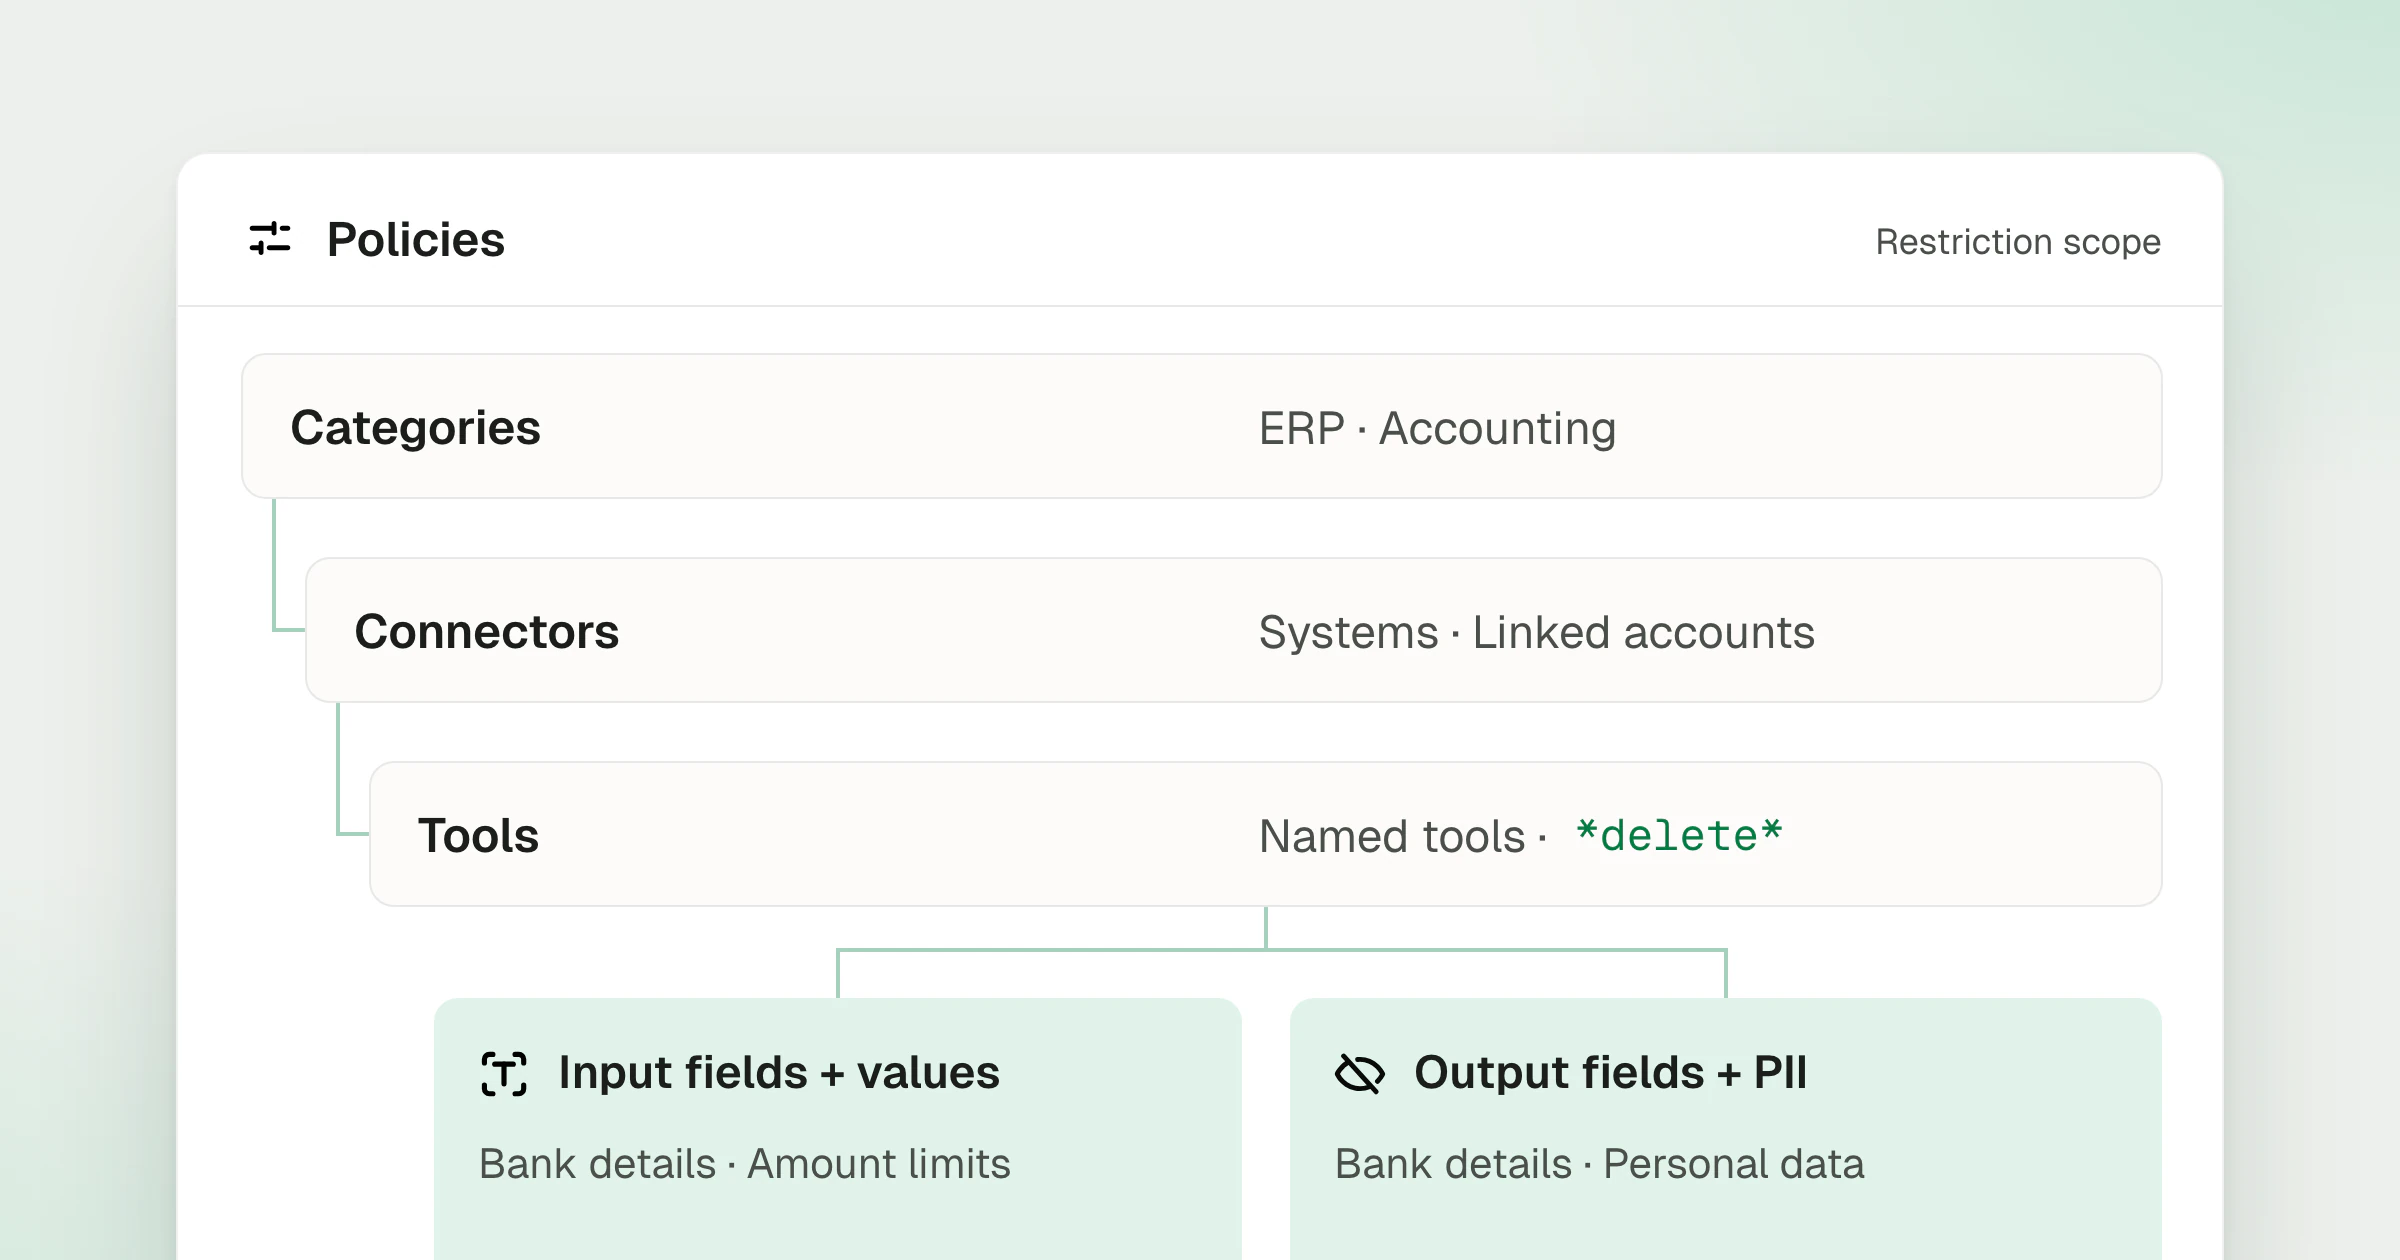
Tool Policies now run semantic rules and PII redaction on tool inputs and responses, and the Policy AI Assistant drafts rules from a description or a logged call.
Read about agent tool policies
Before you approve an AI app, the MCP OAuth consent screen now shows where your access goes and, for apps with a metadata document, the publishing domain.
Read about Client ID Metadata Documents
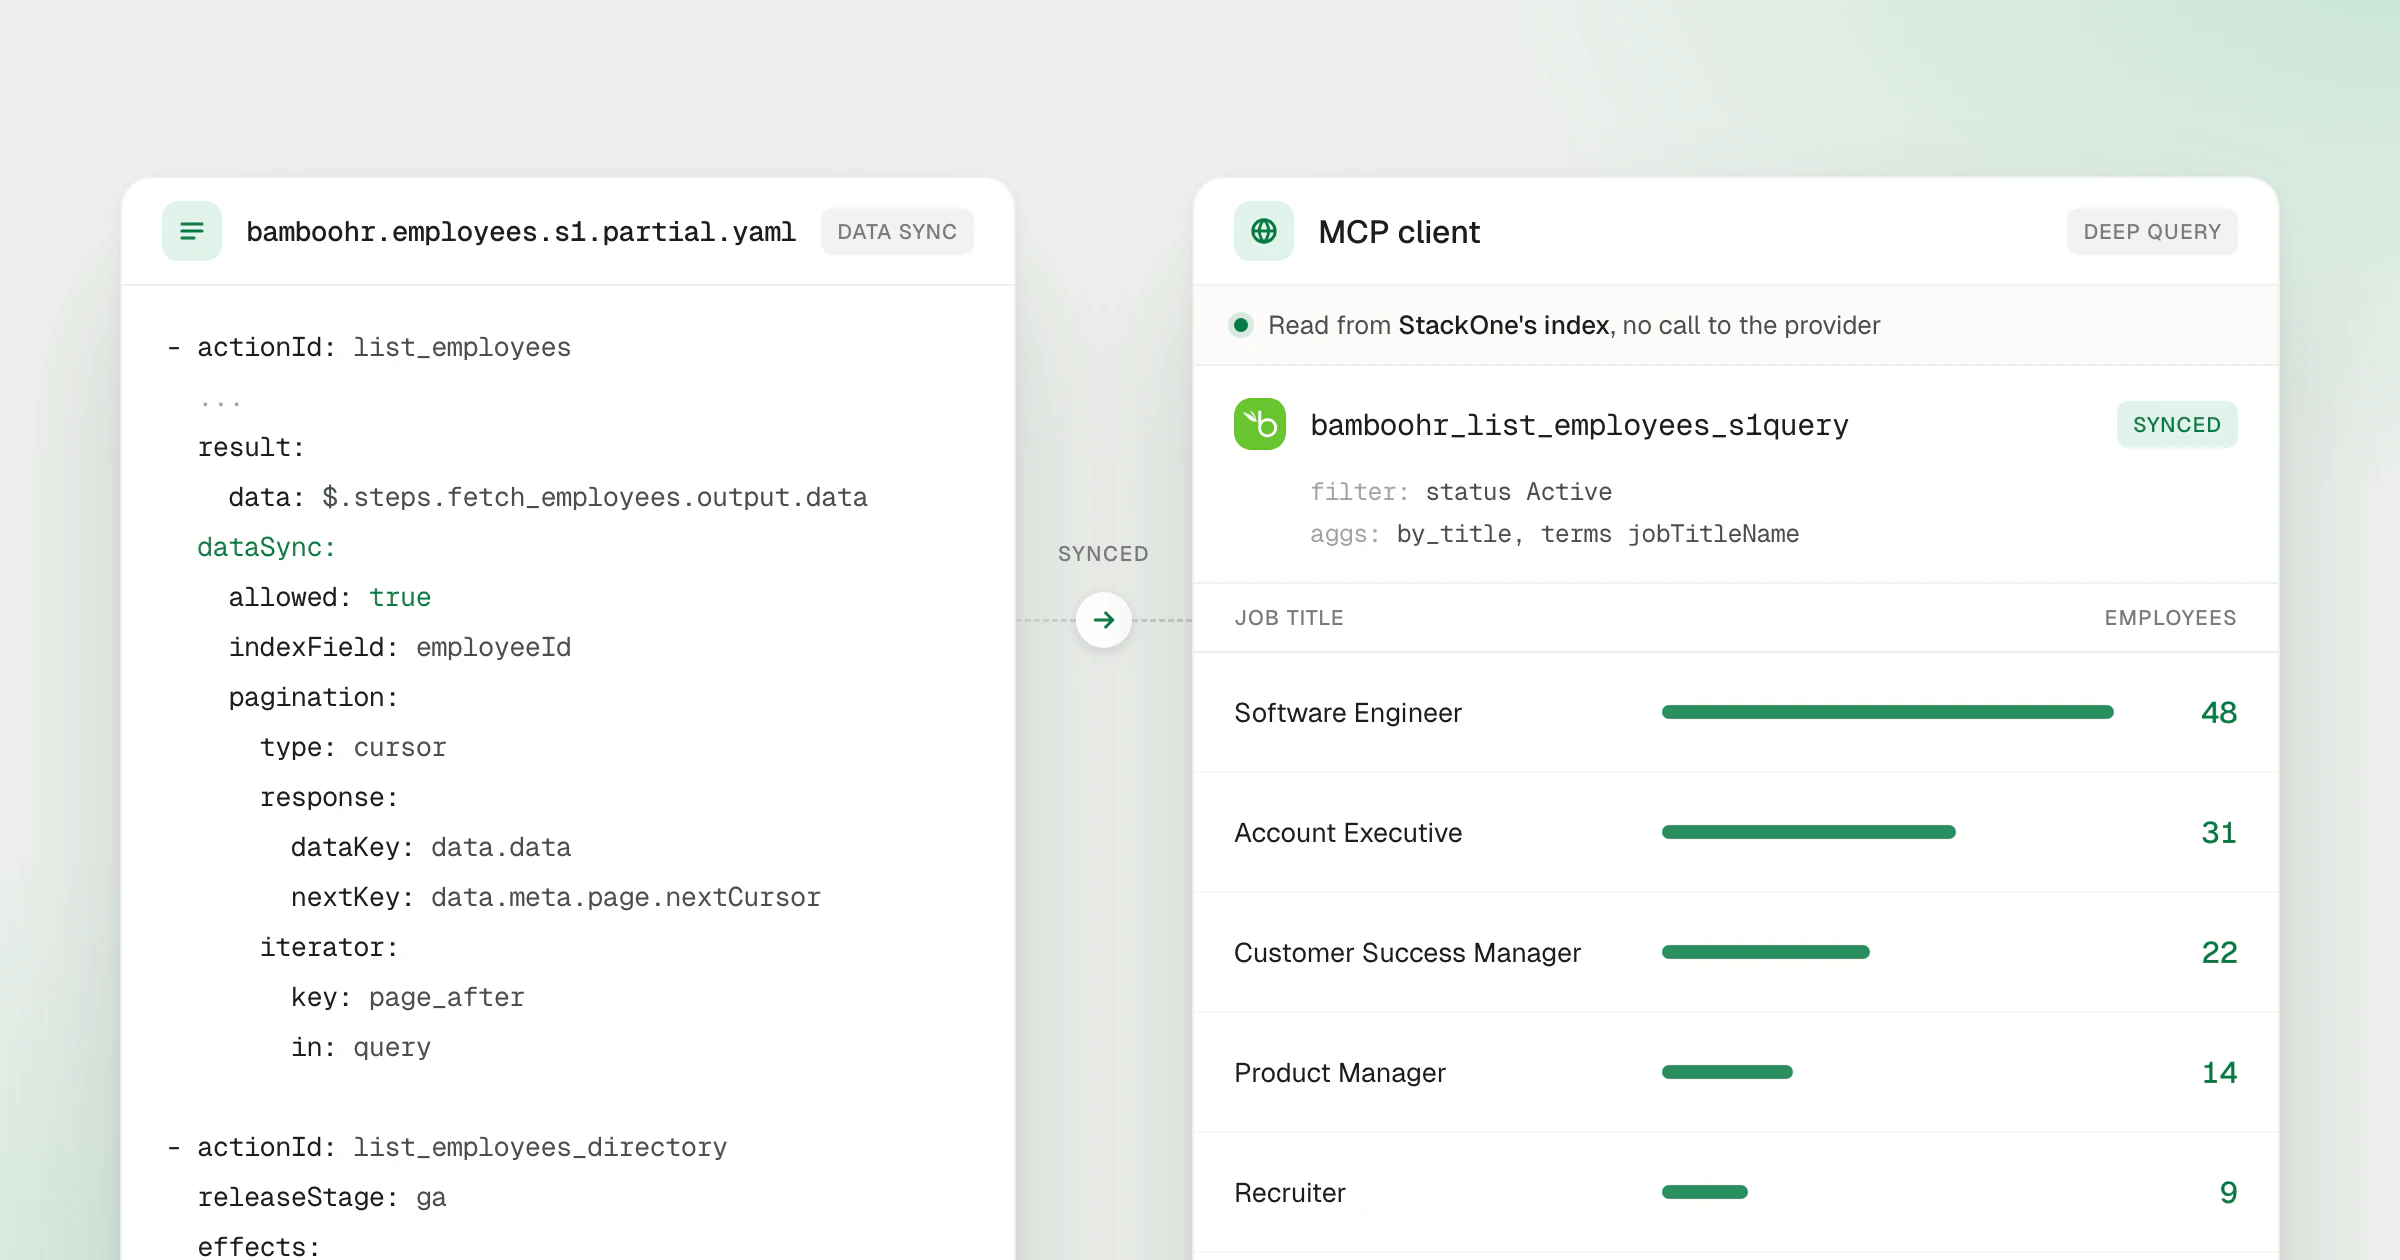
Deep Query lets agents filter, search and aggregate records stored by Data Sync, returning counts or selected fields instead of full datasets.
Read about Deep Query
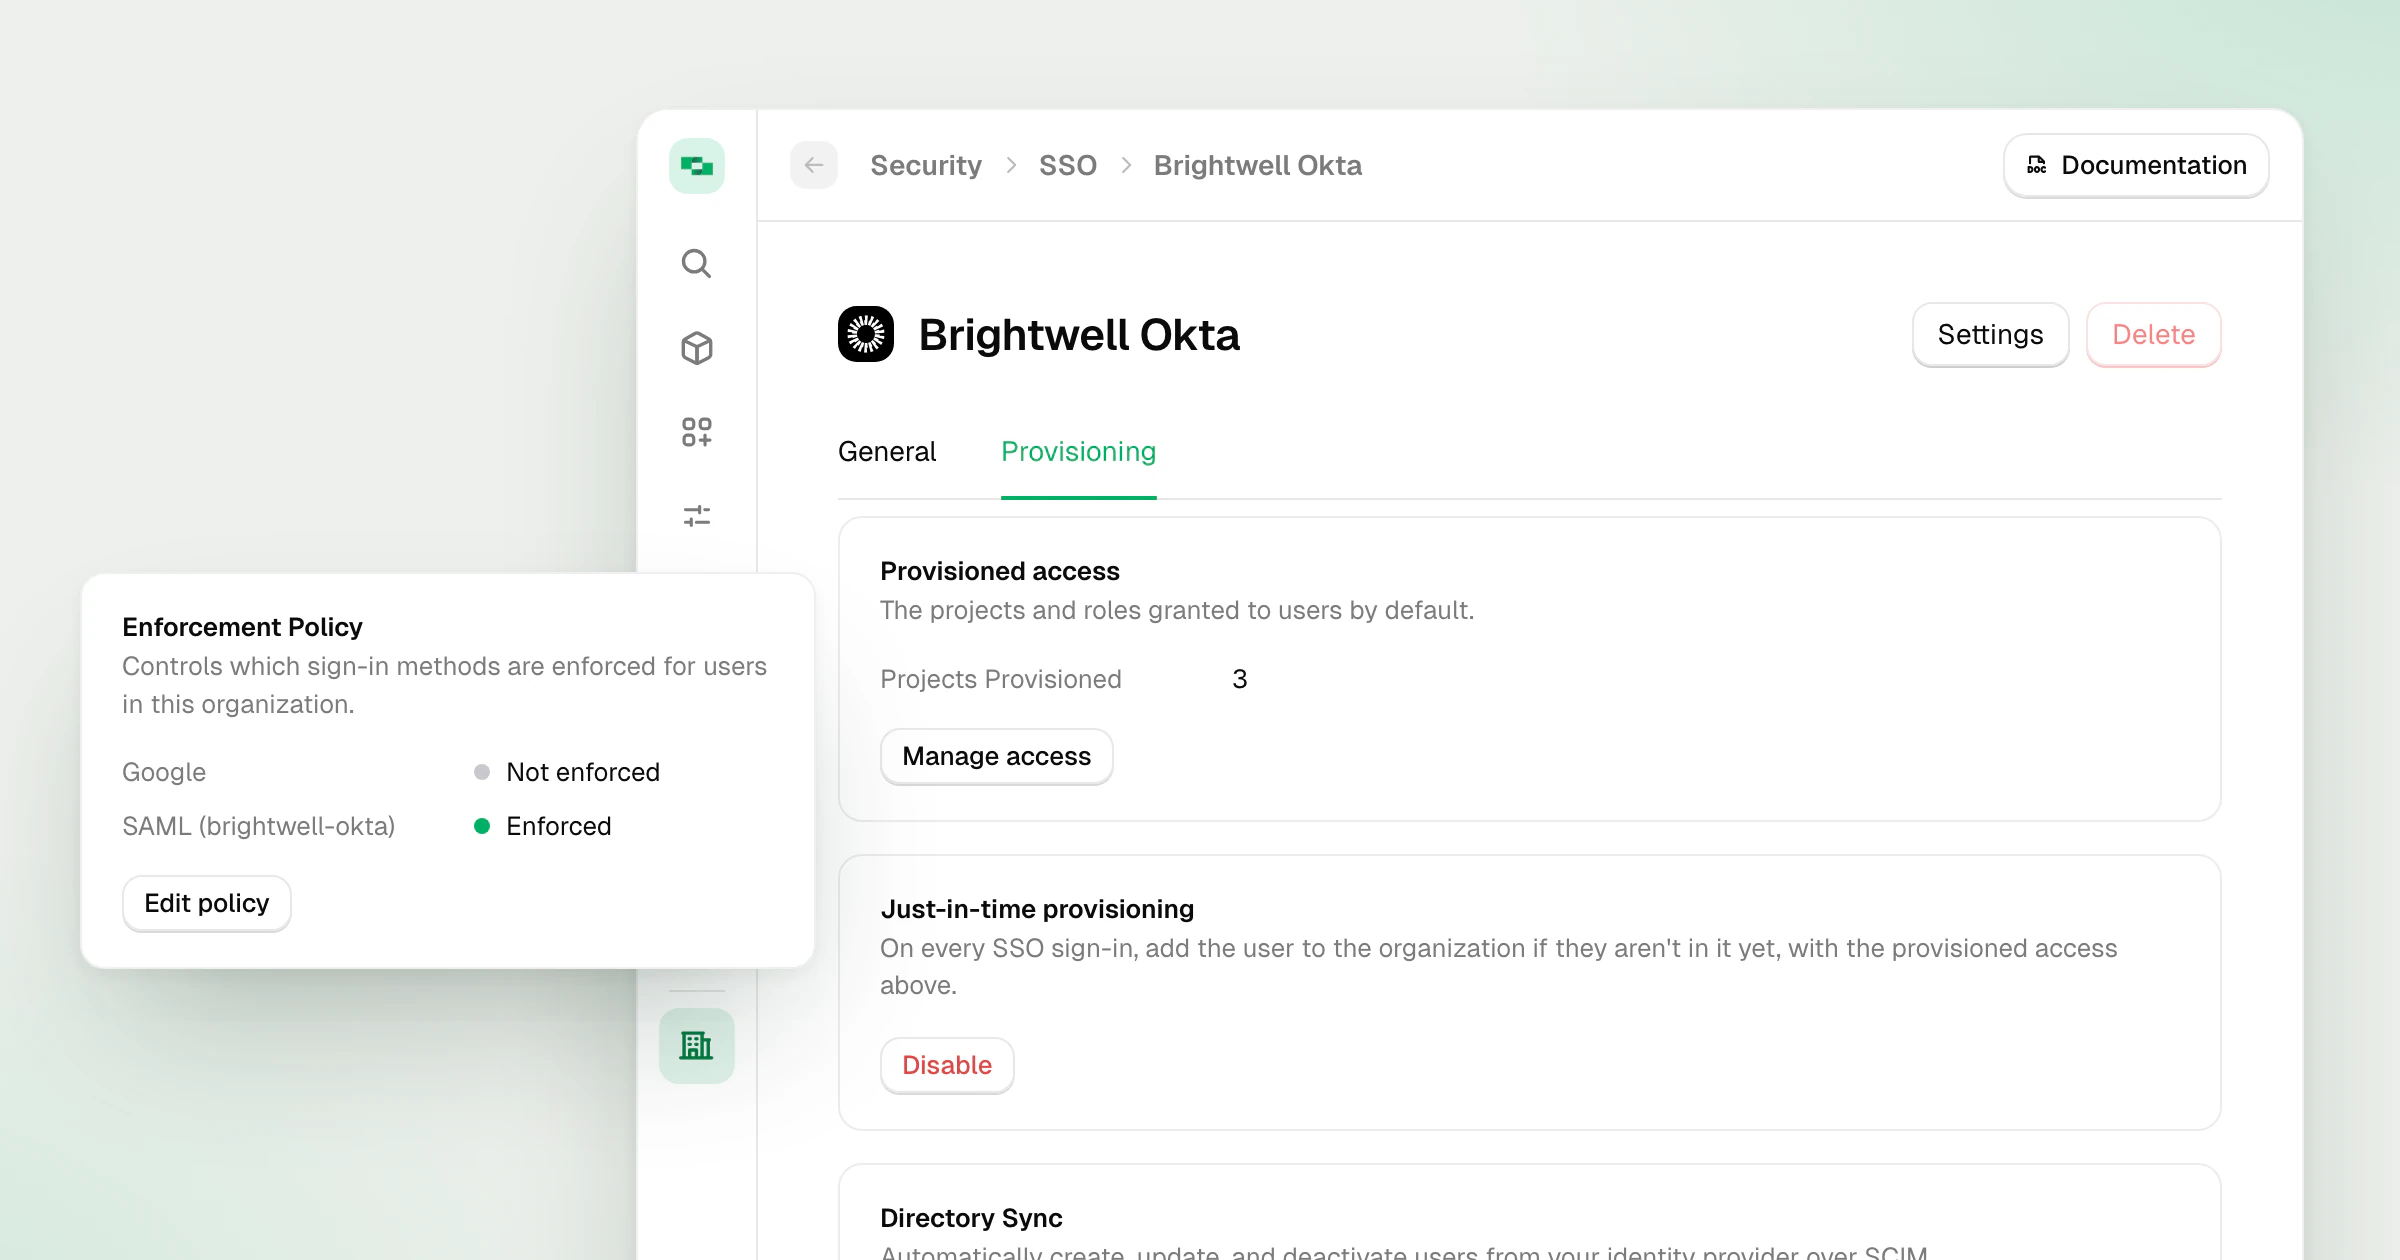
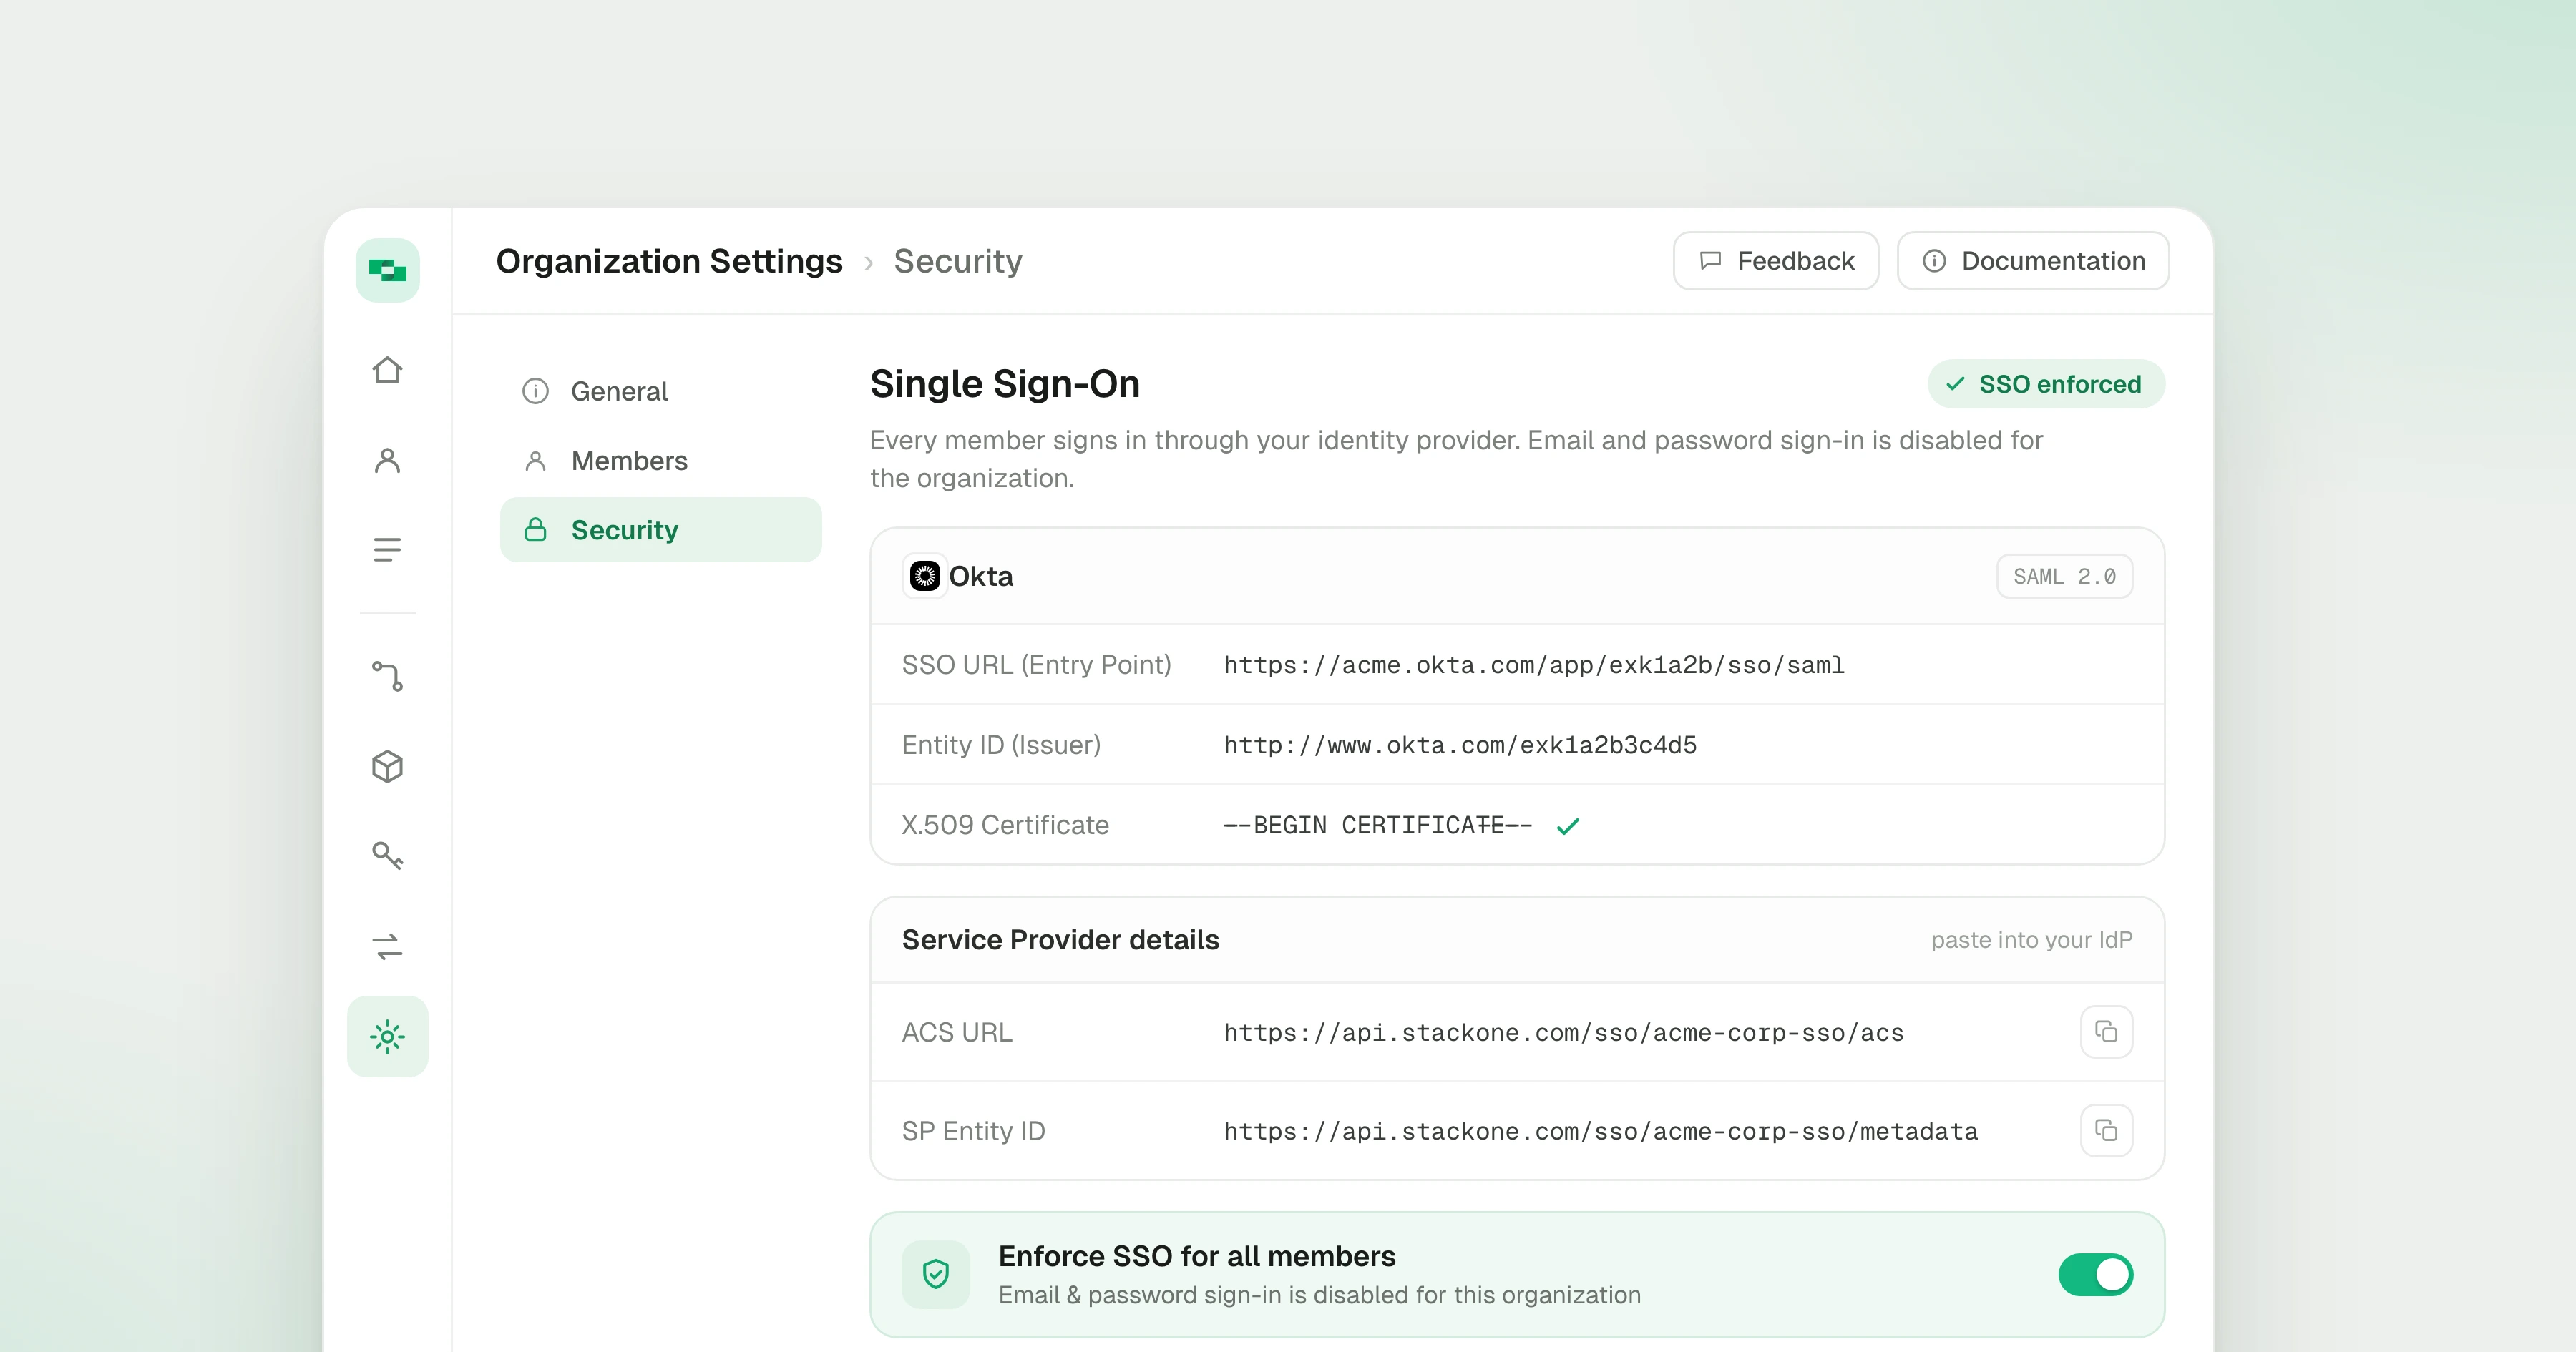
SAML SSO setup is rebuilt, Just-in-Time provisioning adds users at their first SSO sign-in, and an Enforcement Policy limits each organization to SSO.
Read about Just-in-Time provisioning
Connector profiles move out of a side panel onto each connector's page, with profile cards, tabs, search and filters by effect, auth method and tag.
Read about Connector Profiles
Directory Sync provisions and deprovisions StackOne users from Okta or Entra over SCIM, and syncs directory groups into StackOne groups.
Read about Directory Sync
Tool Policies let admins restrict agent tools, input fields and values, and output data for users and groups, with AI authoring and request log details.
Read about agent tool policies
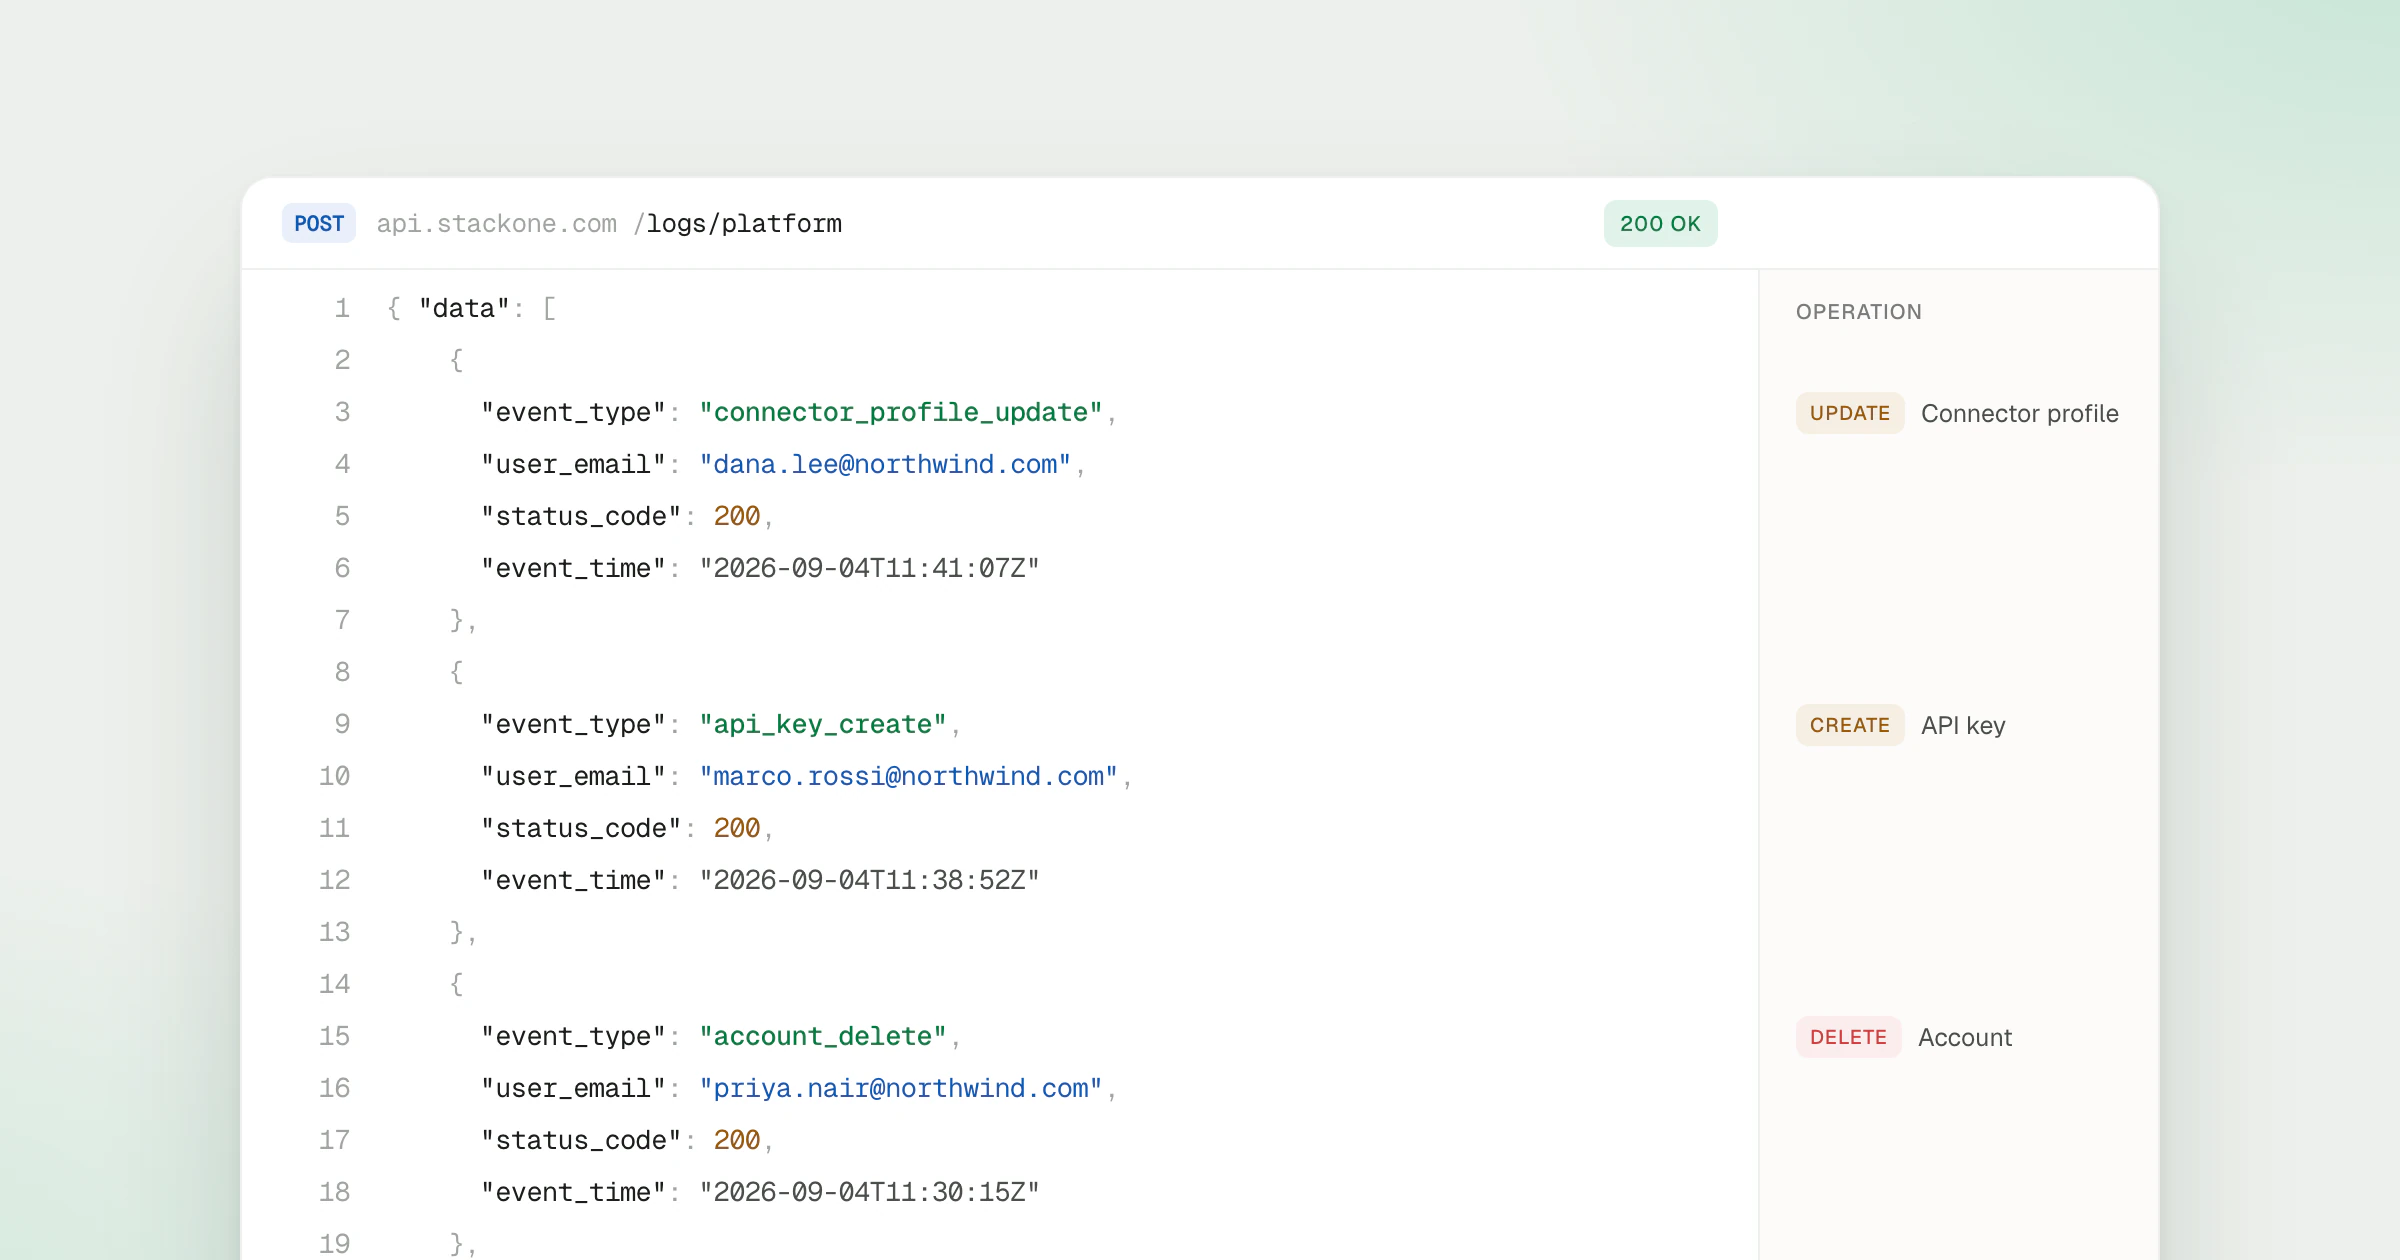
Platform logs record setup changes in StackOne. A collector pulls them and action logs through the Logs API into Splunk, Datadog or any SIEM.
Read about SIEM export
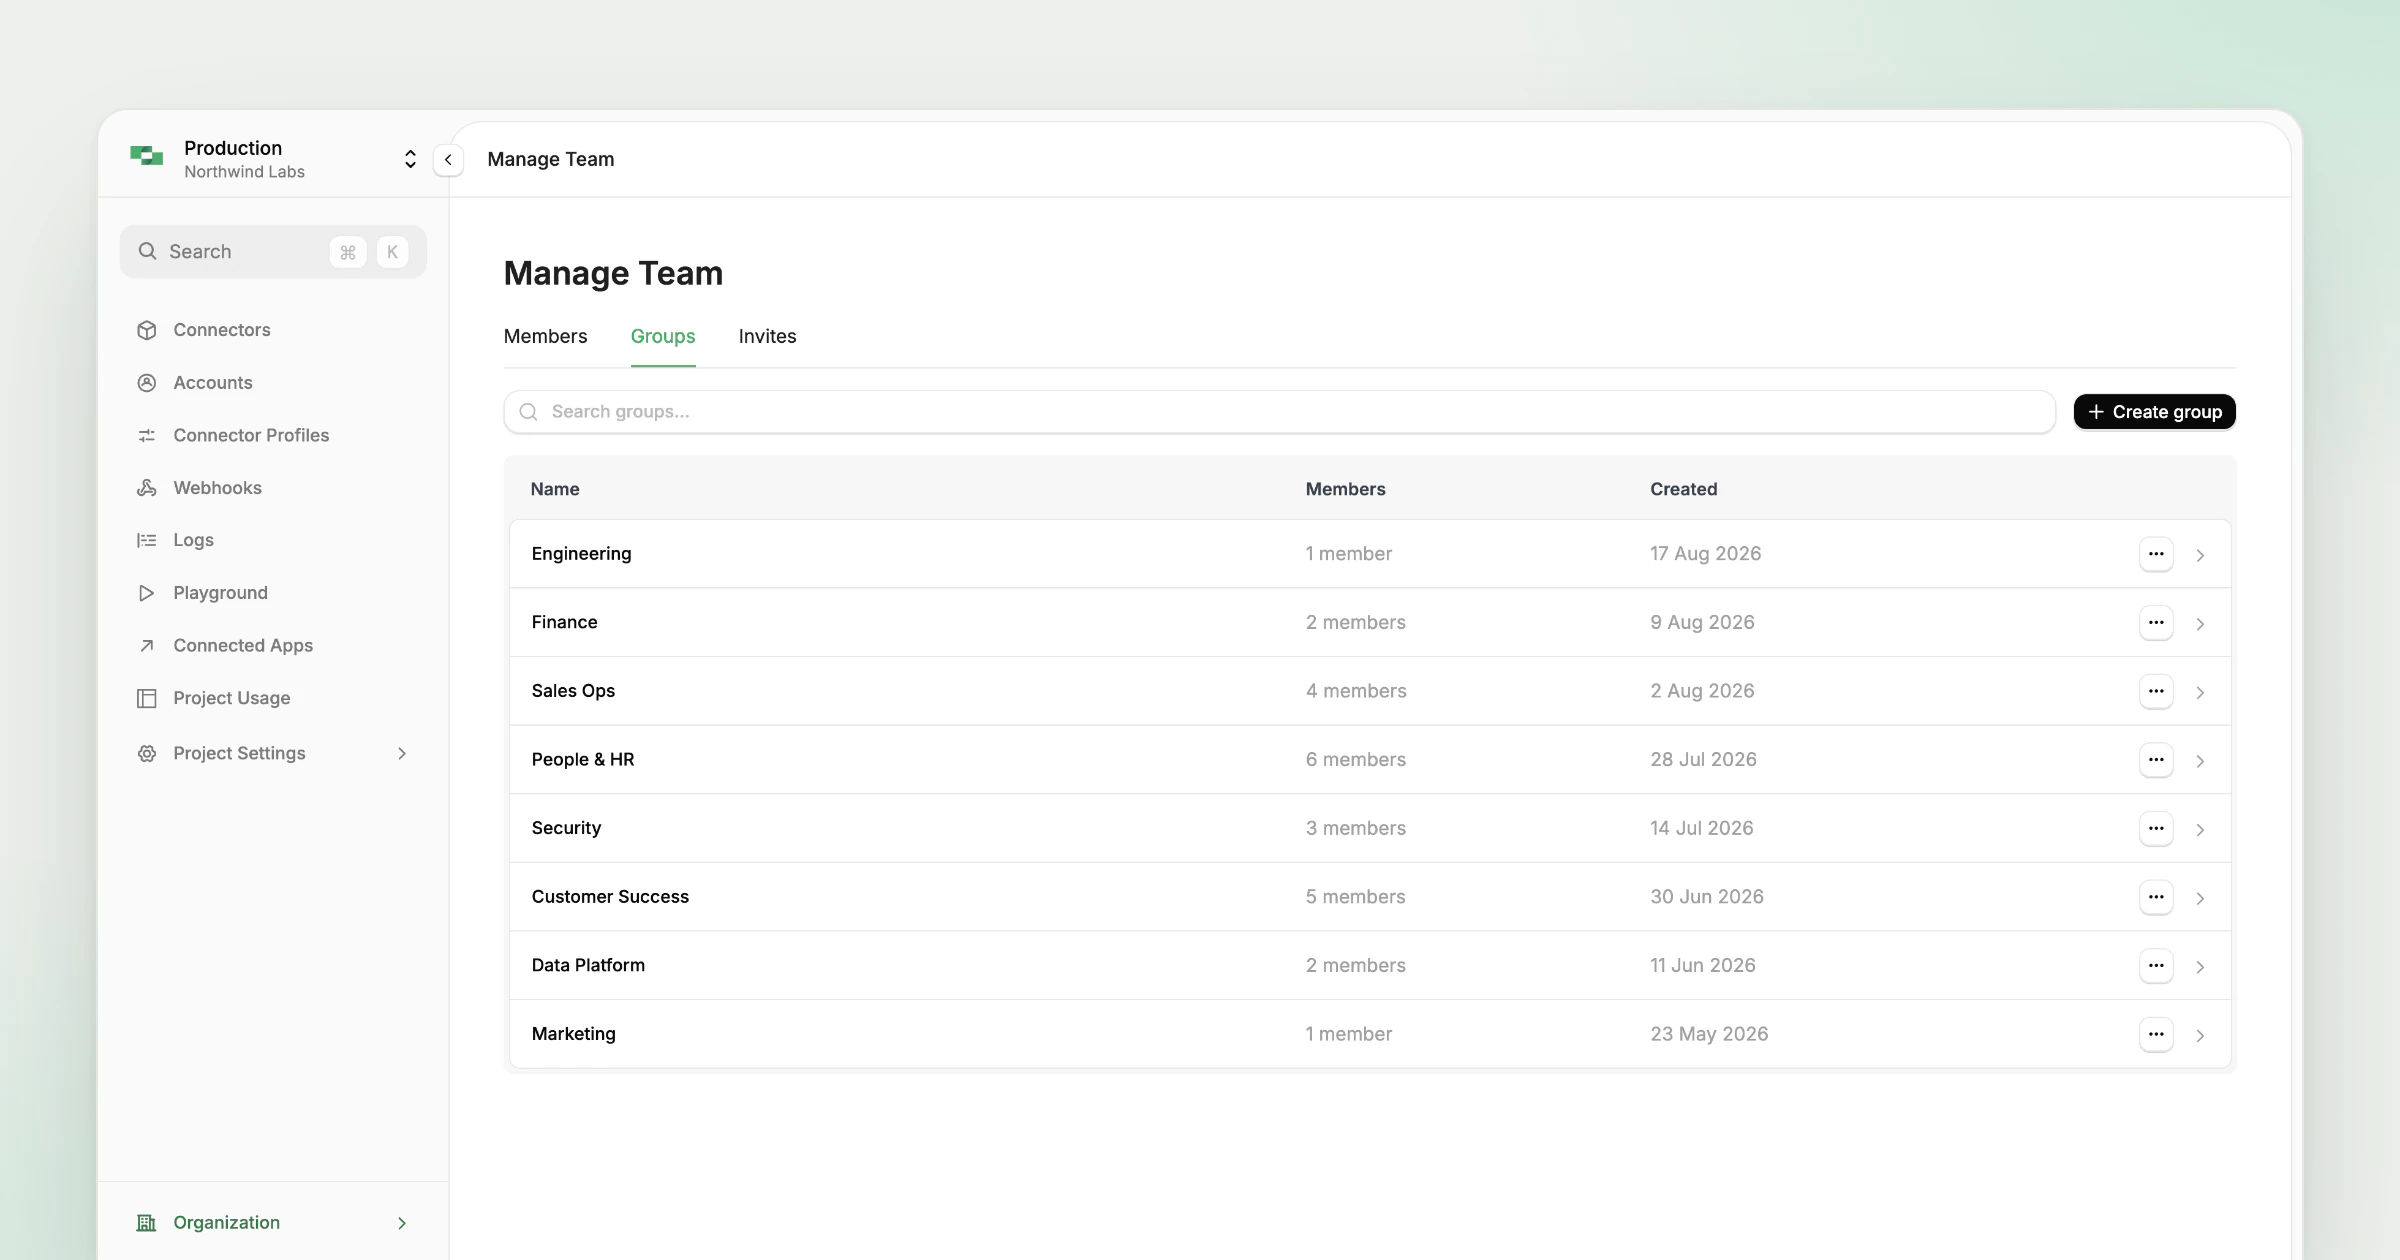
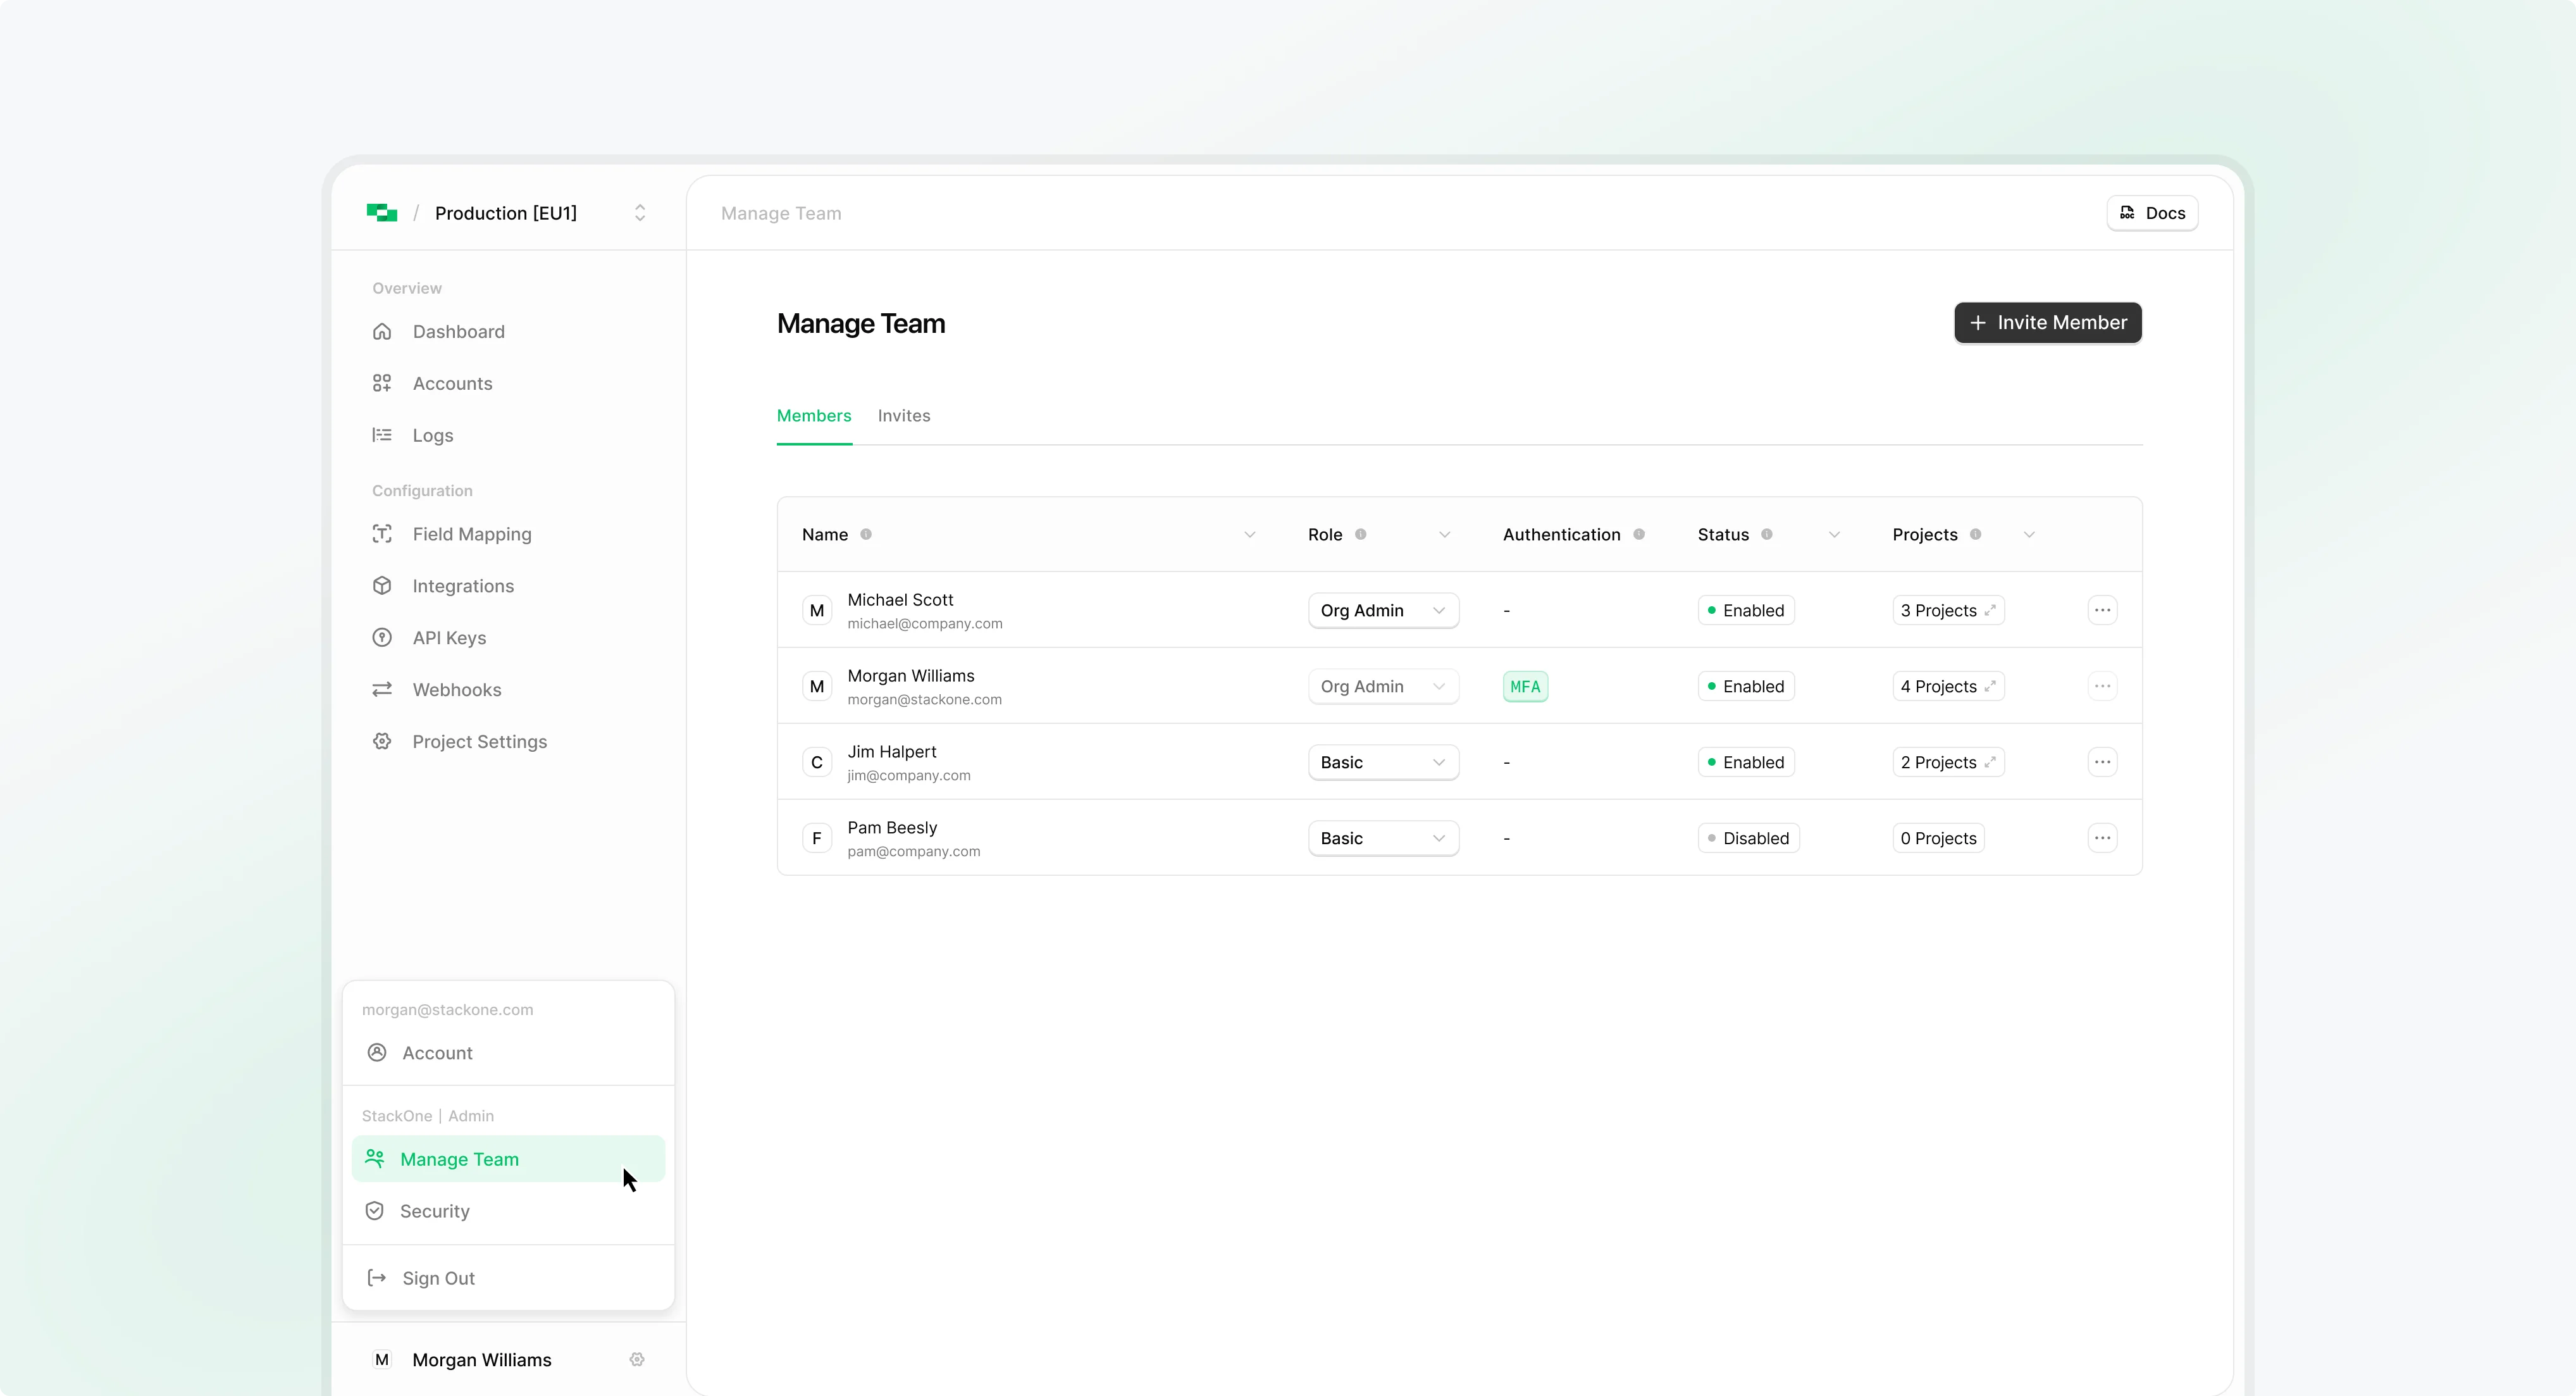
Groups are reusable sets of people. Assign one to a project or linked account with a role and every member inherits it. Manage access in one place.
Read about Groups
Any MCP client can now connect to StackOne over OAuth. Each user signs in and picks which of their linked accounts and actions that client may use.
Read about MCP OAuth
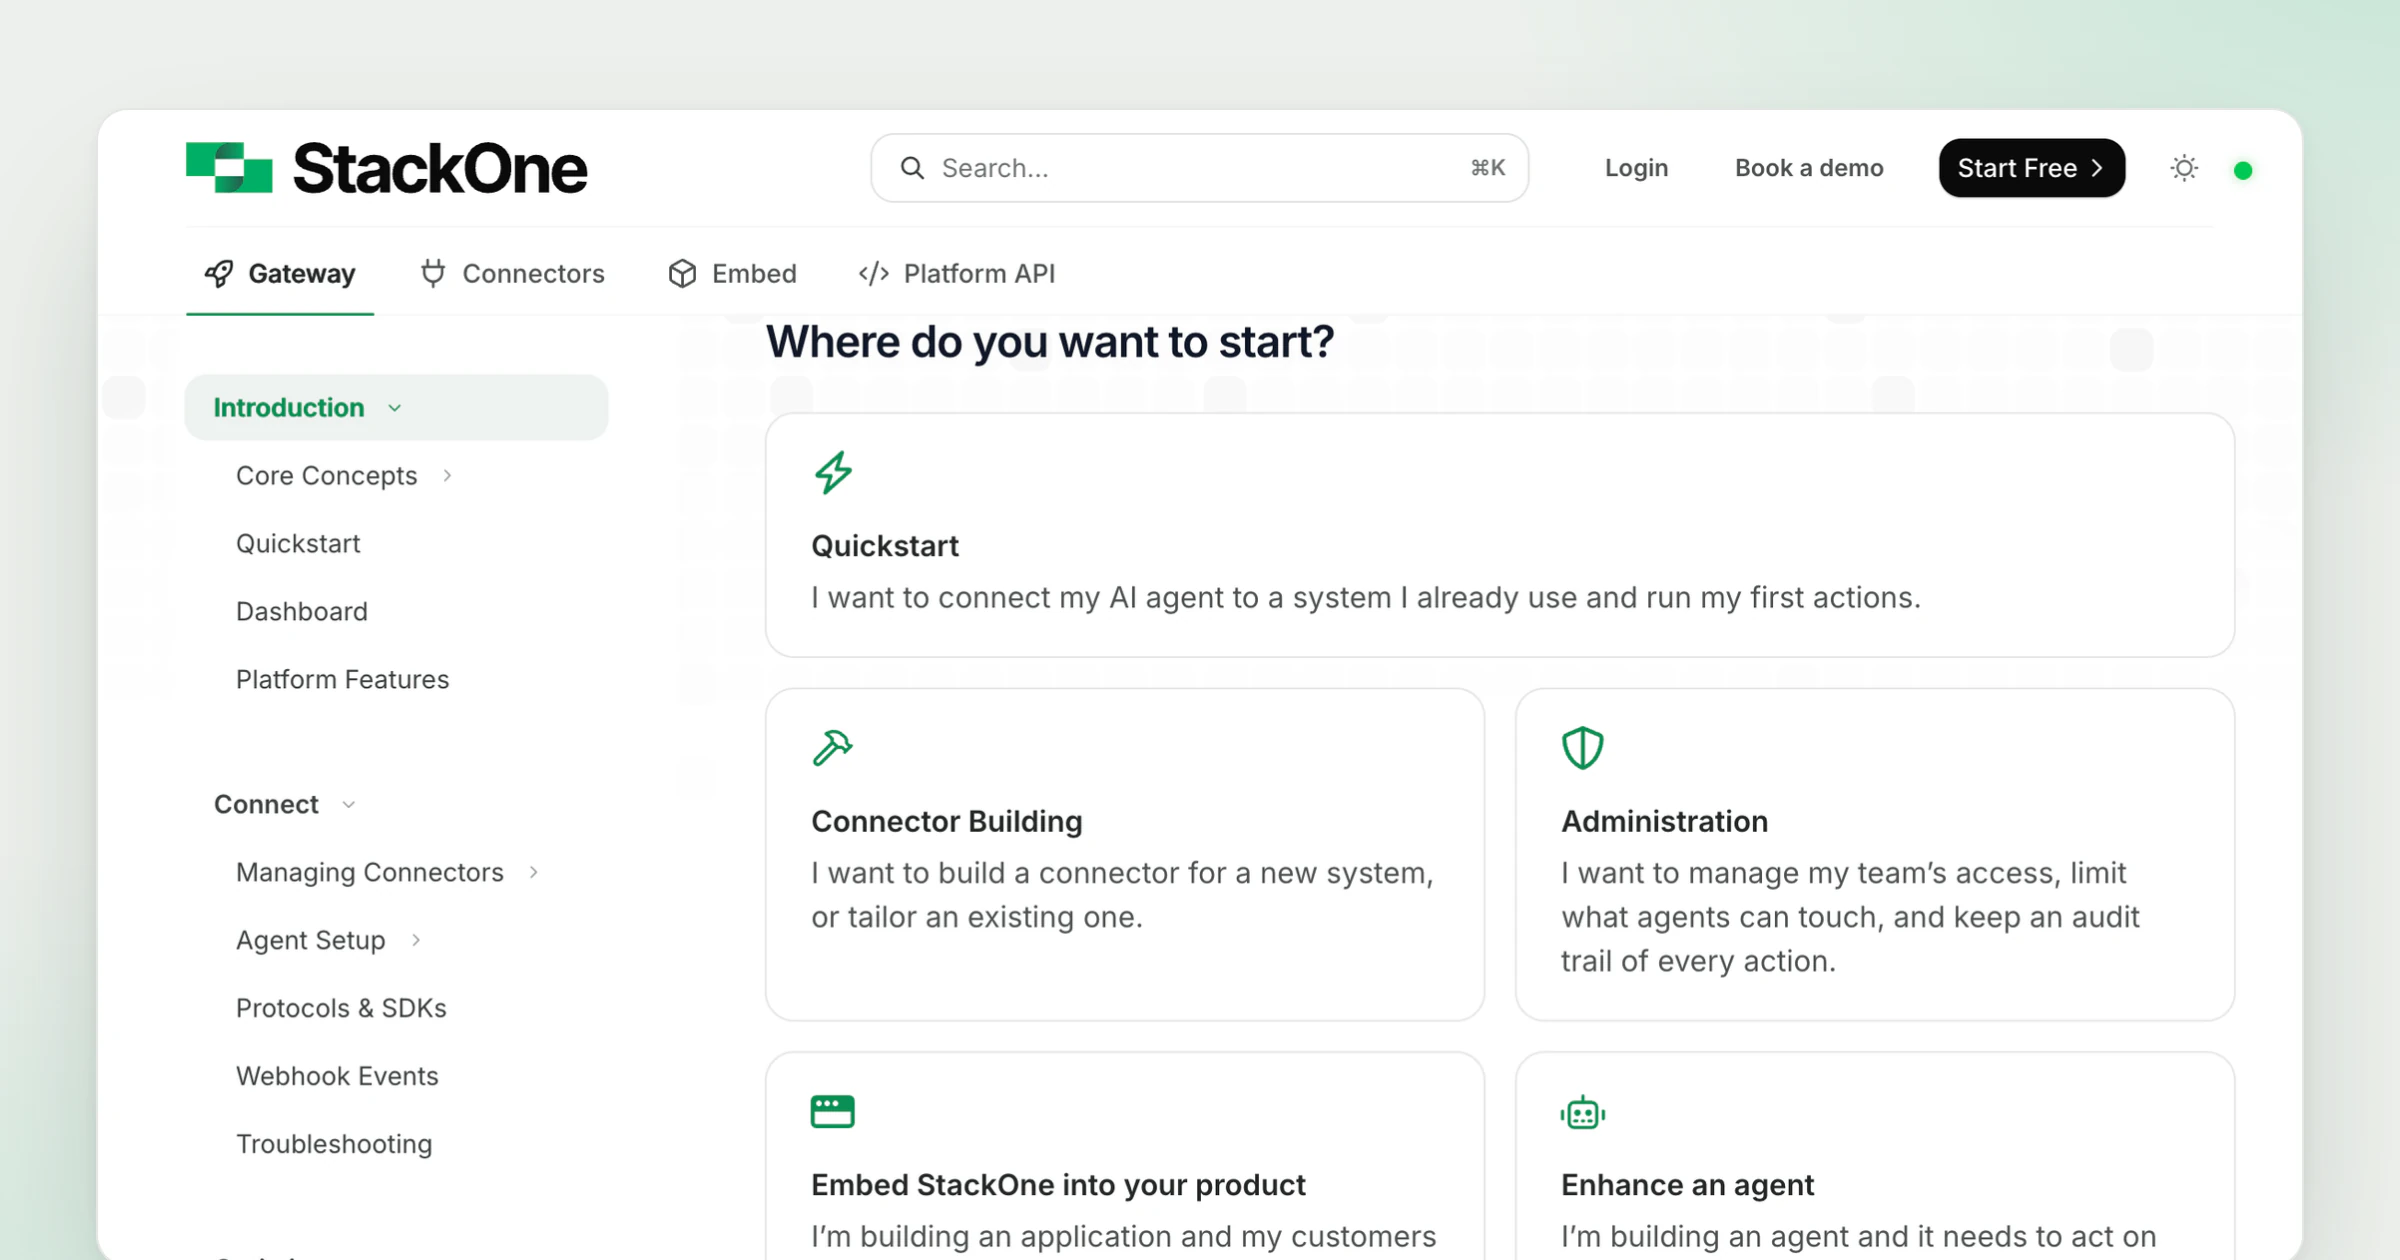
docs.stackone.com is restructured into four tabs, split by whether the reader is writing code: Gateway, Connectors, Embed and Platform API.
Read about StackOne Documentation
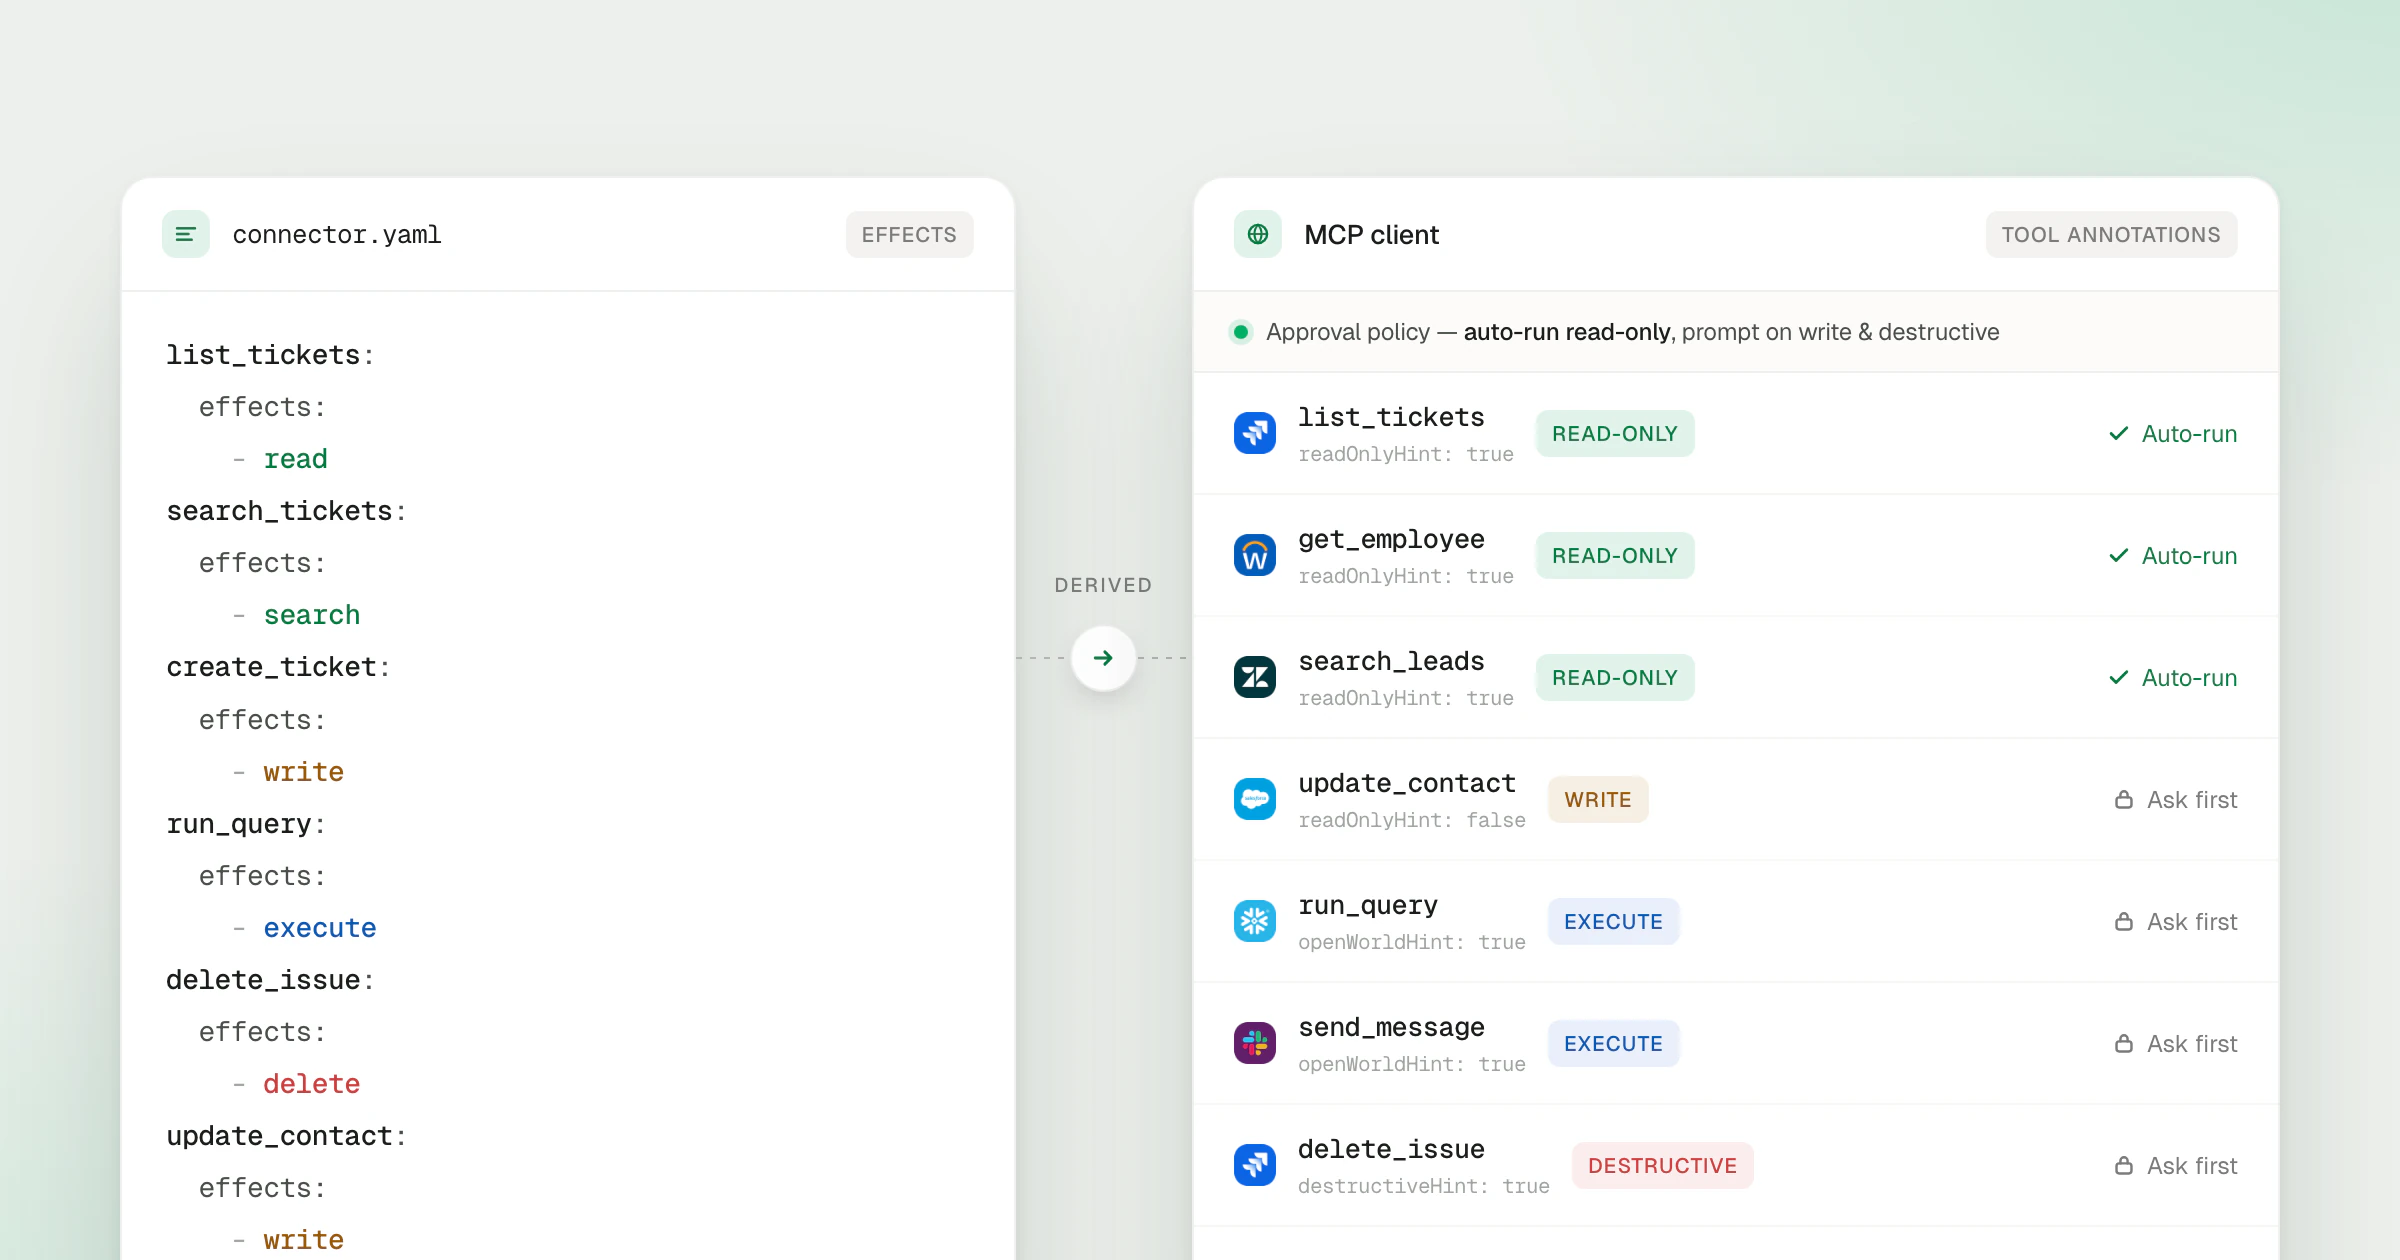
Every StackOne action now carries an effects value that derives standard MCP tool annotations, so clients can auto-approve reads and gate writes and deletes.
Read about MCP Tool Annotations
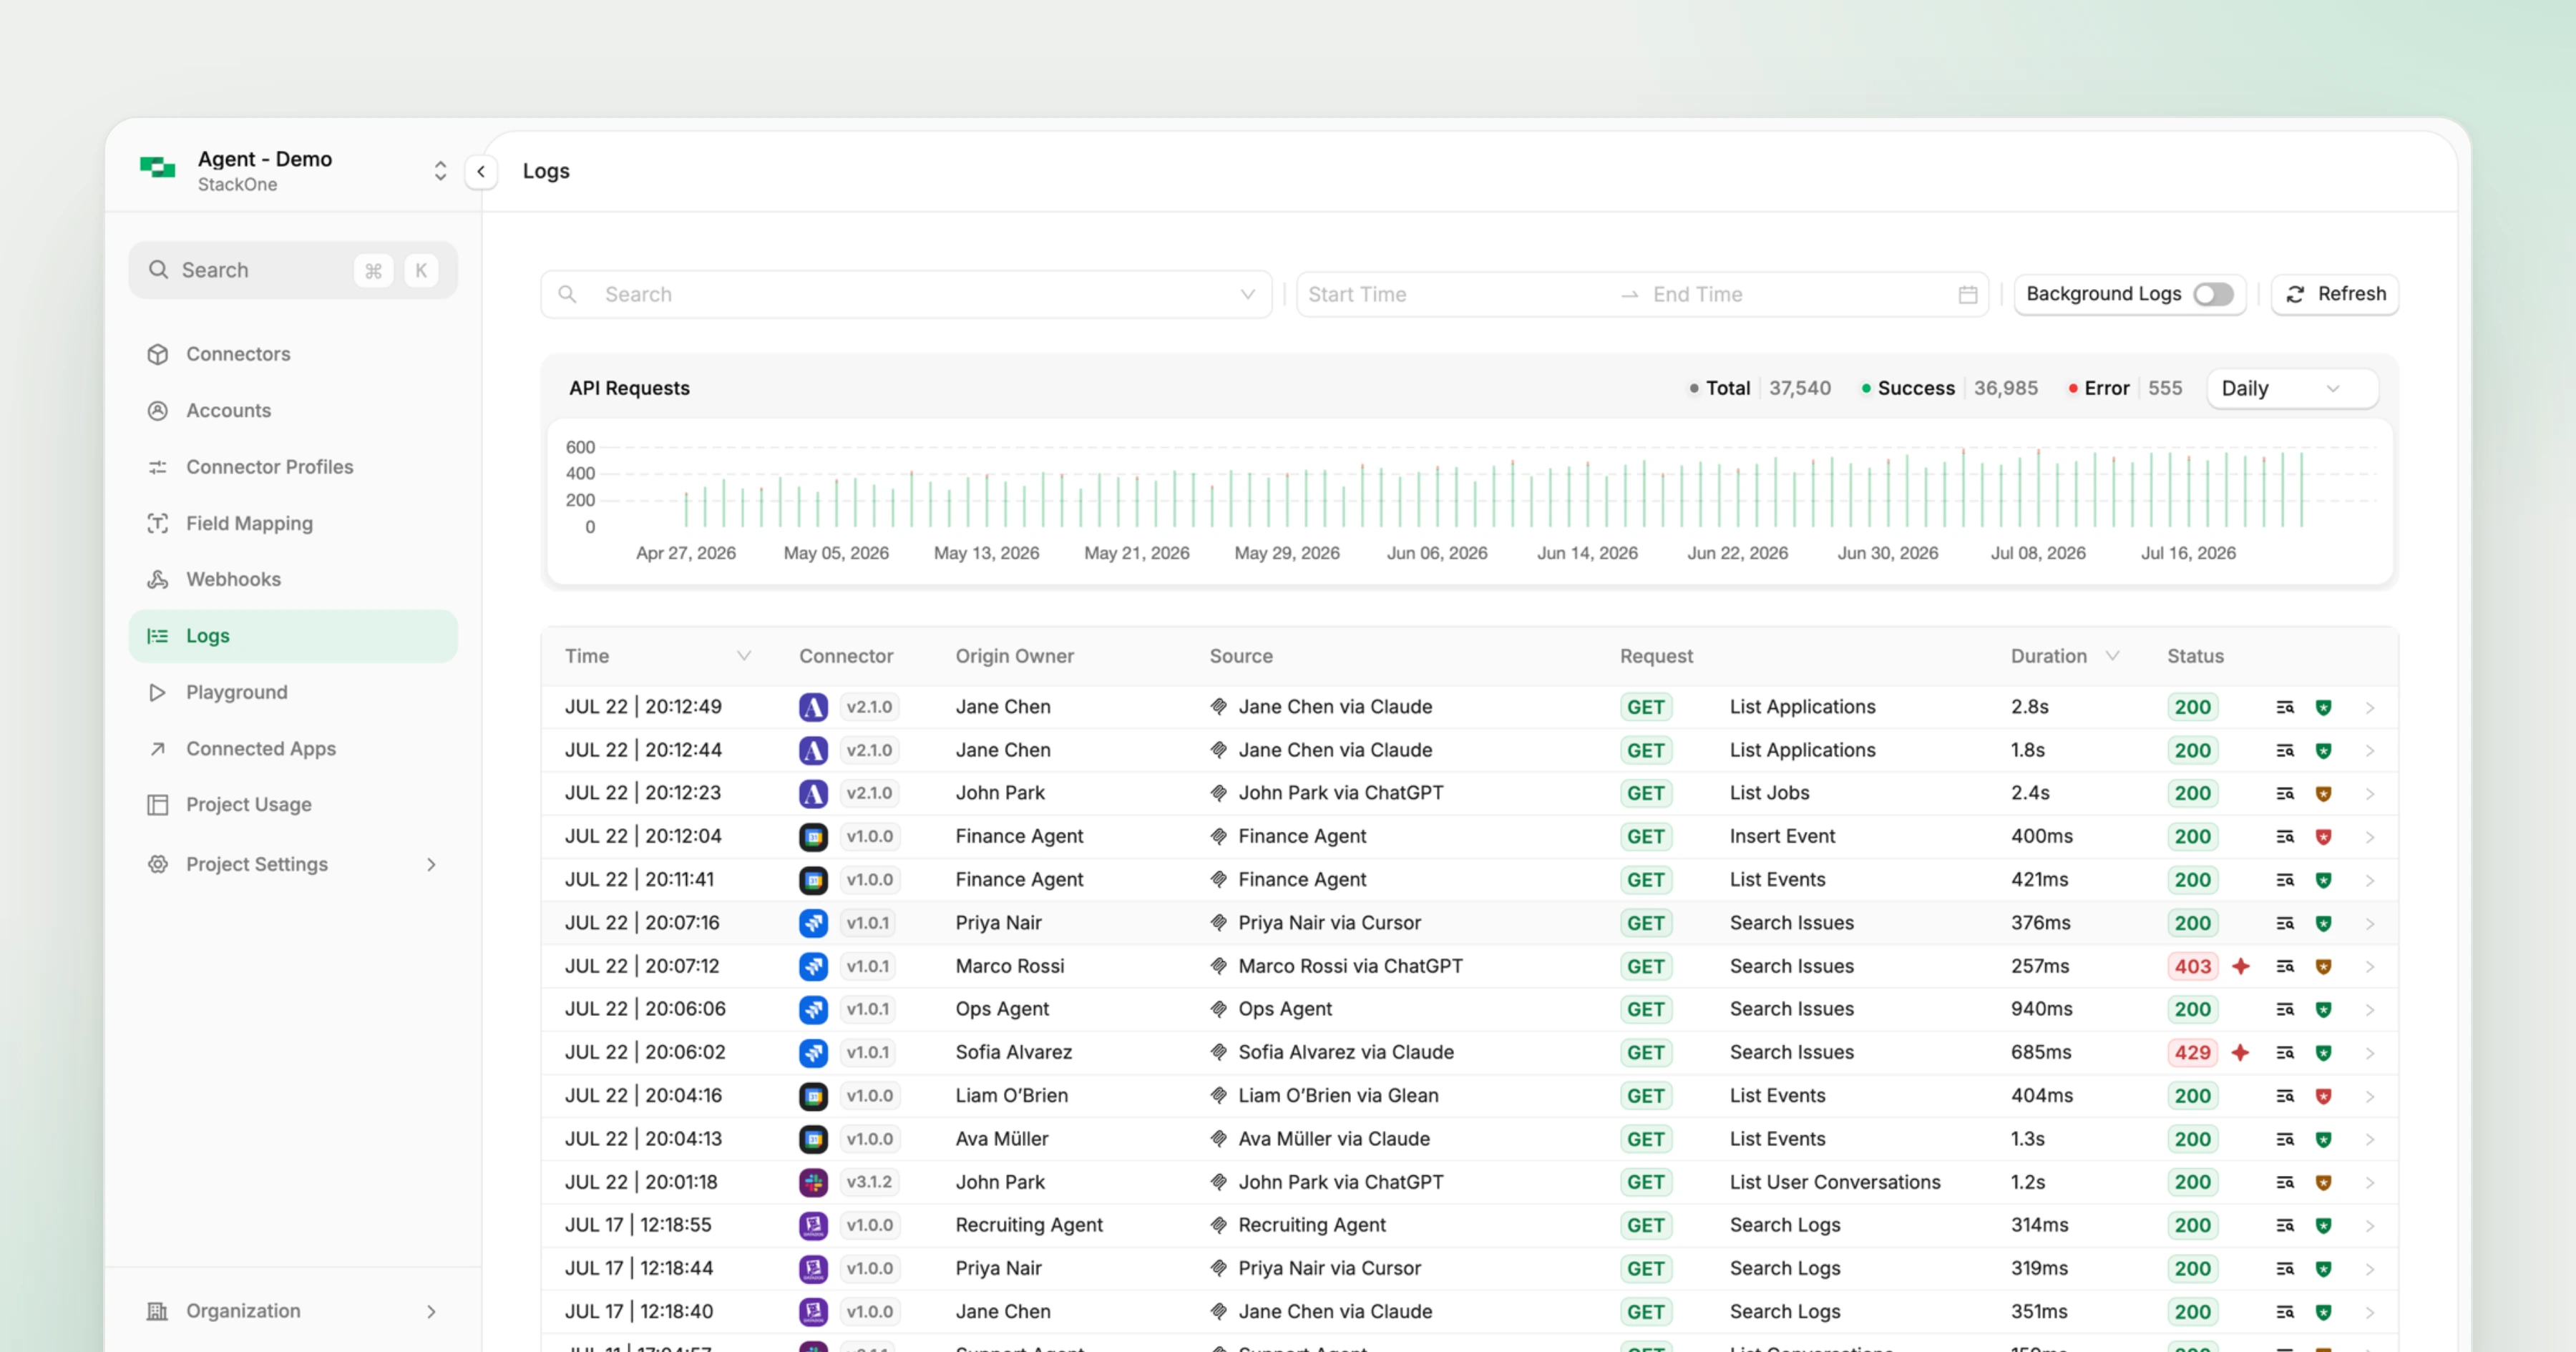
A rebuilt Logs page and public API show every tool call your agents make, with connector versions, Defender verdicts and step-by-step traces.
Read about StackOne Logs
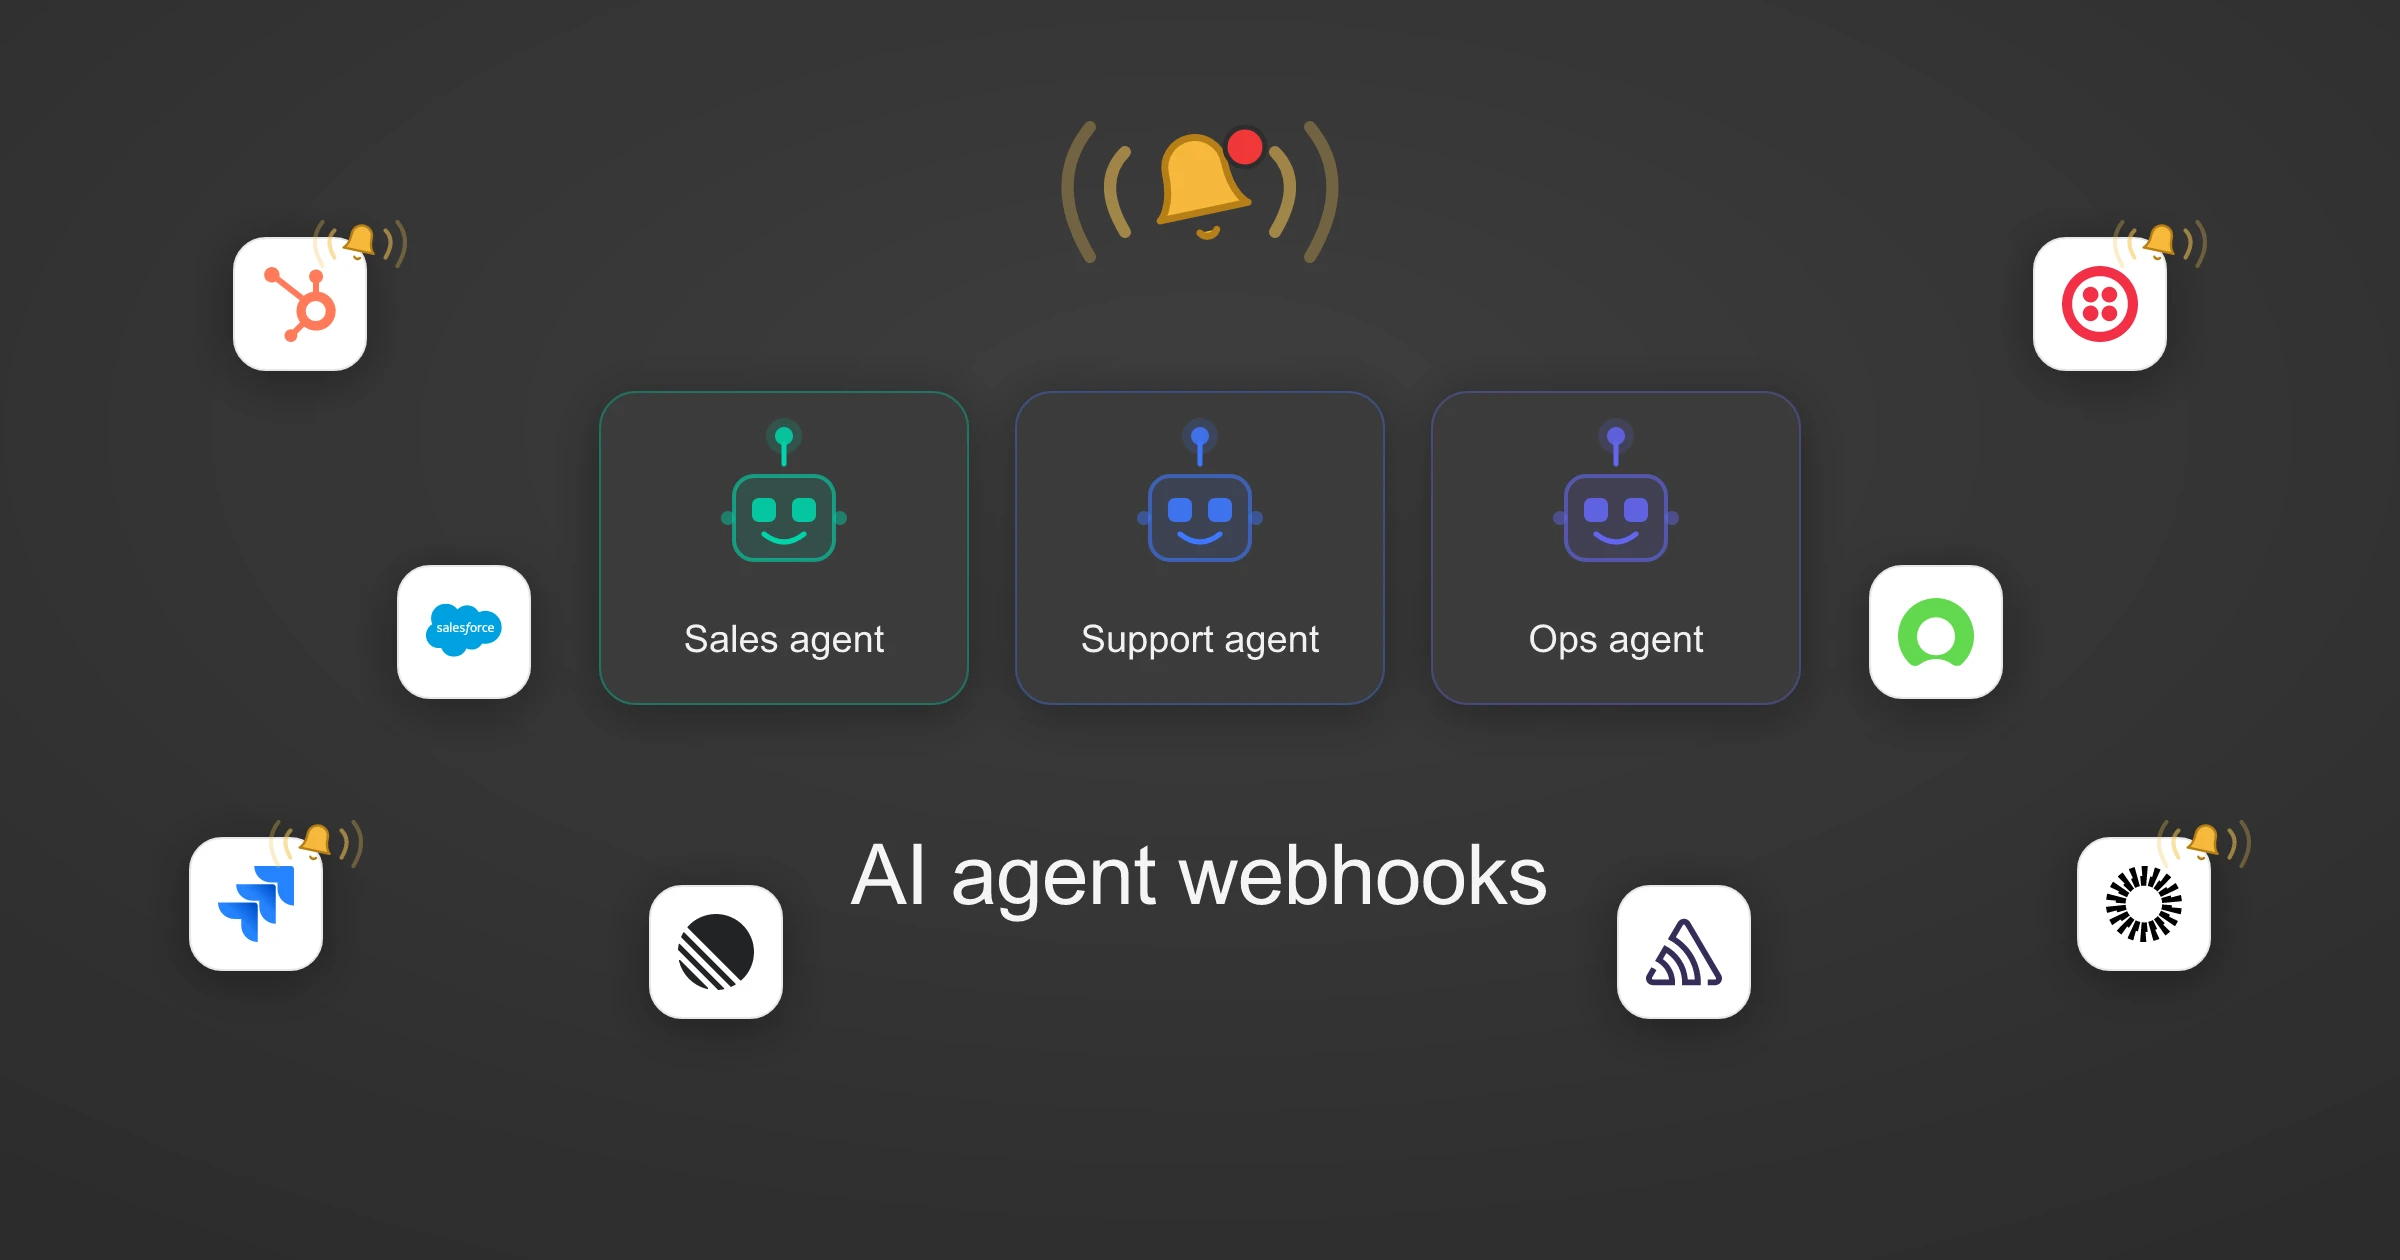
Get real-time events from your connectors, filter and reshape them in flight, and send them to your receivers, so agents act only on what matters.
Read about Native WebhooksStackOne connectors now support semver, per-config pinning, and immutable pushes. Pin production to a specific version, test in sandbox, and promote when ready.
Read about Connector Versioning
Semantic tool discovery for agents: 92.8% Hit@1 on scoped search and 57.3% globally, against 44% for Anthropic's native tool use.
Read about Semantic Tool Discovery
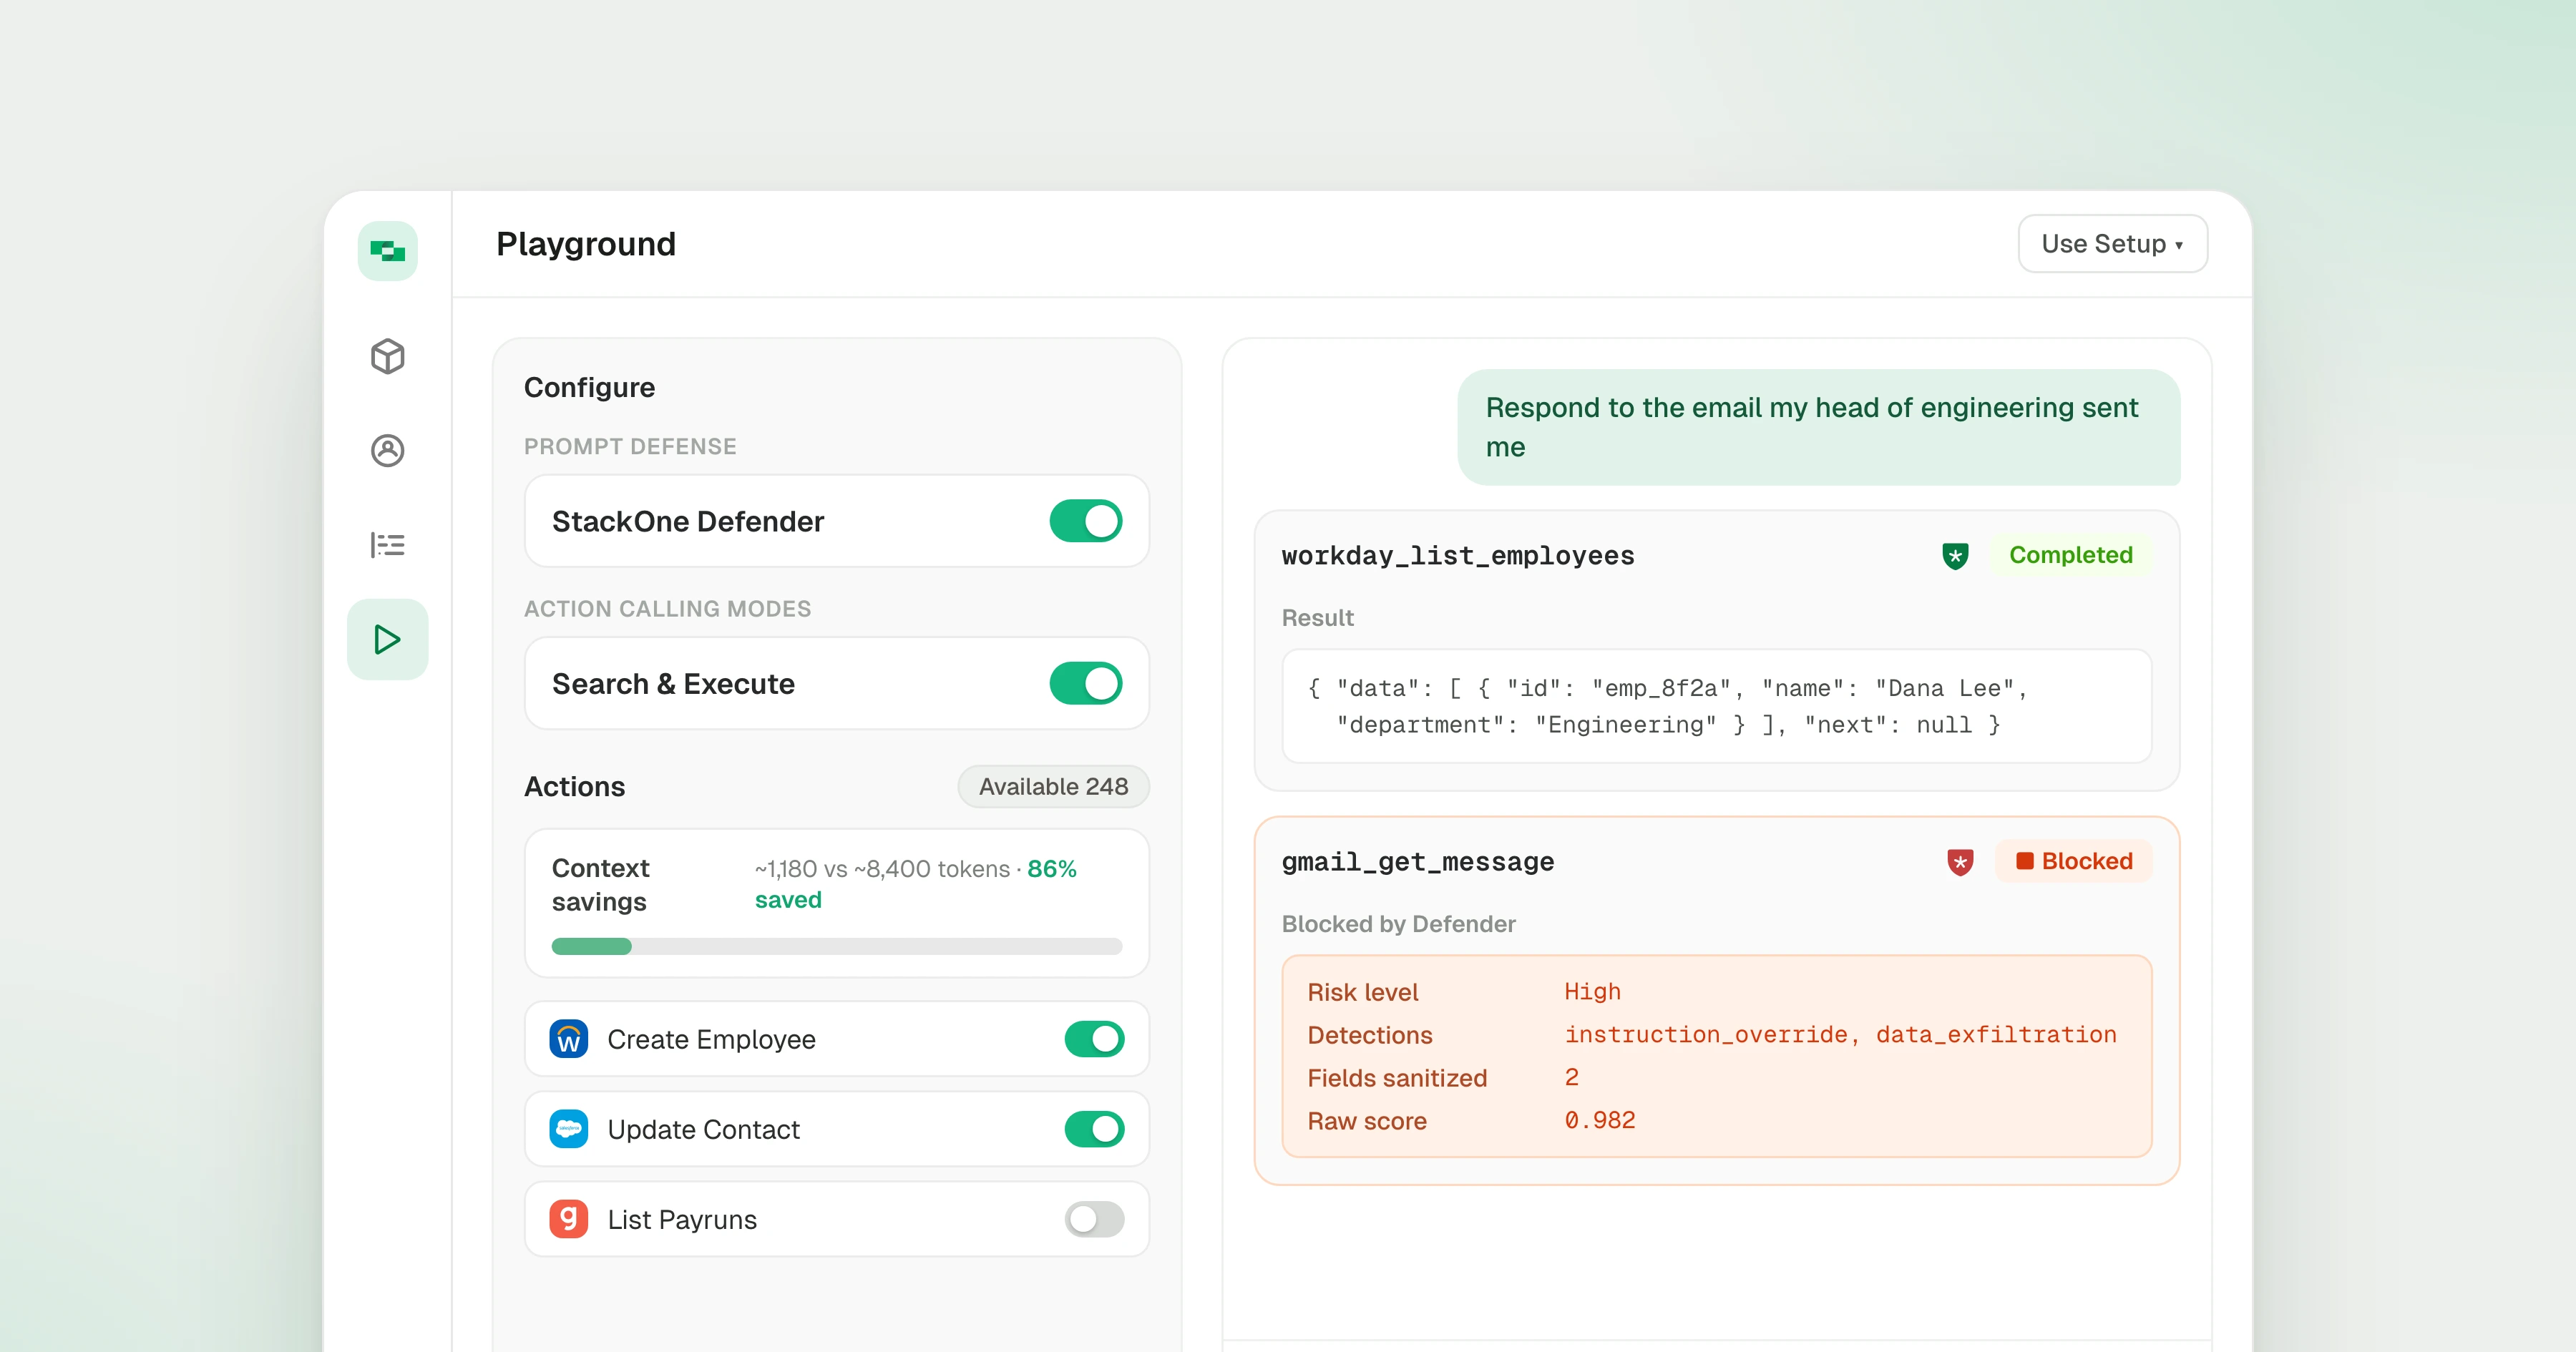
Try Search & Execute in the Playground to see the token savings, and watch Defender check every tool result for prompt injection.
Read about the Playground
SAML 2.0 single sign-on for StackOne. Admins connect their identity provider once, and users sign in with their existing corporate credentials.
Read about SAML SSOProtect your AI agents from prompt injection. Open source, 88.7% accurate, runs anywhere with no external API calls. npm install @stackone/defender.
Read about Defender
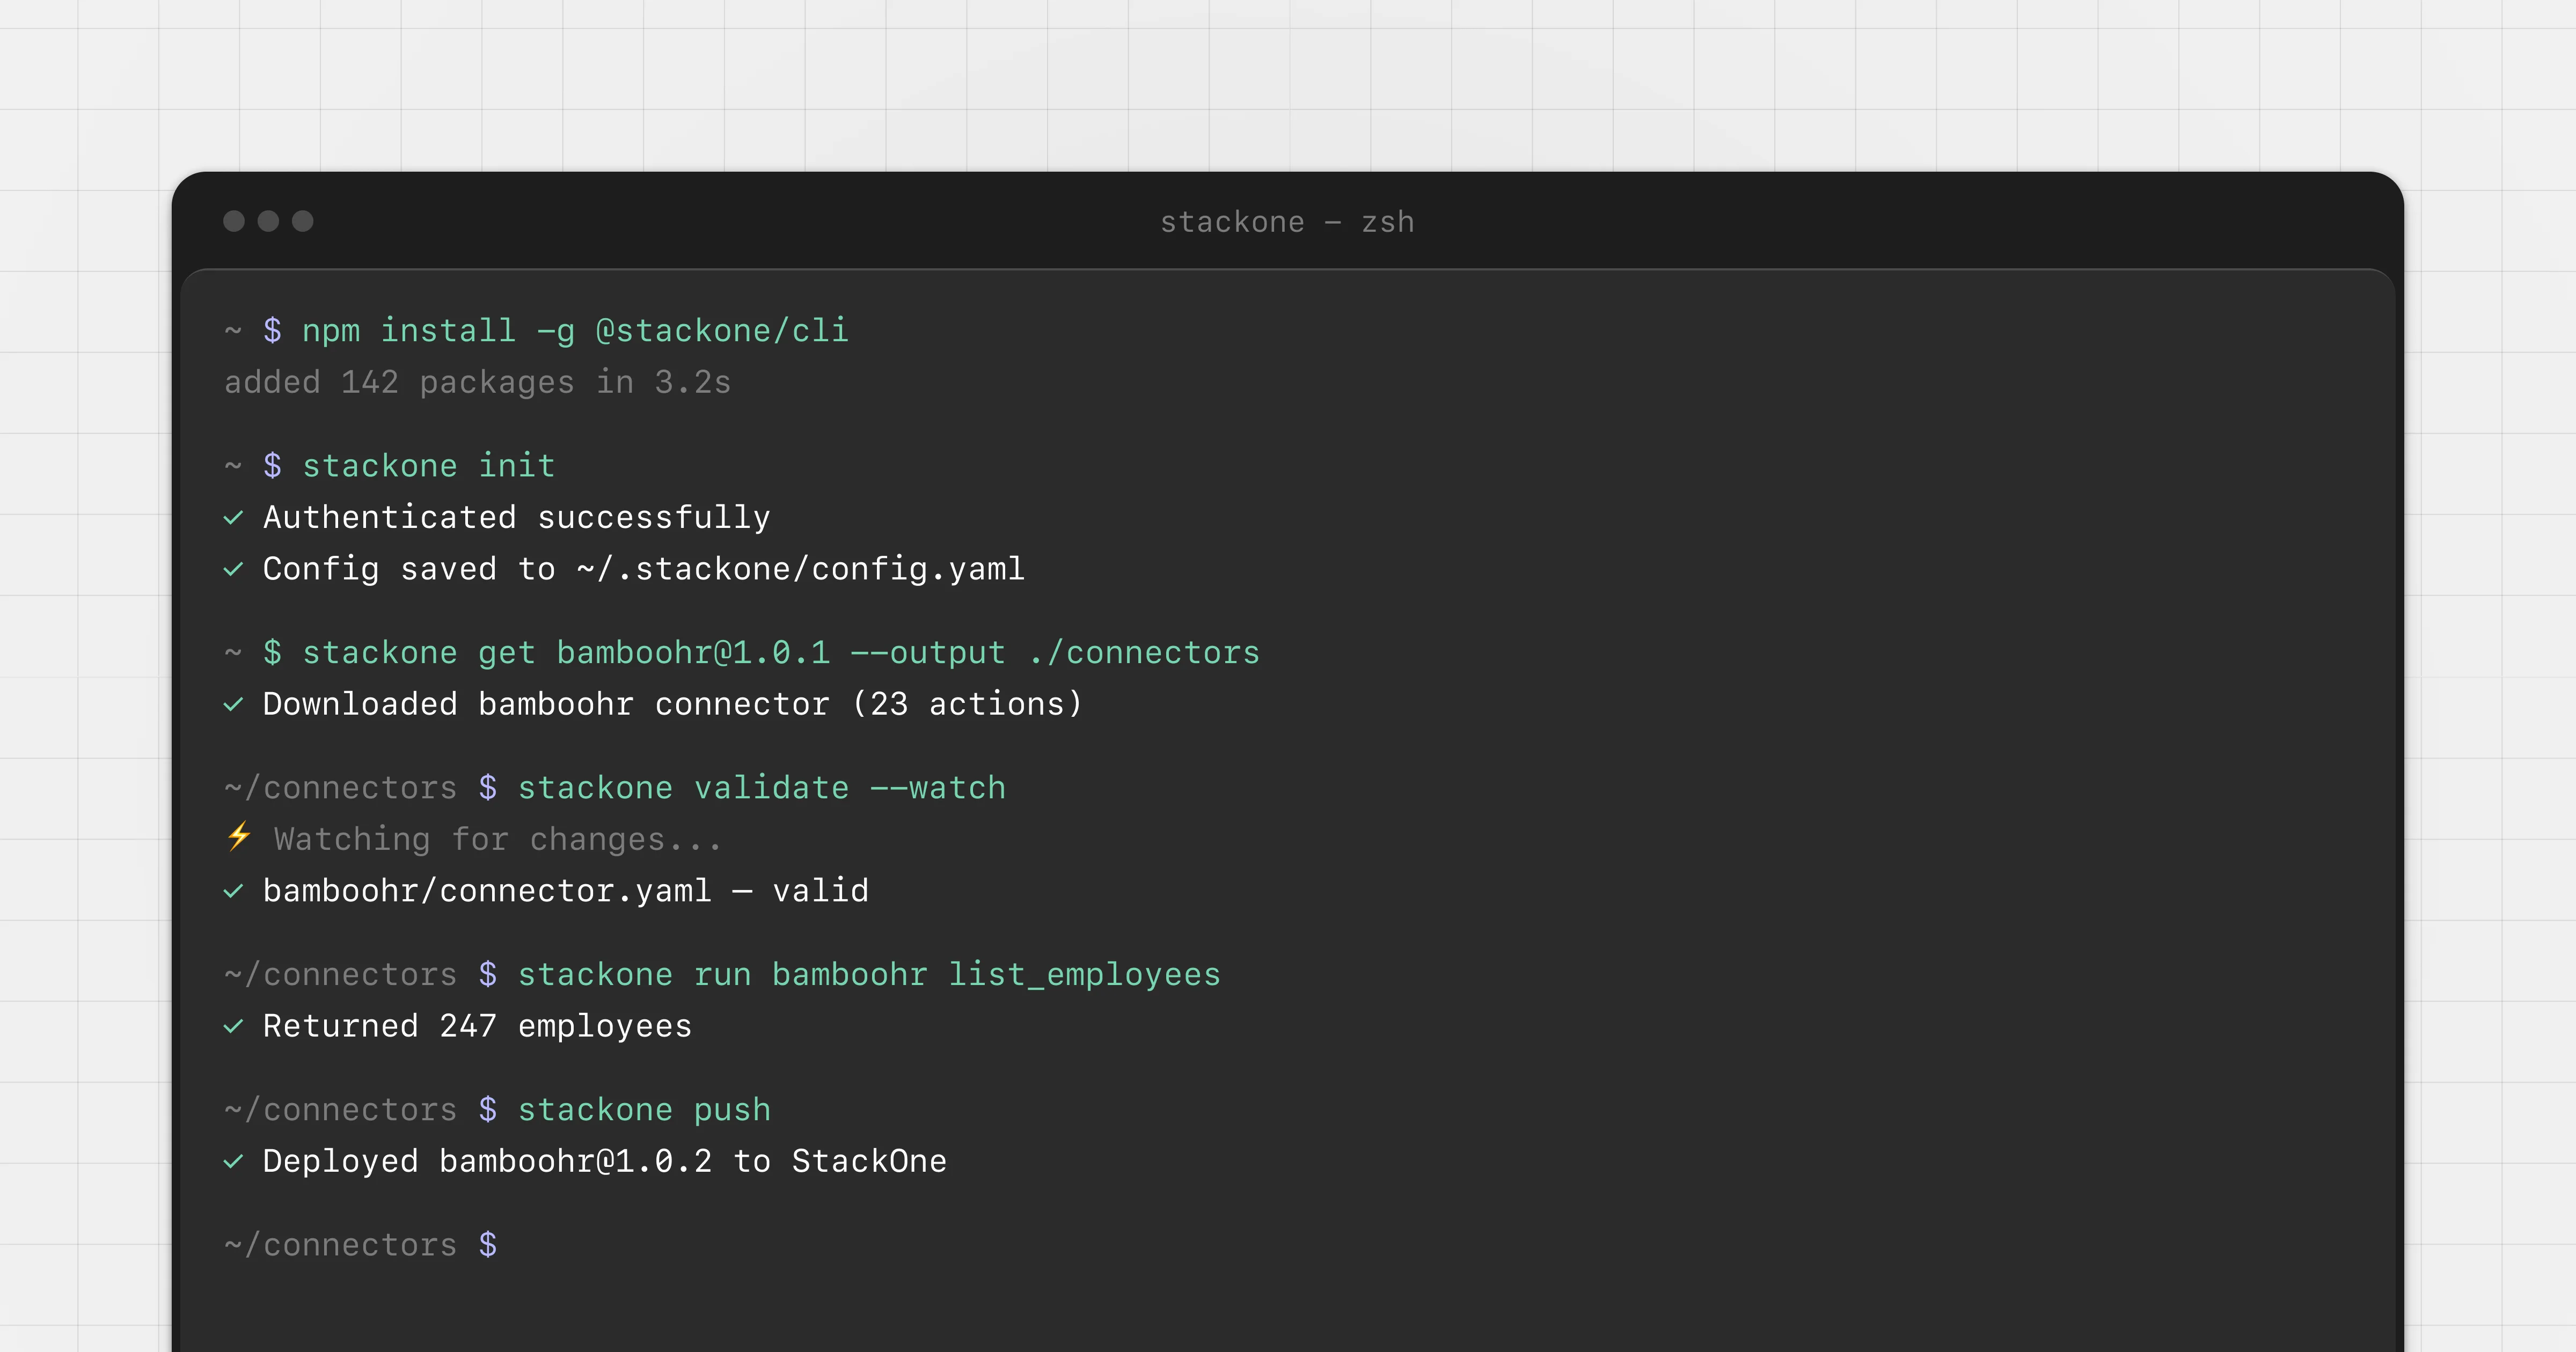
The StackOne CLI lets you build, test and deploy connectors from your terminal: pull connectors, validate configs, test actions locally and push changes.
Read about the CLI
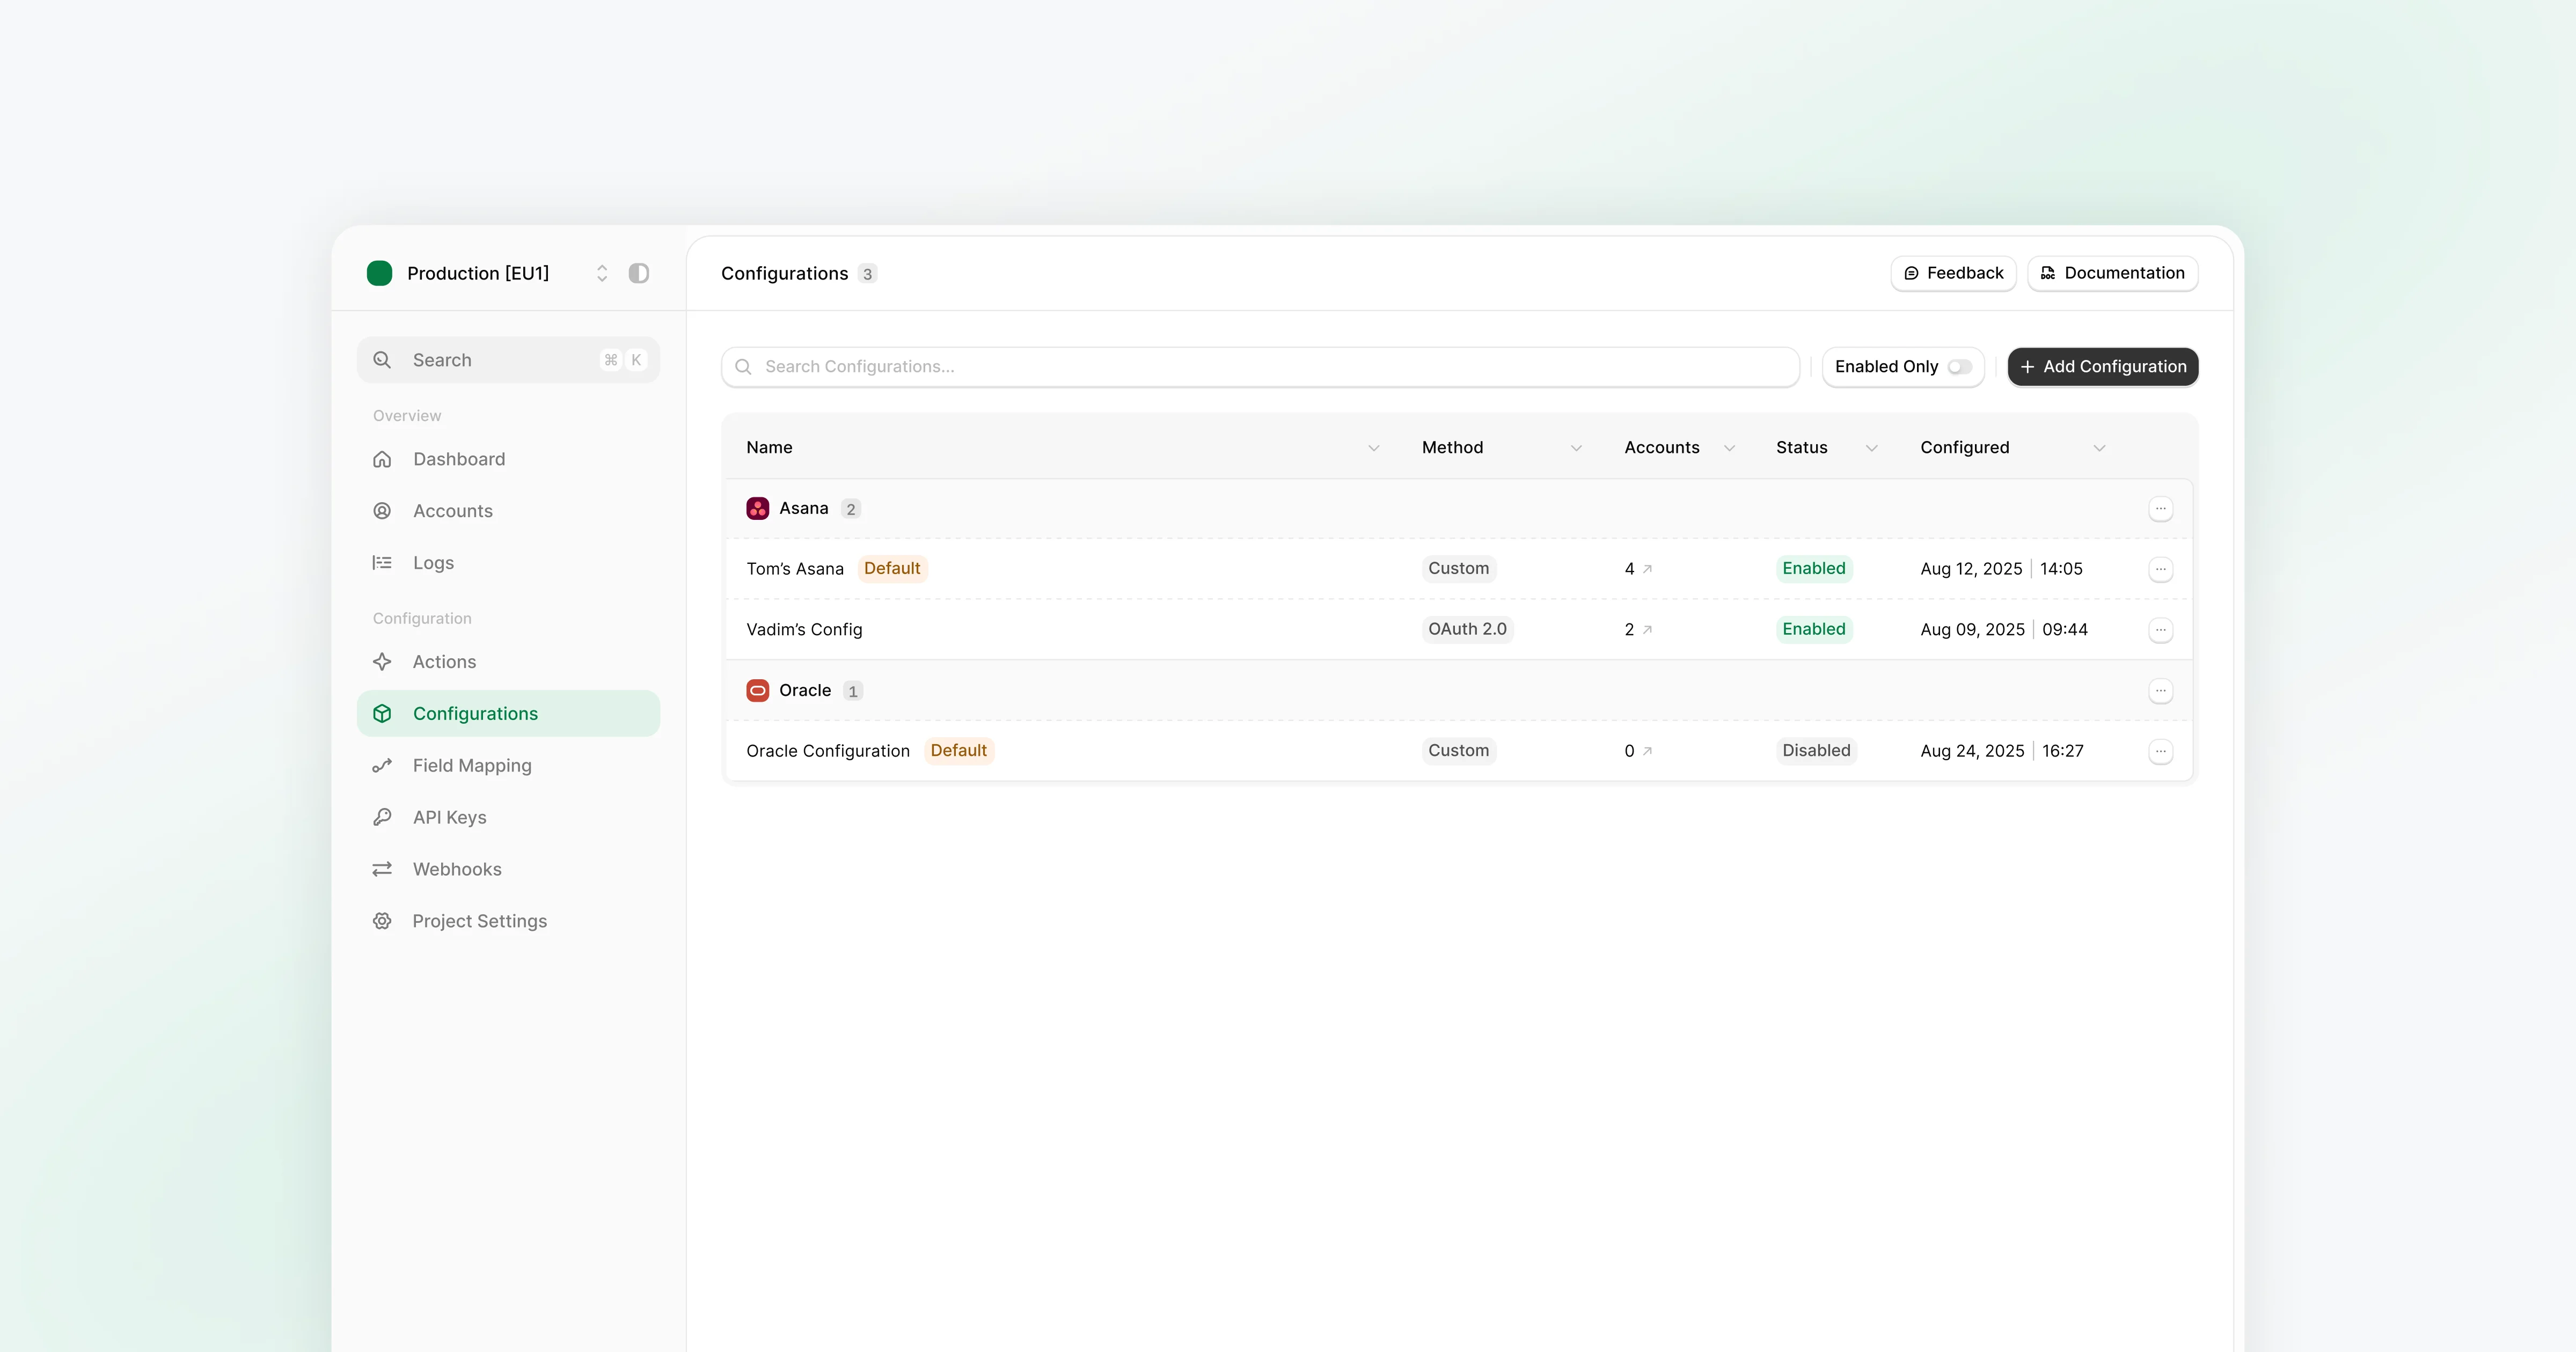
Configuring integrations just got a major upgrade. Create and manage multiple configurations per integration, each with its own authentication and permission scopes.
Read about Integration Configs
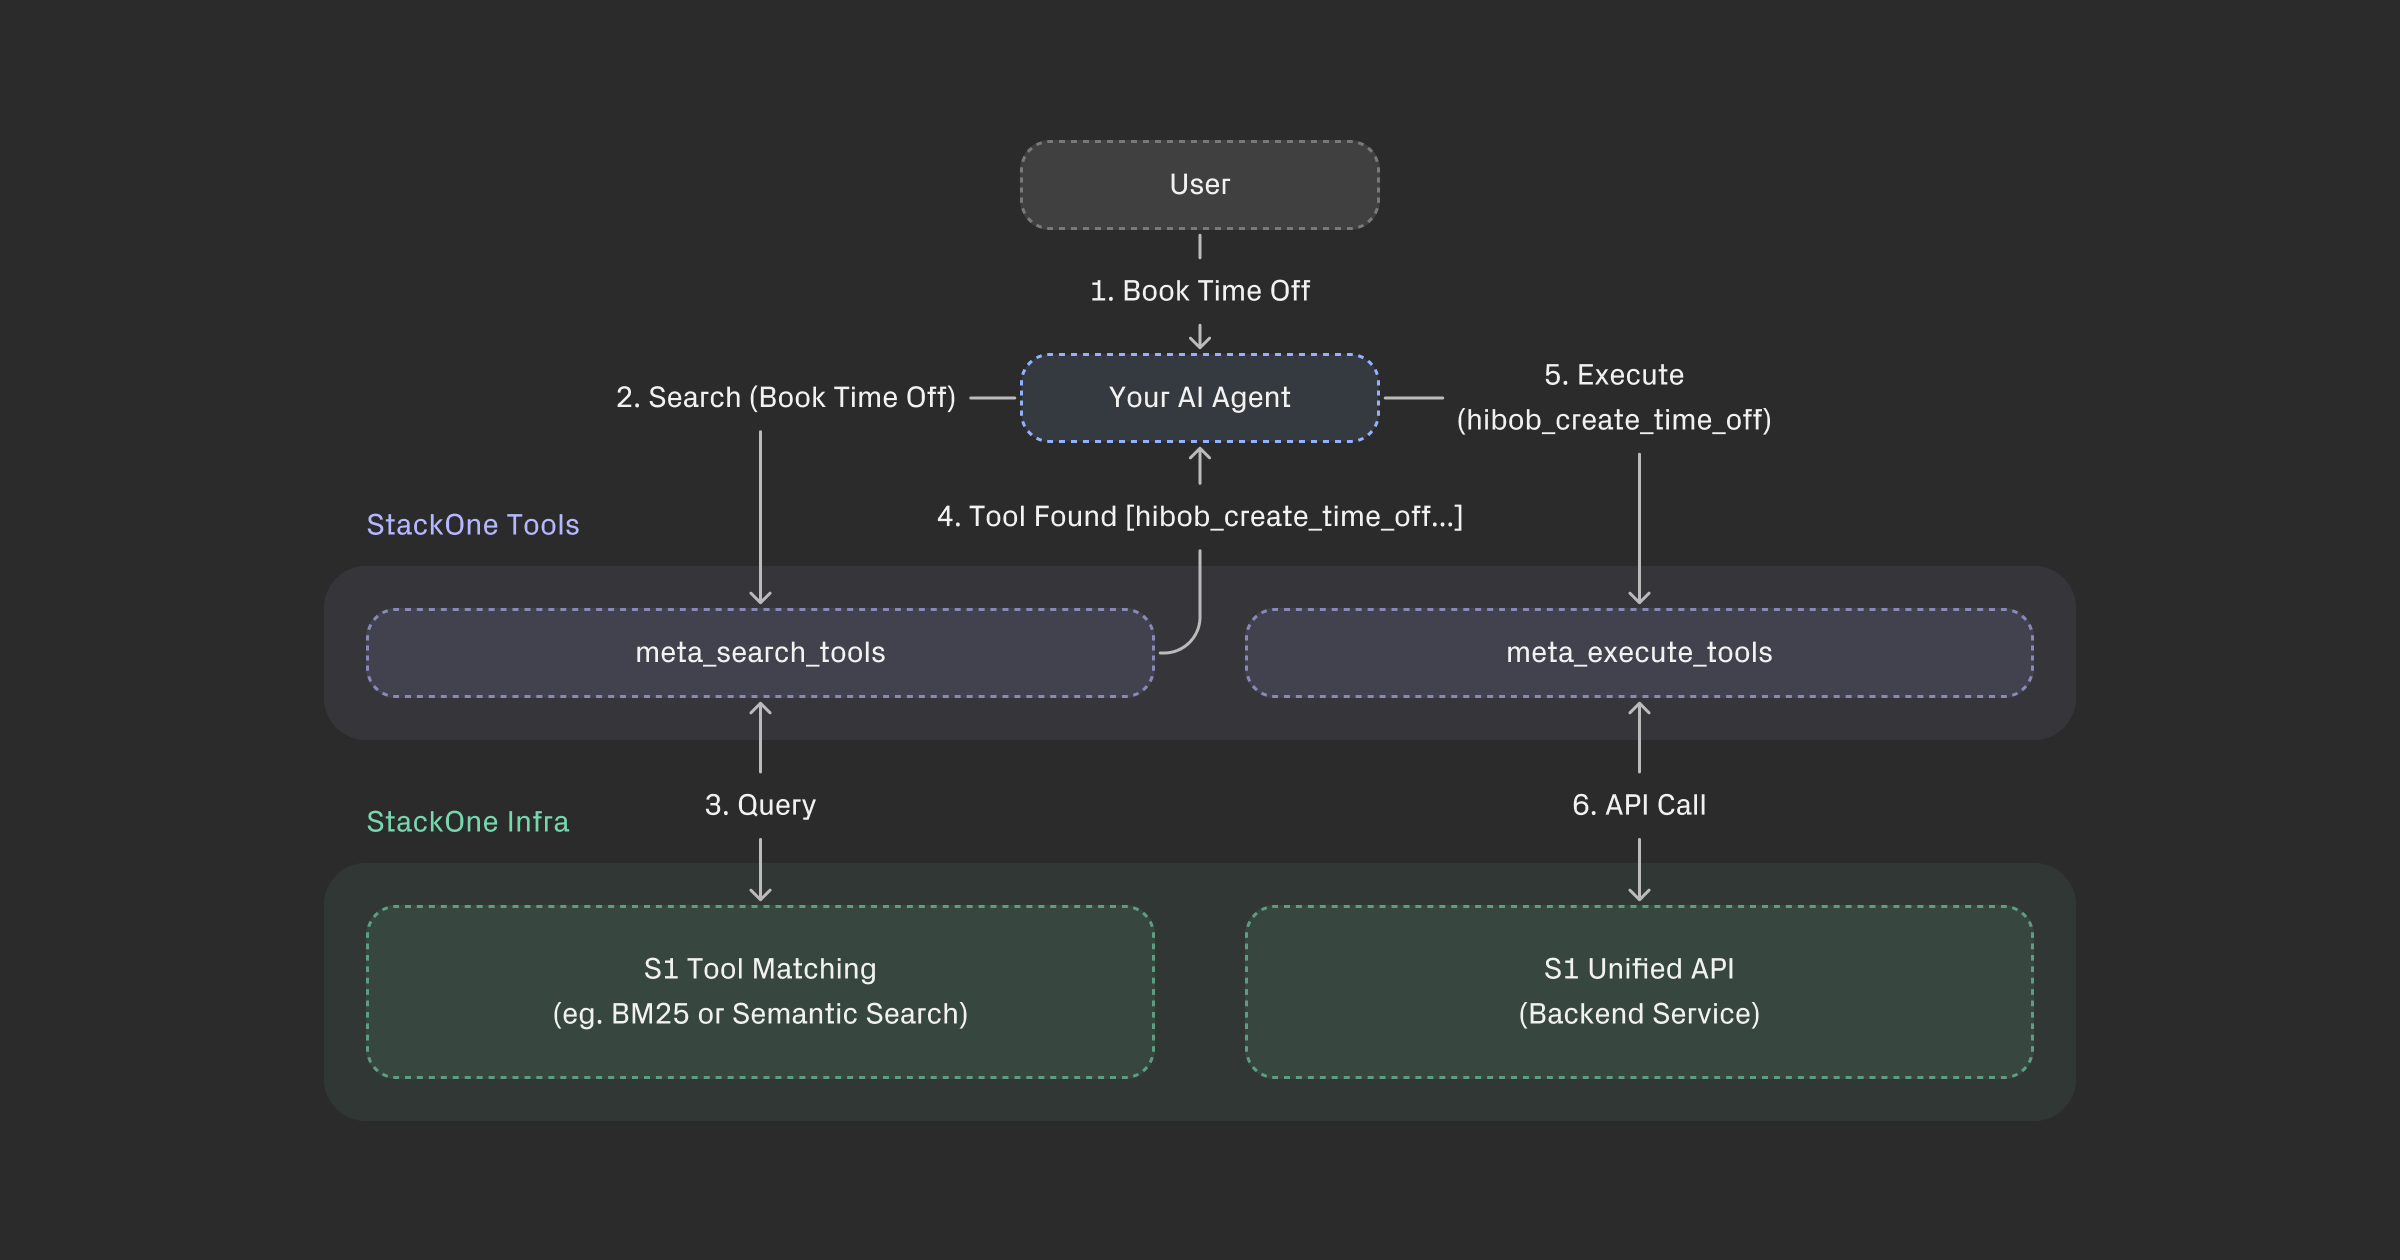
Introducing search_tools: two meta-tools that replace hundreds of tool definitions, cutting context bloat and improving agent accuracy.
Read about Tools Discovery
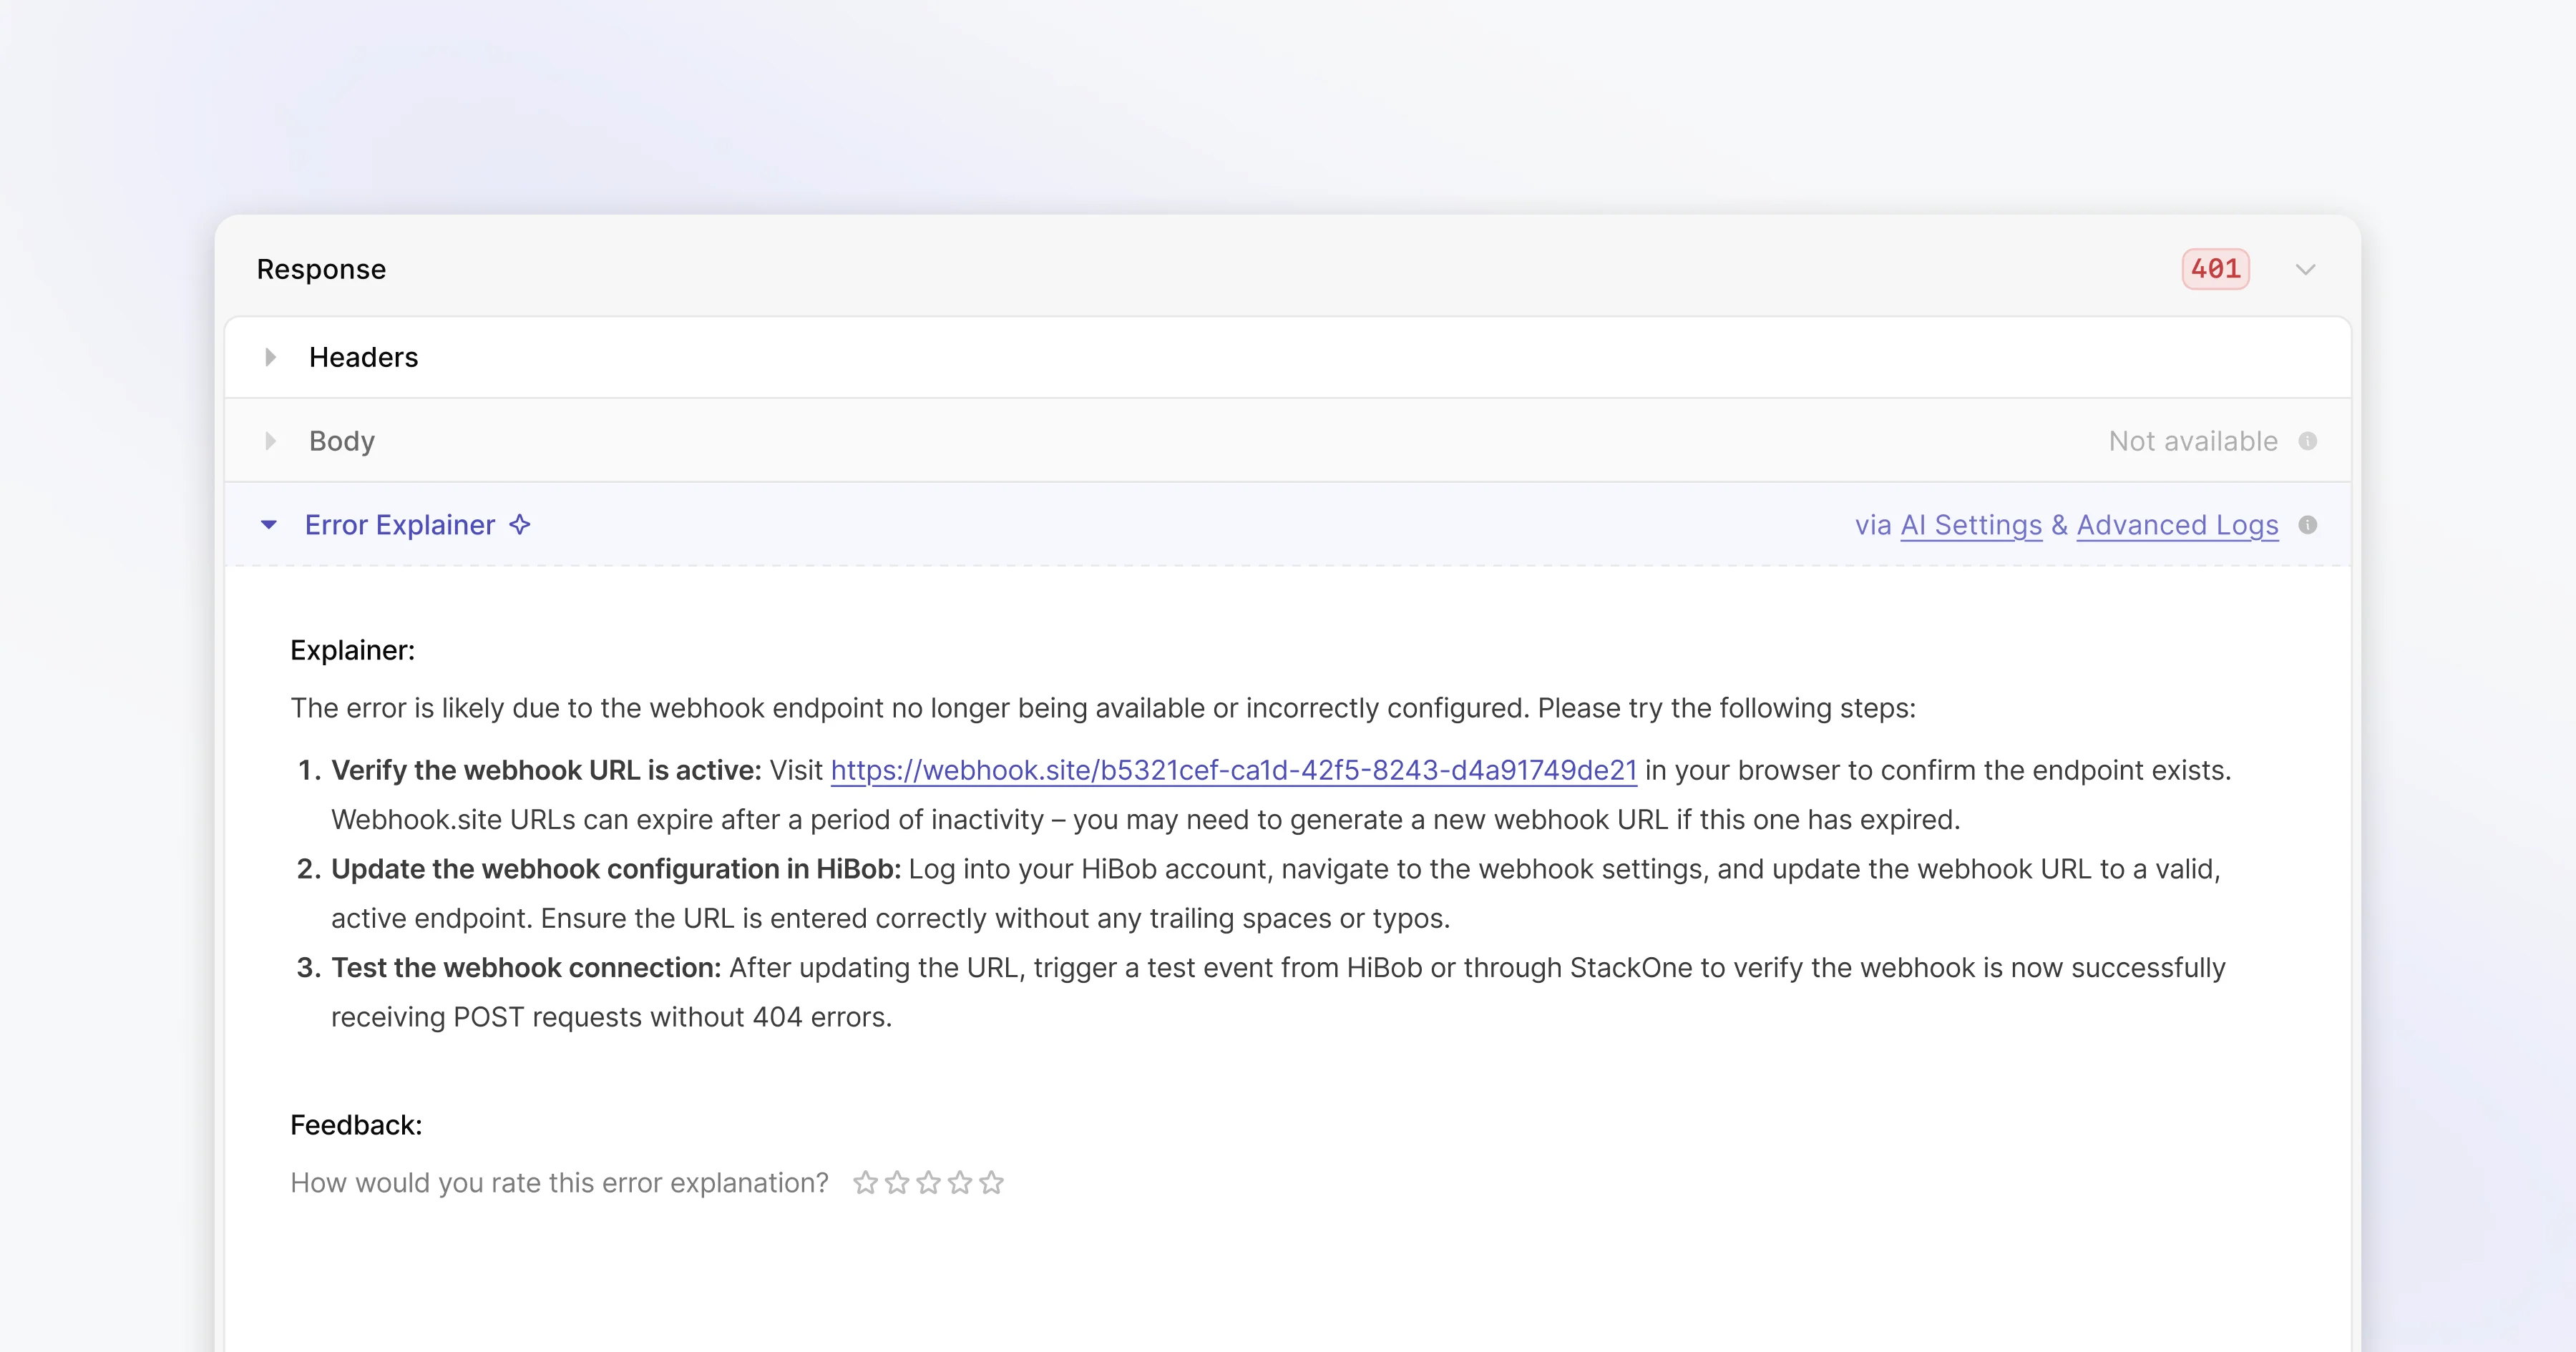
The new Error Explainer uses AI to instantly translate error messages into actionable explanations, enriched with data from 800+ documentations indexed by StackOne.
Read about Error Explainer
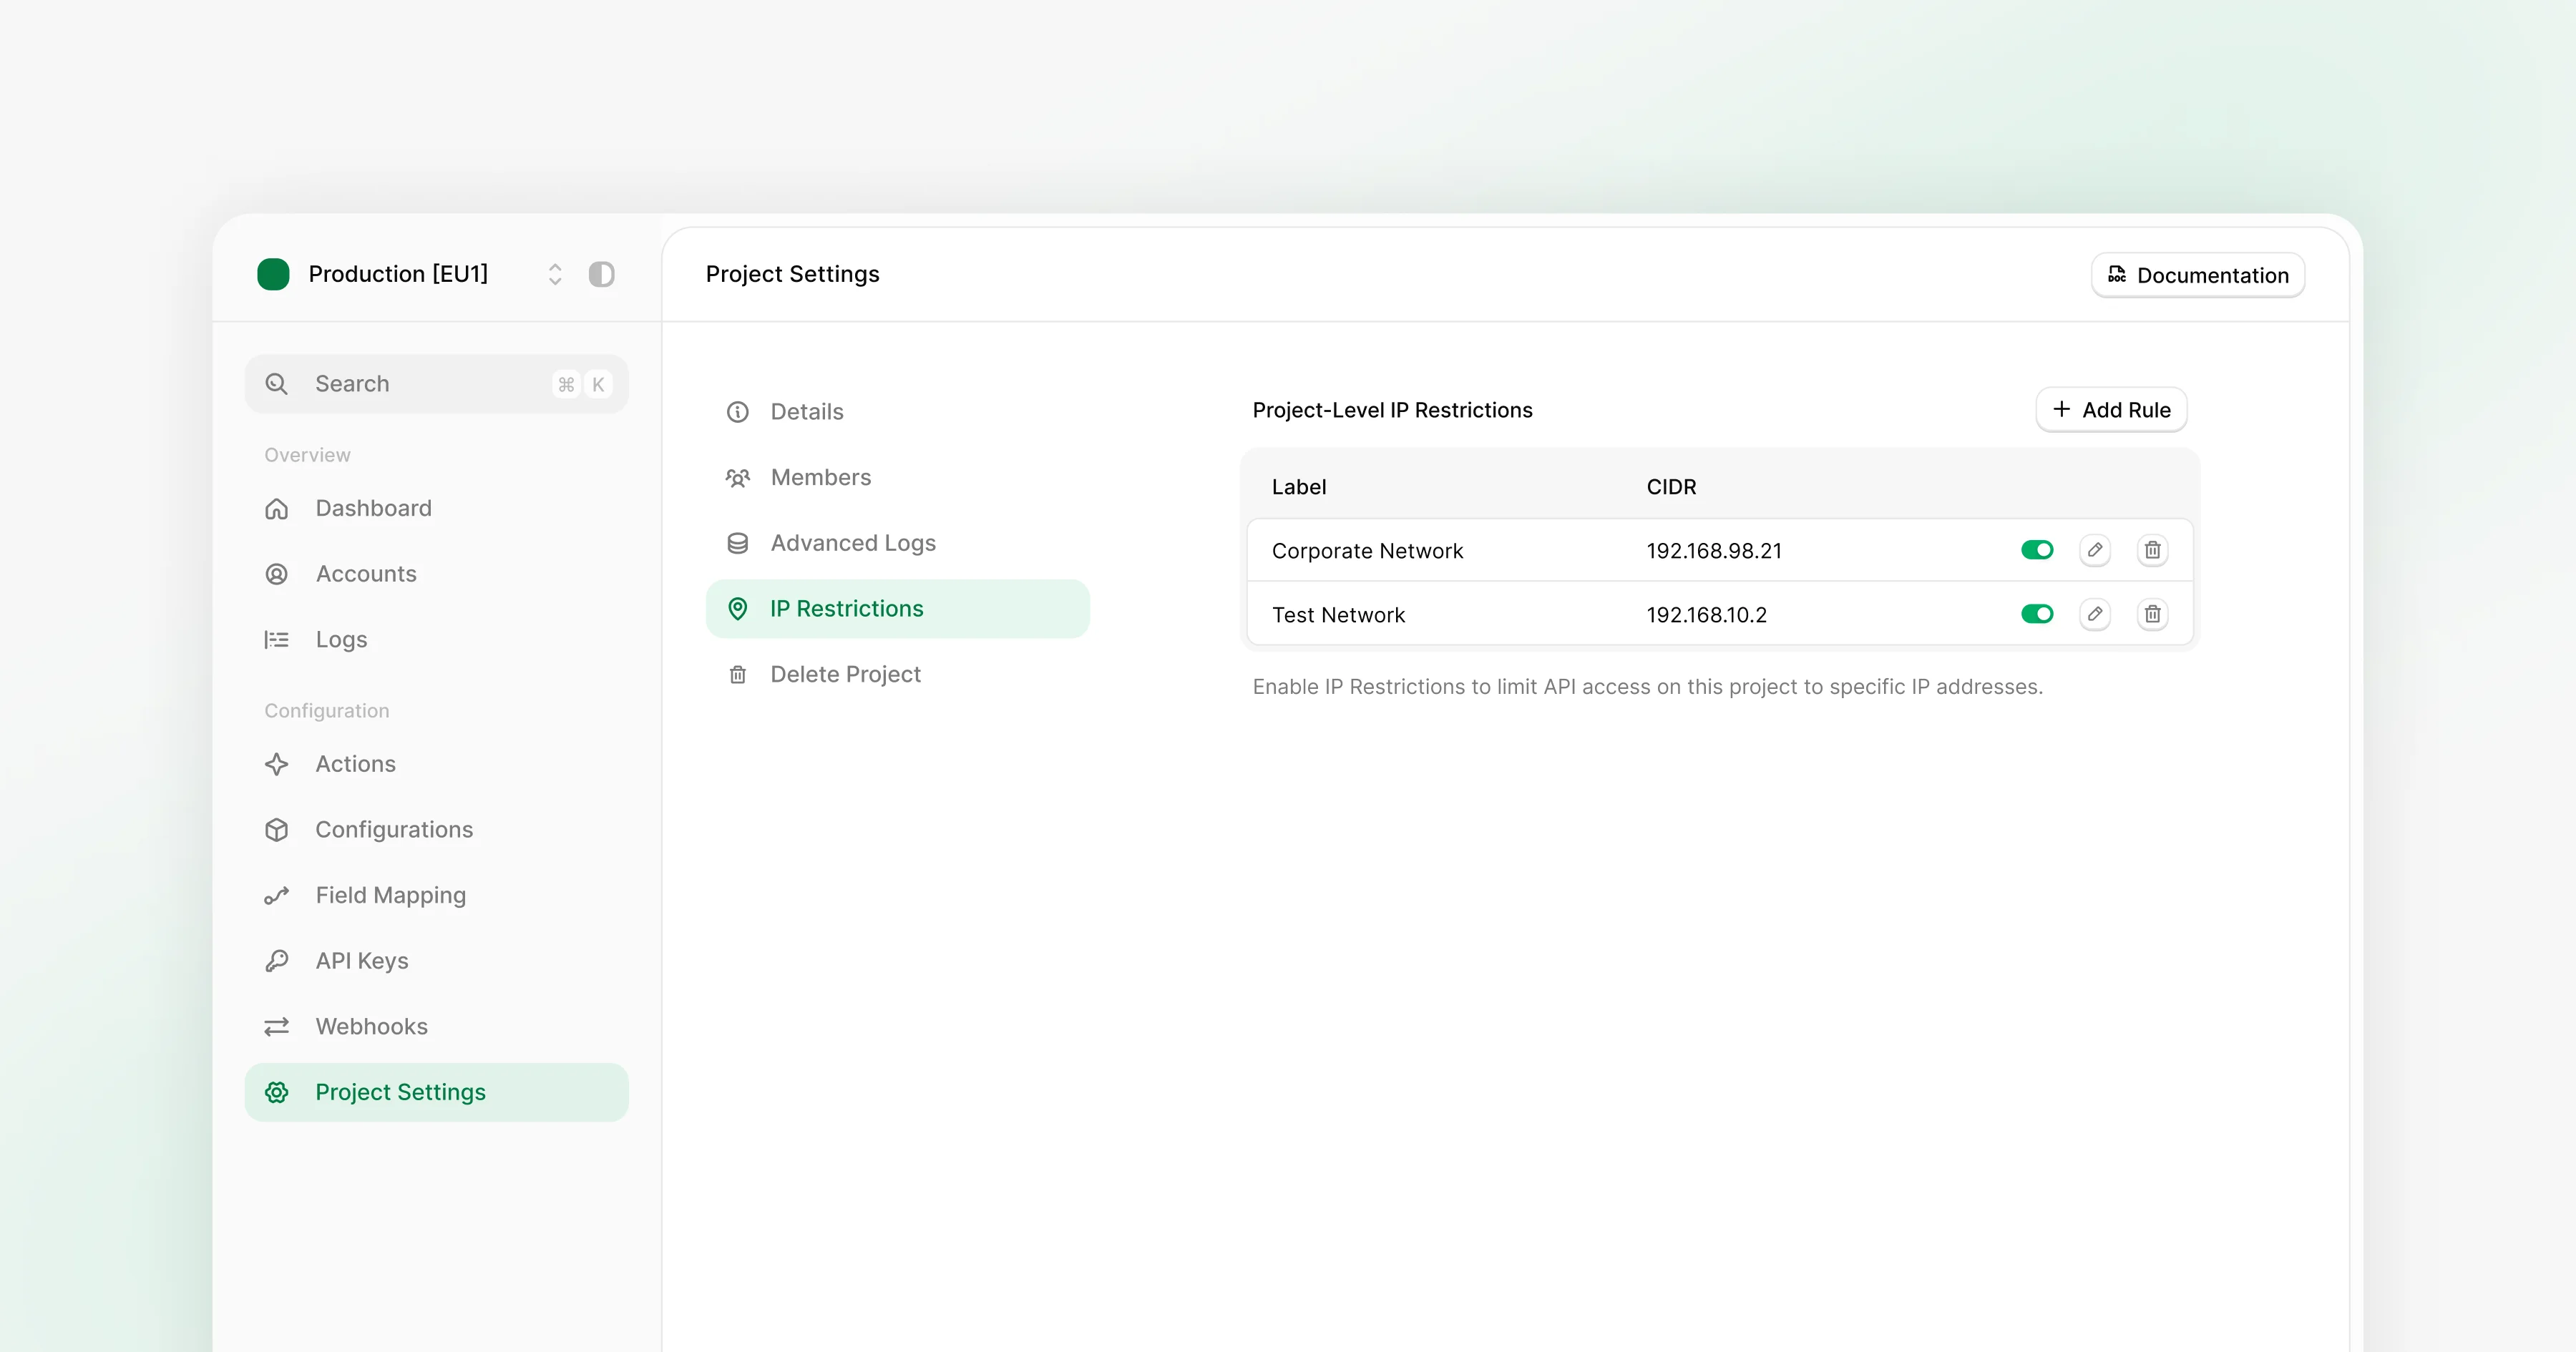
Projects can now be secured at the network layer by restricting API traffic to approved IPs or ranges, preventing calls from unauthorized origins.
Read about IP Allowlist
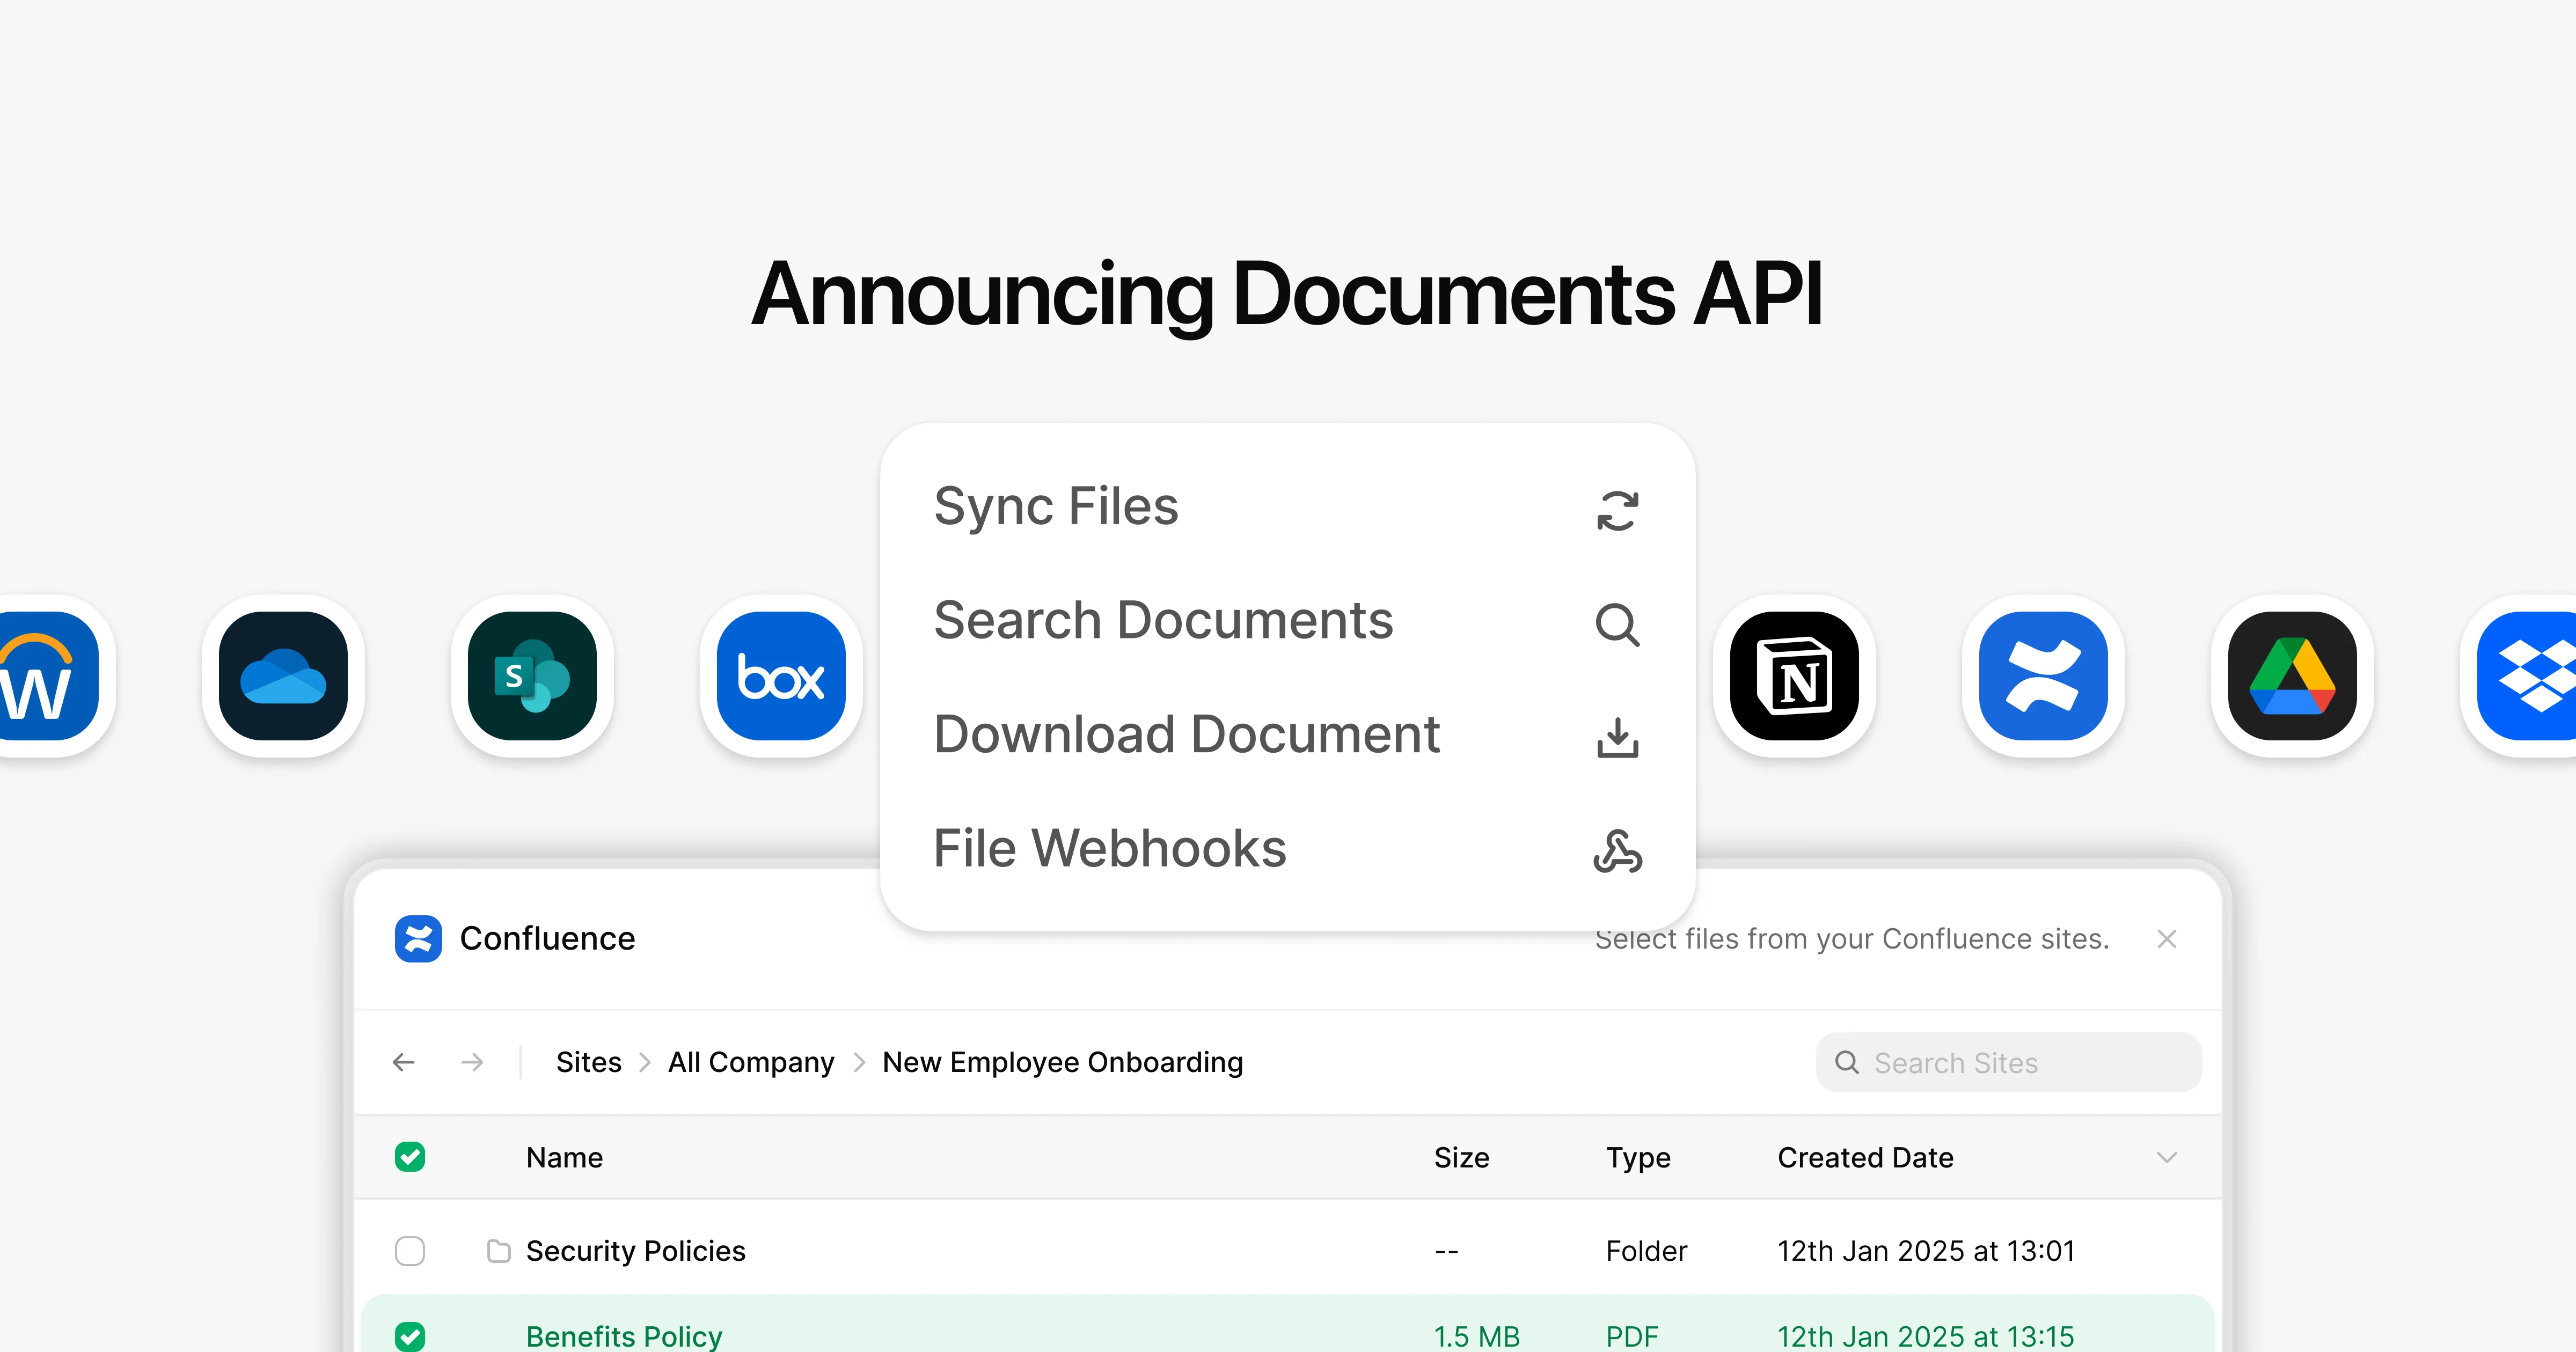
A consistent way to fetch, upload, and manage content across knowledge bases and file storage systems like Notion, Google Drive, and SharePoint.
Read about Documents API
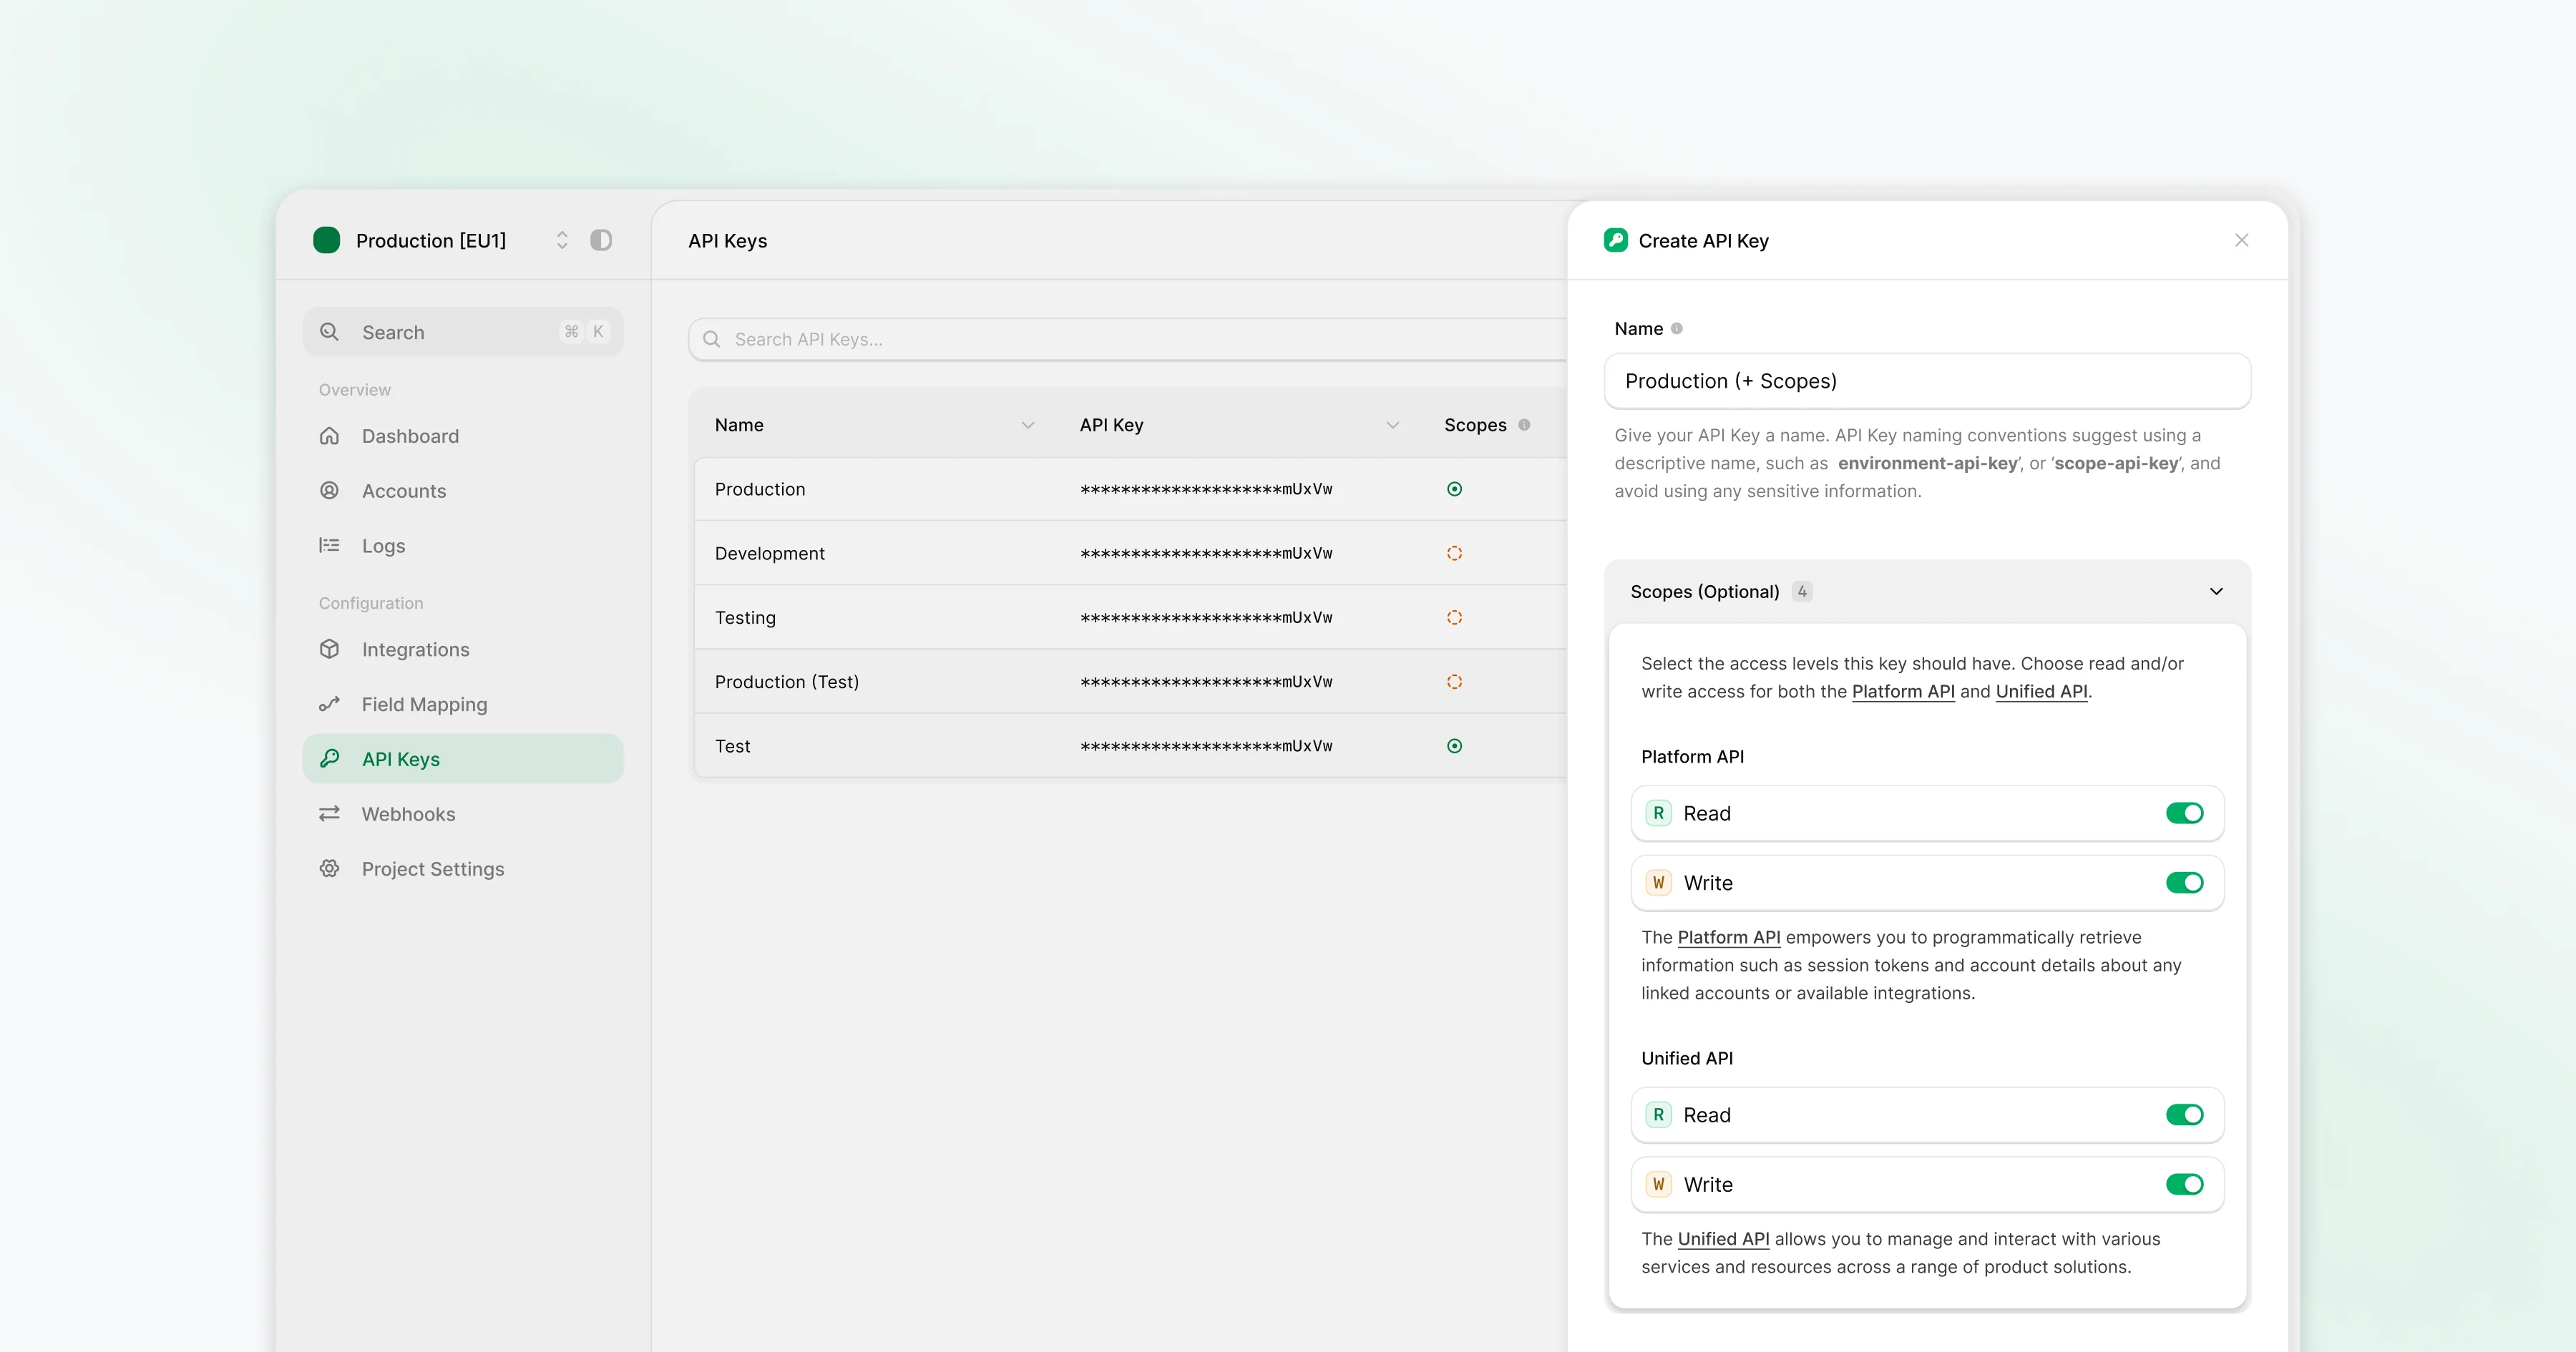
API keys can now be created with granular scopes that limit what each key is allowed to do, improving security posture.
Read about API Key Scopes
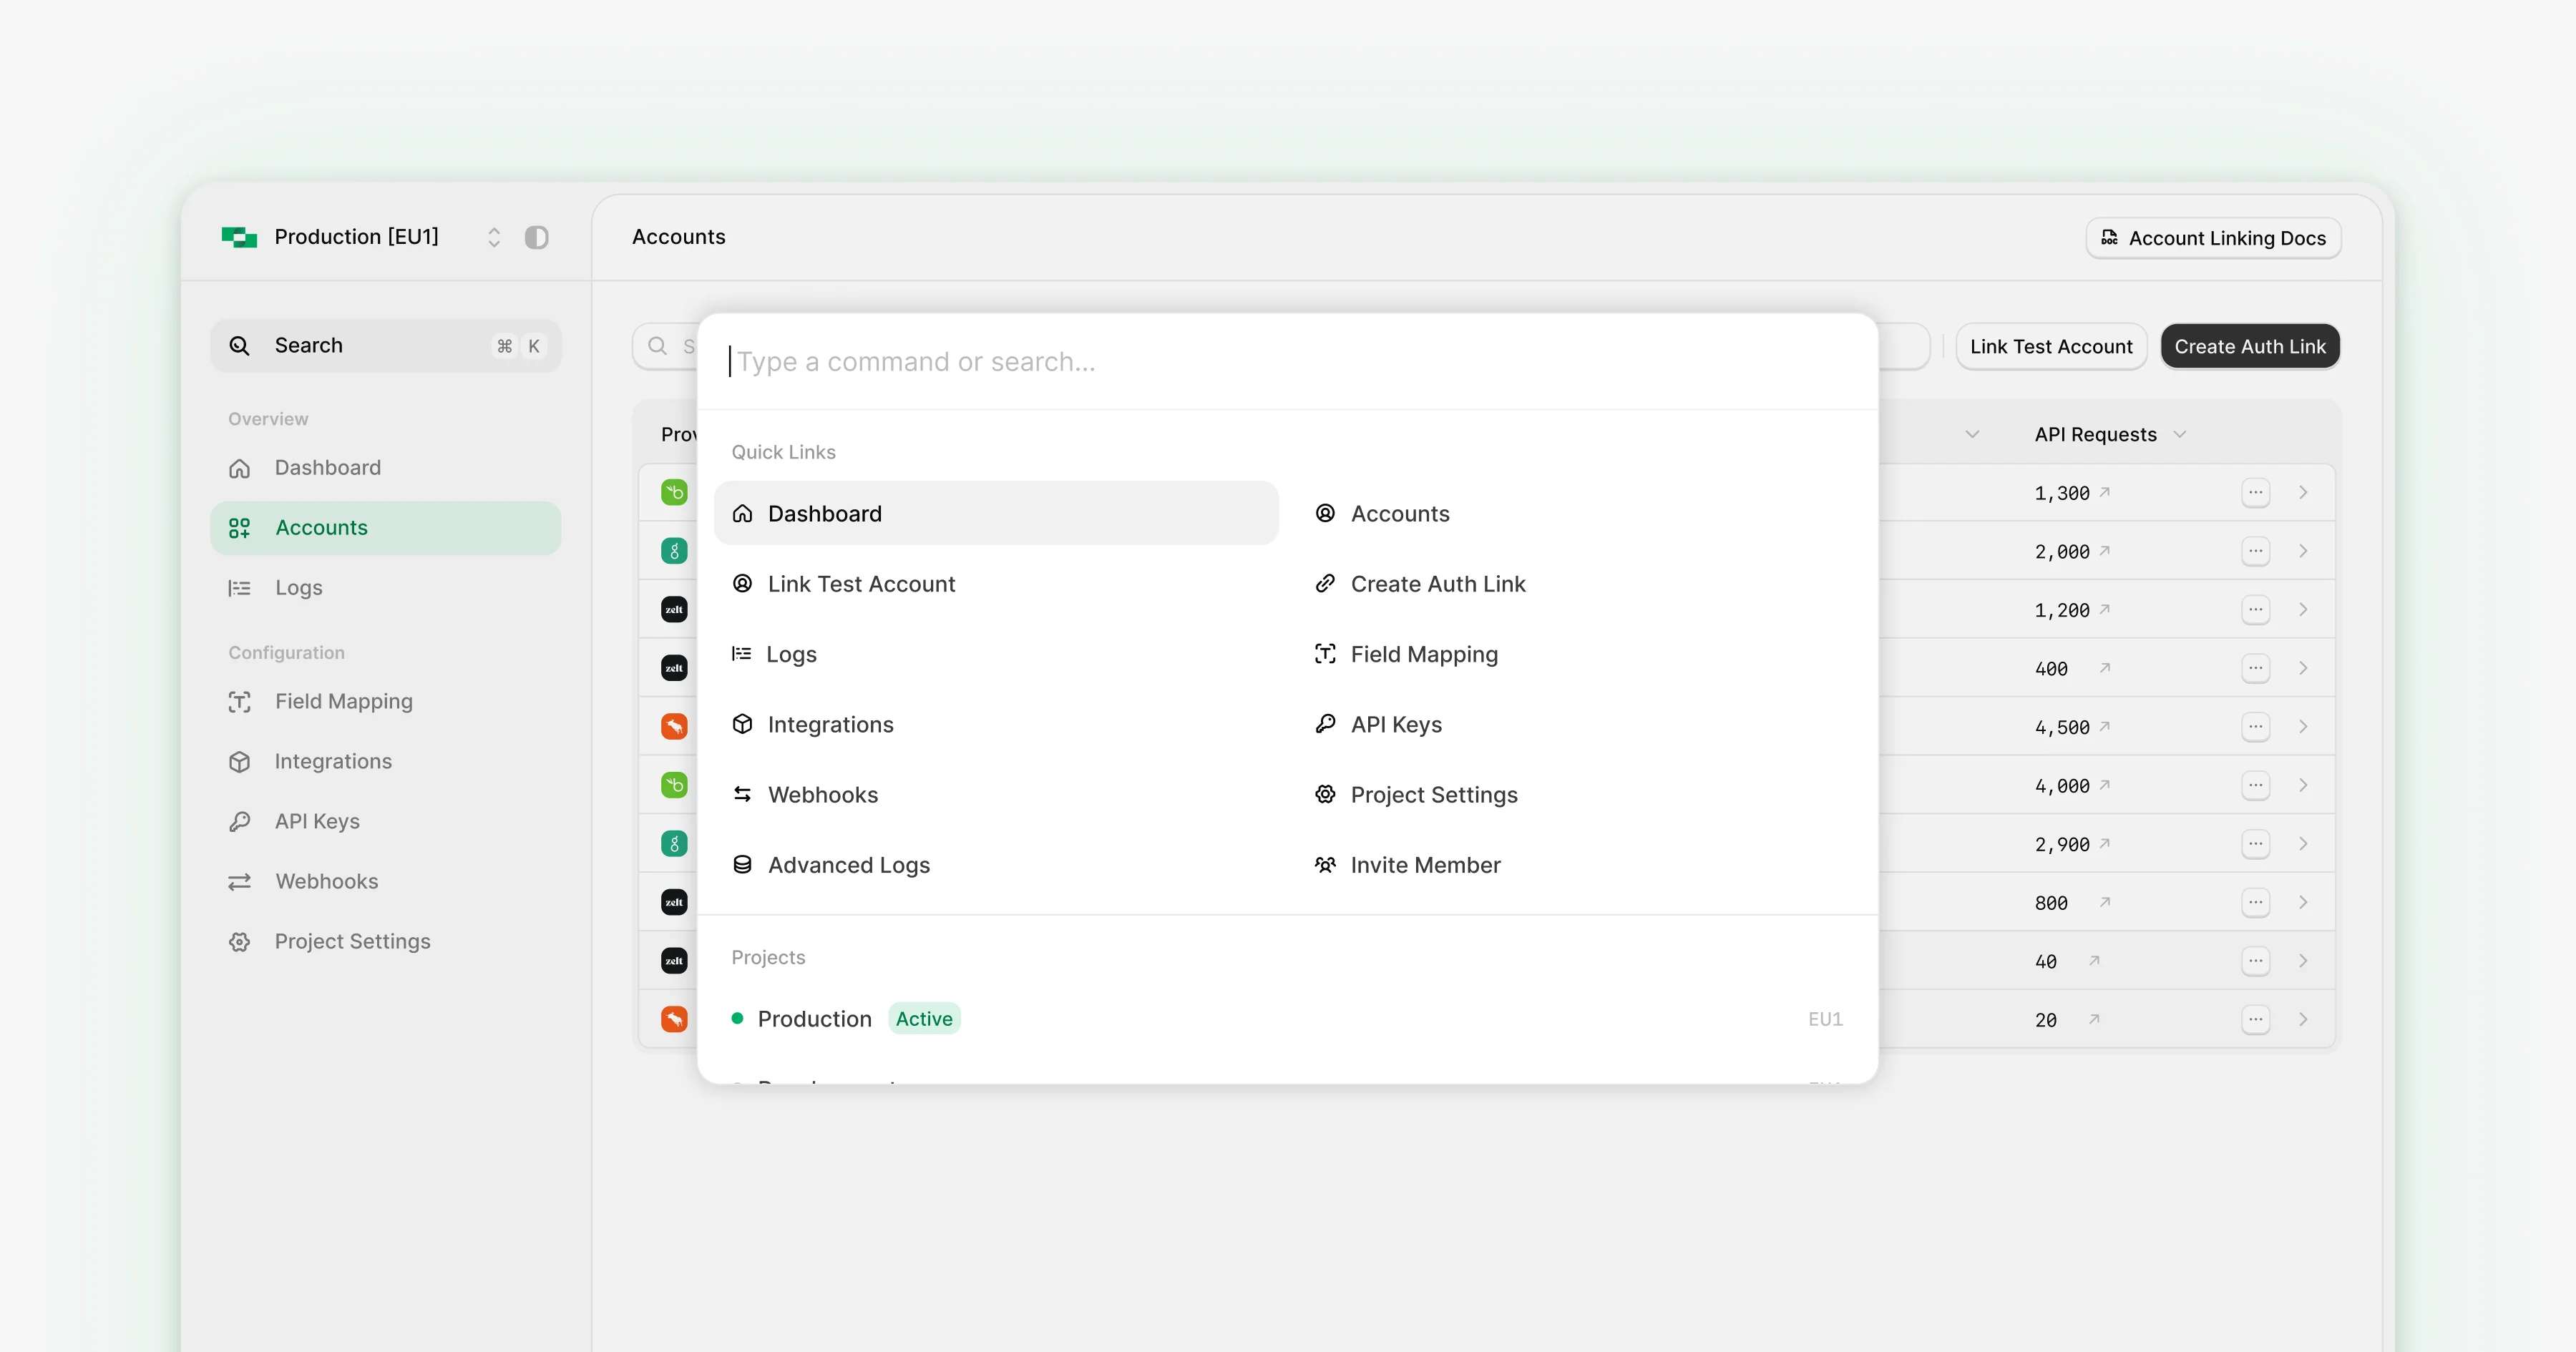
Introducing the StackOne Command Menu - open it instantly with Cmd/Ctrl + K for quick access to any part of the product.
Read about Command Palette
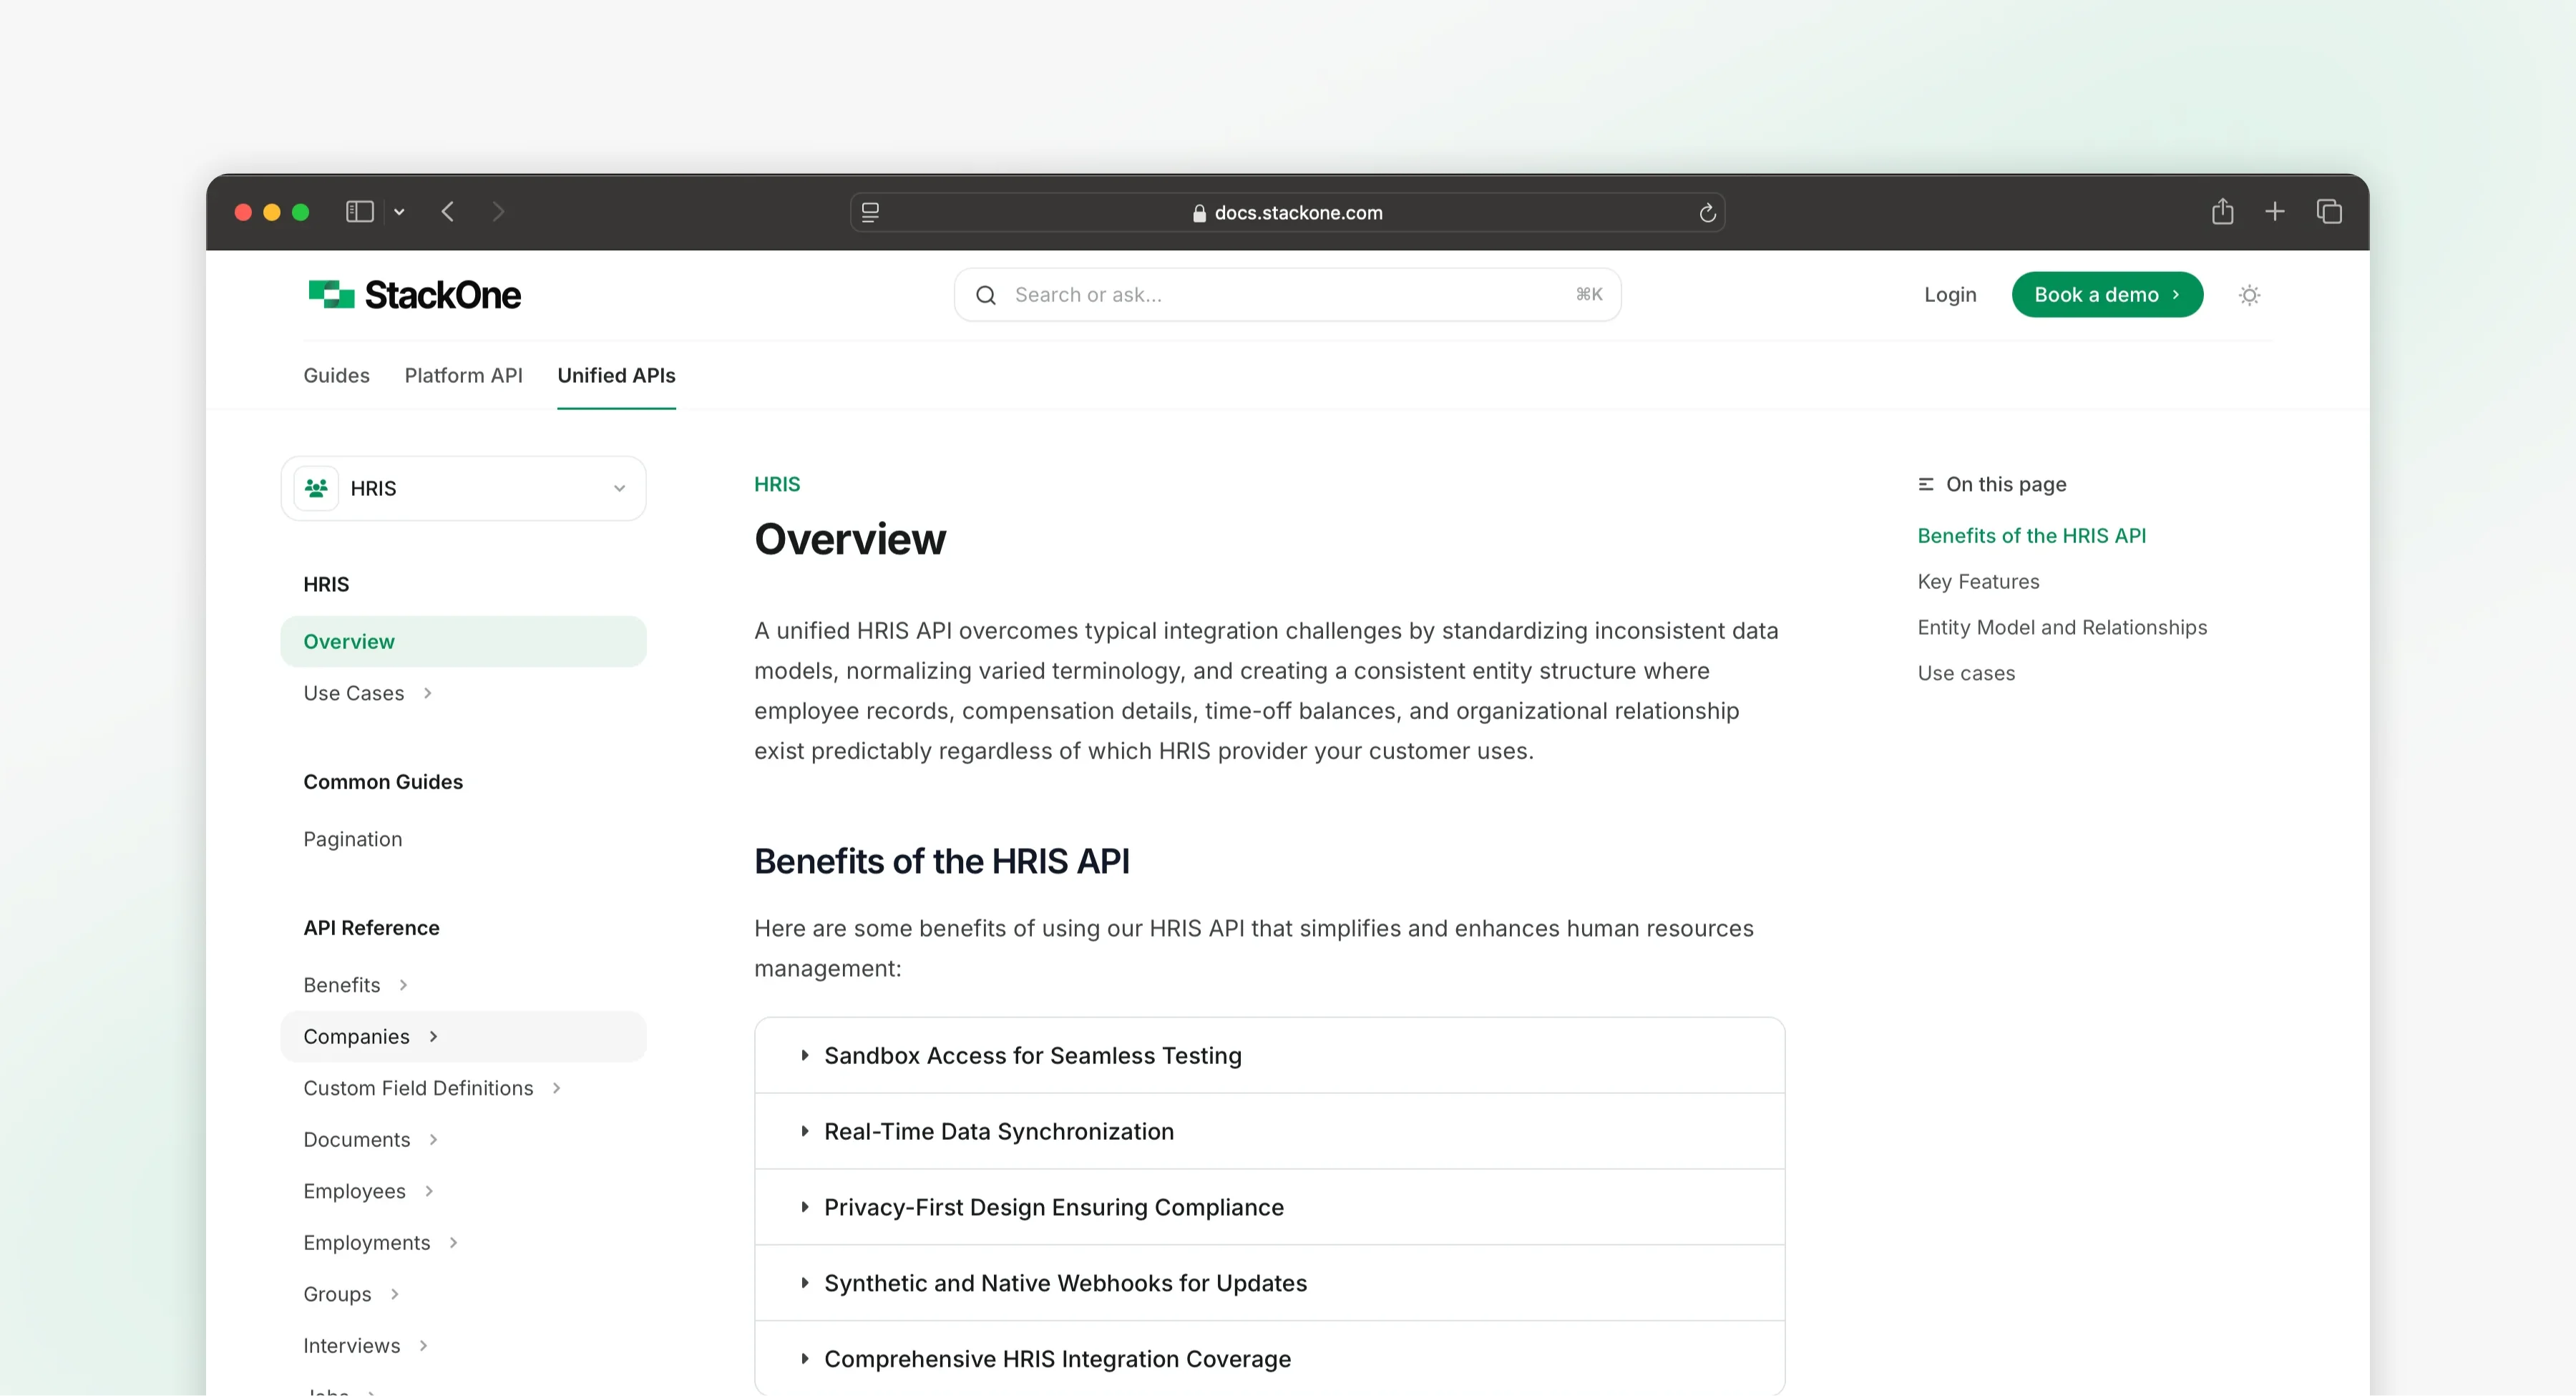
We launched a completely redesigned documentation experience at docs.stackone.com, powered by Mintlify, with AI-enhanced search.
Read about New Documentation
A powerful upgrade to give you complete visibility into requests made via and by StackOne with extended data retention and deeper insights.
Read about Advanced Logs
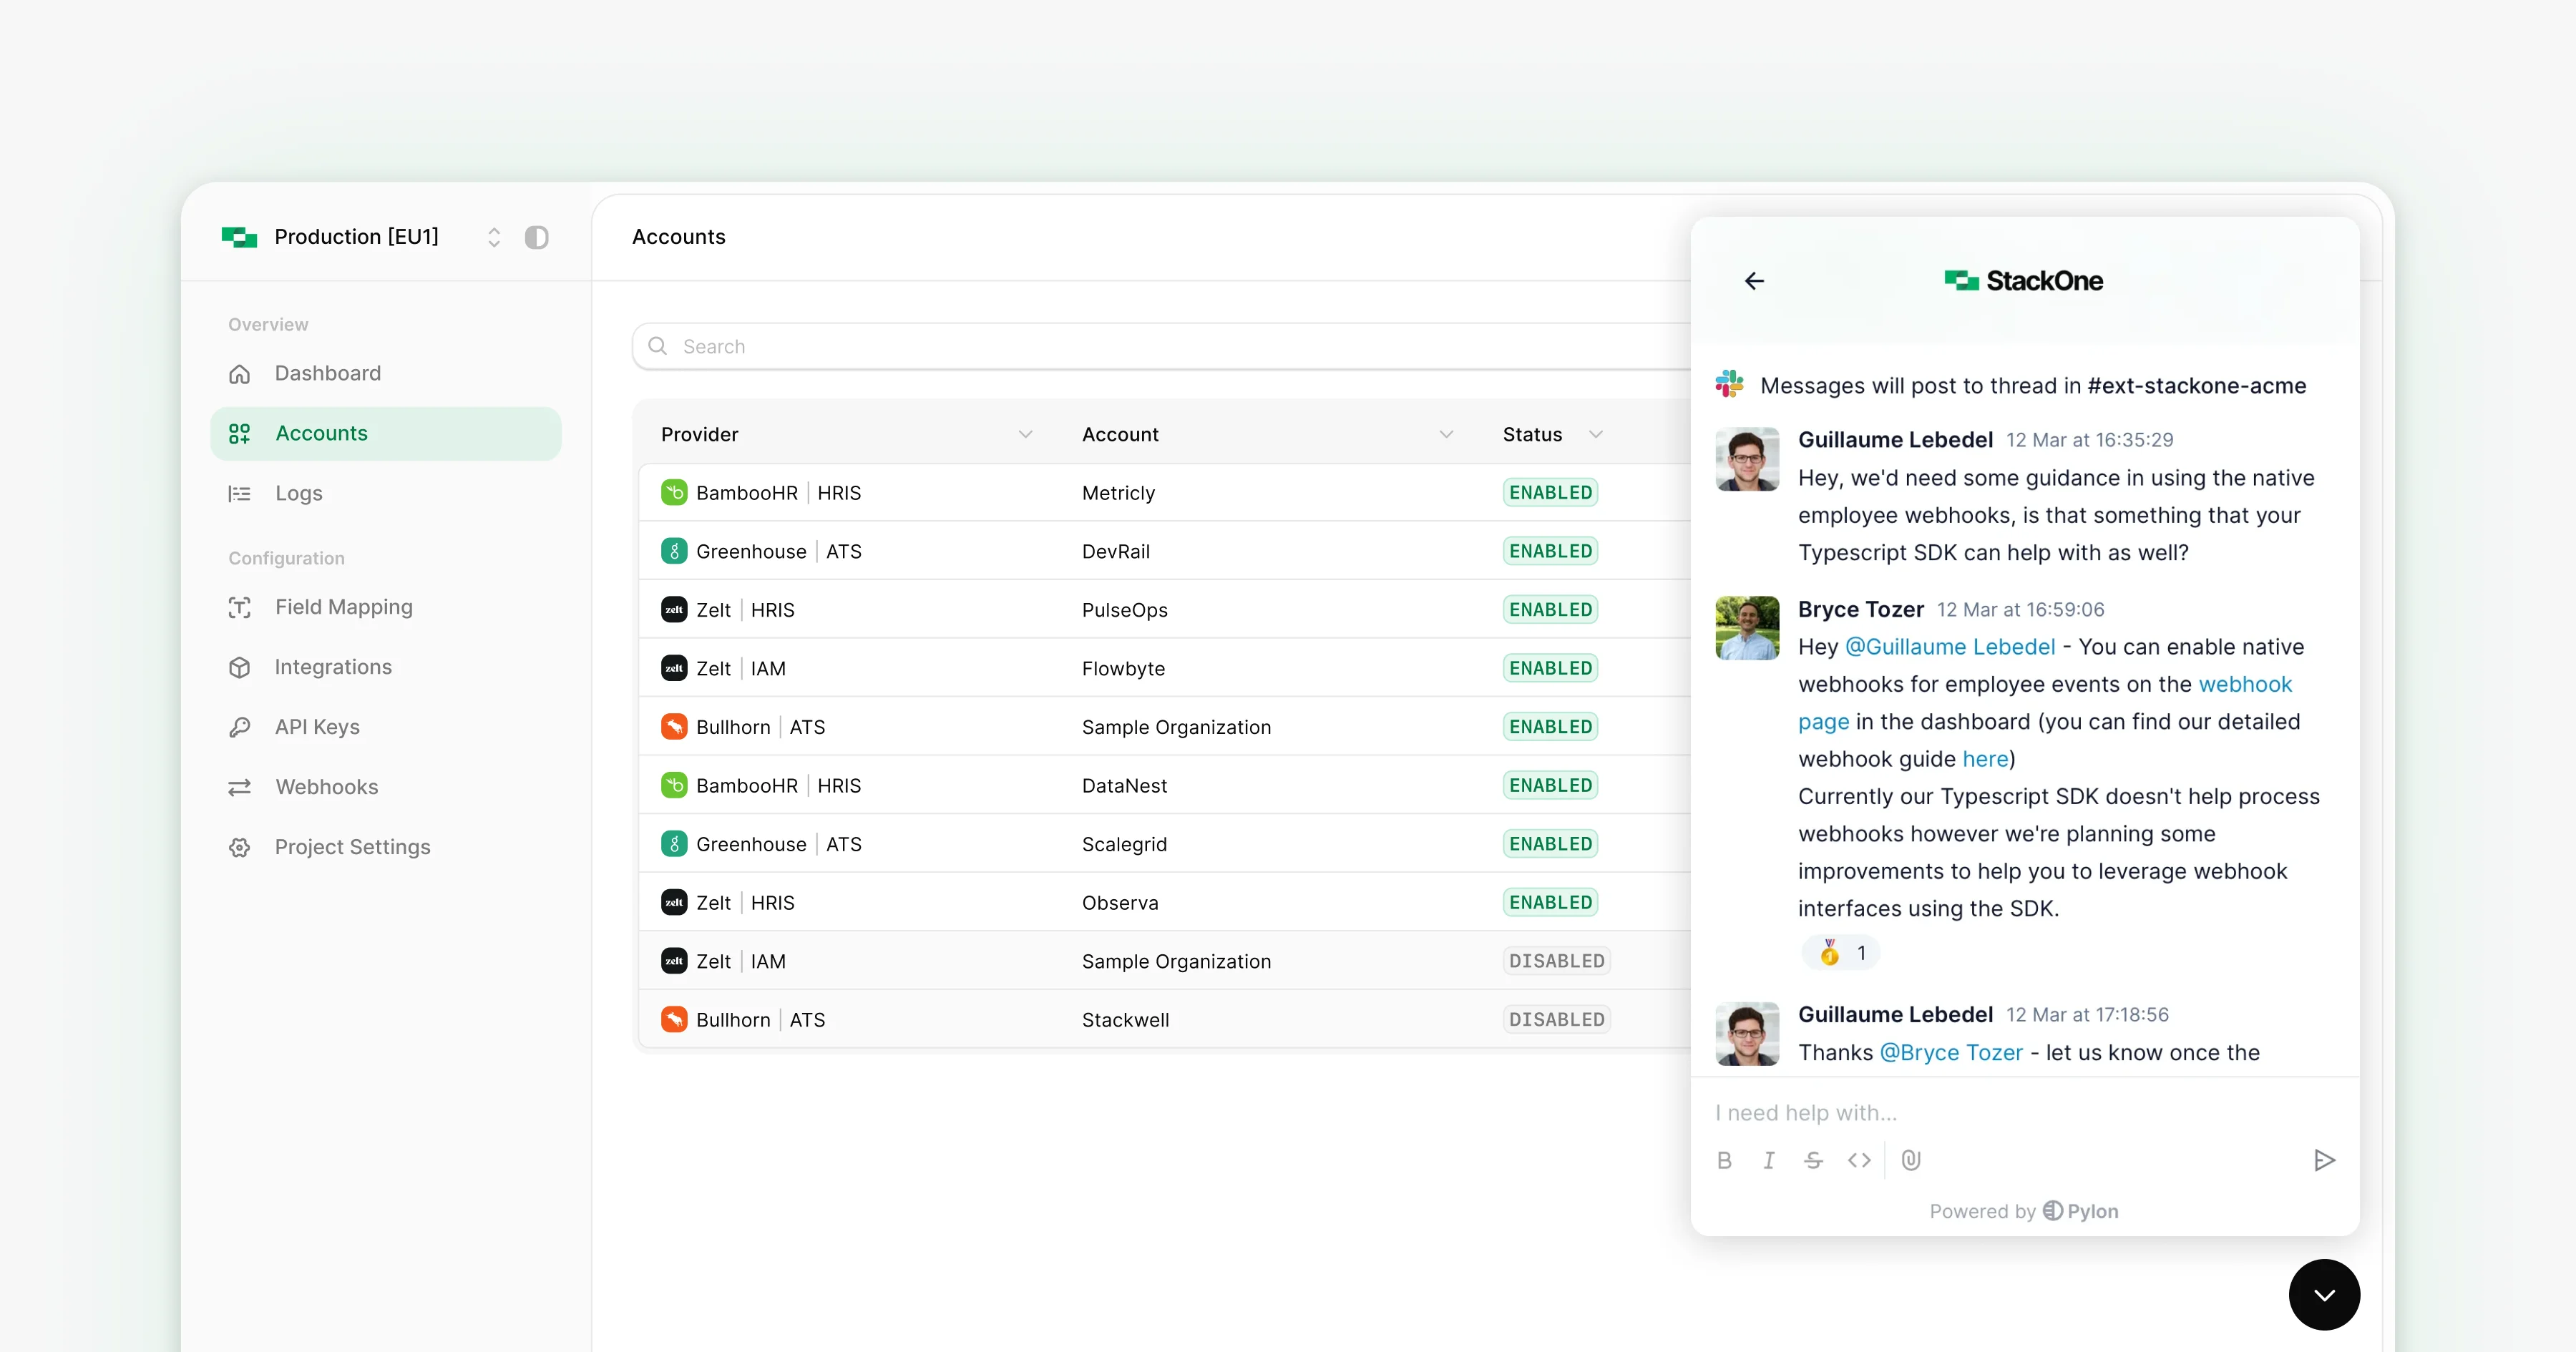
In-app chat allows every logged-in user to instantly open issues and requests directly within the chat interface.
Read about Chat Support
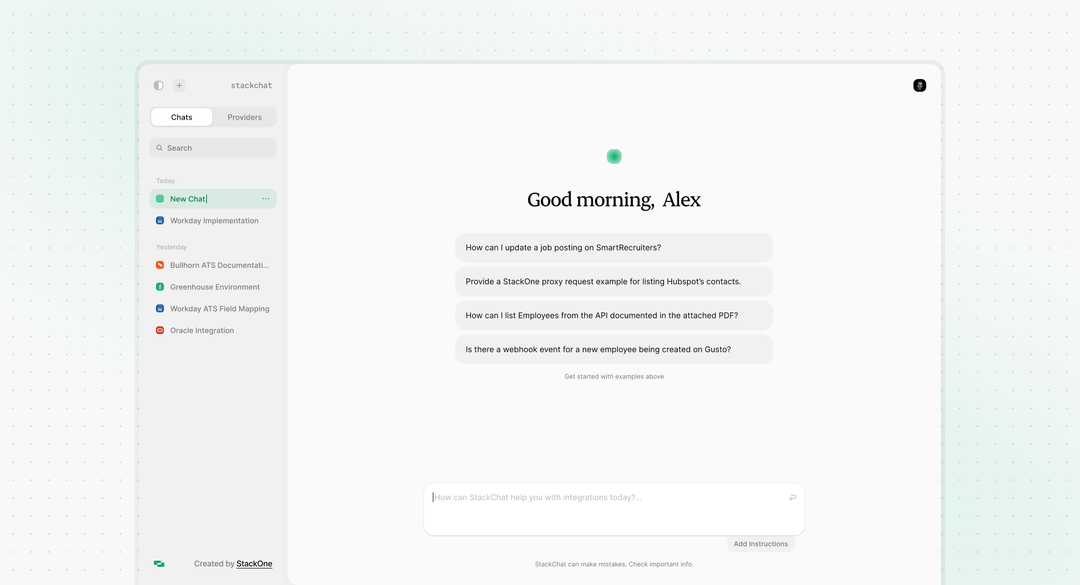
AI-driven assistant designed to streamline API integration tasks with extensive knowledge of 150+ enterprise SaaS APIs.
Read about StackChat
Made it easier to sign in with identity providers like Microsoft or Okta through new Single Sign On authentication methods.
Read about SSO Auth
StackOne Hub can now be embedded within any page with customizable height, width, and styling options.
Read about Hub Customization
New API category for Identity and Access Management, accessing data from 80+ SaaS platforms for compliance and access orchestration.
Read about IAM API
Simplified navigation, modernized design, and streamlined project management features across 8+ dashboard pages.
Read about Dashboard UX
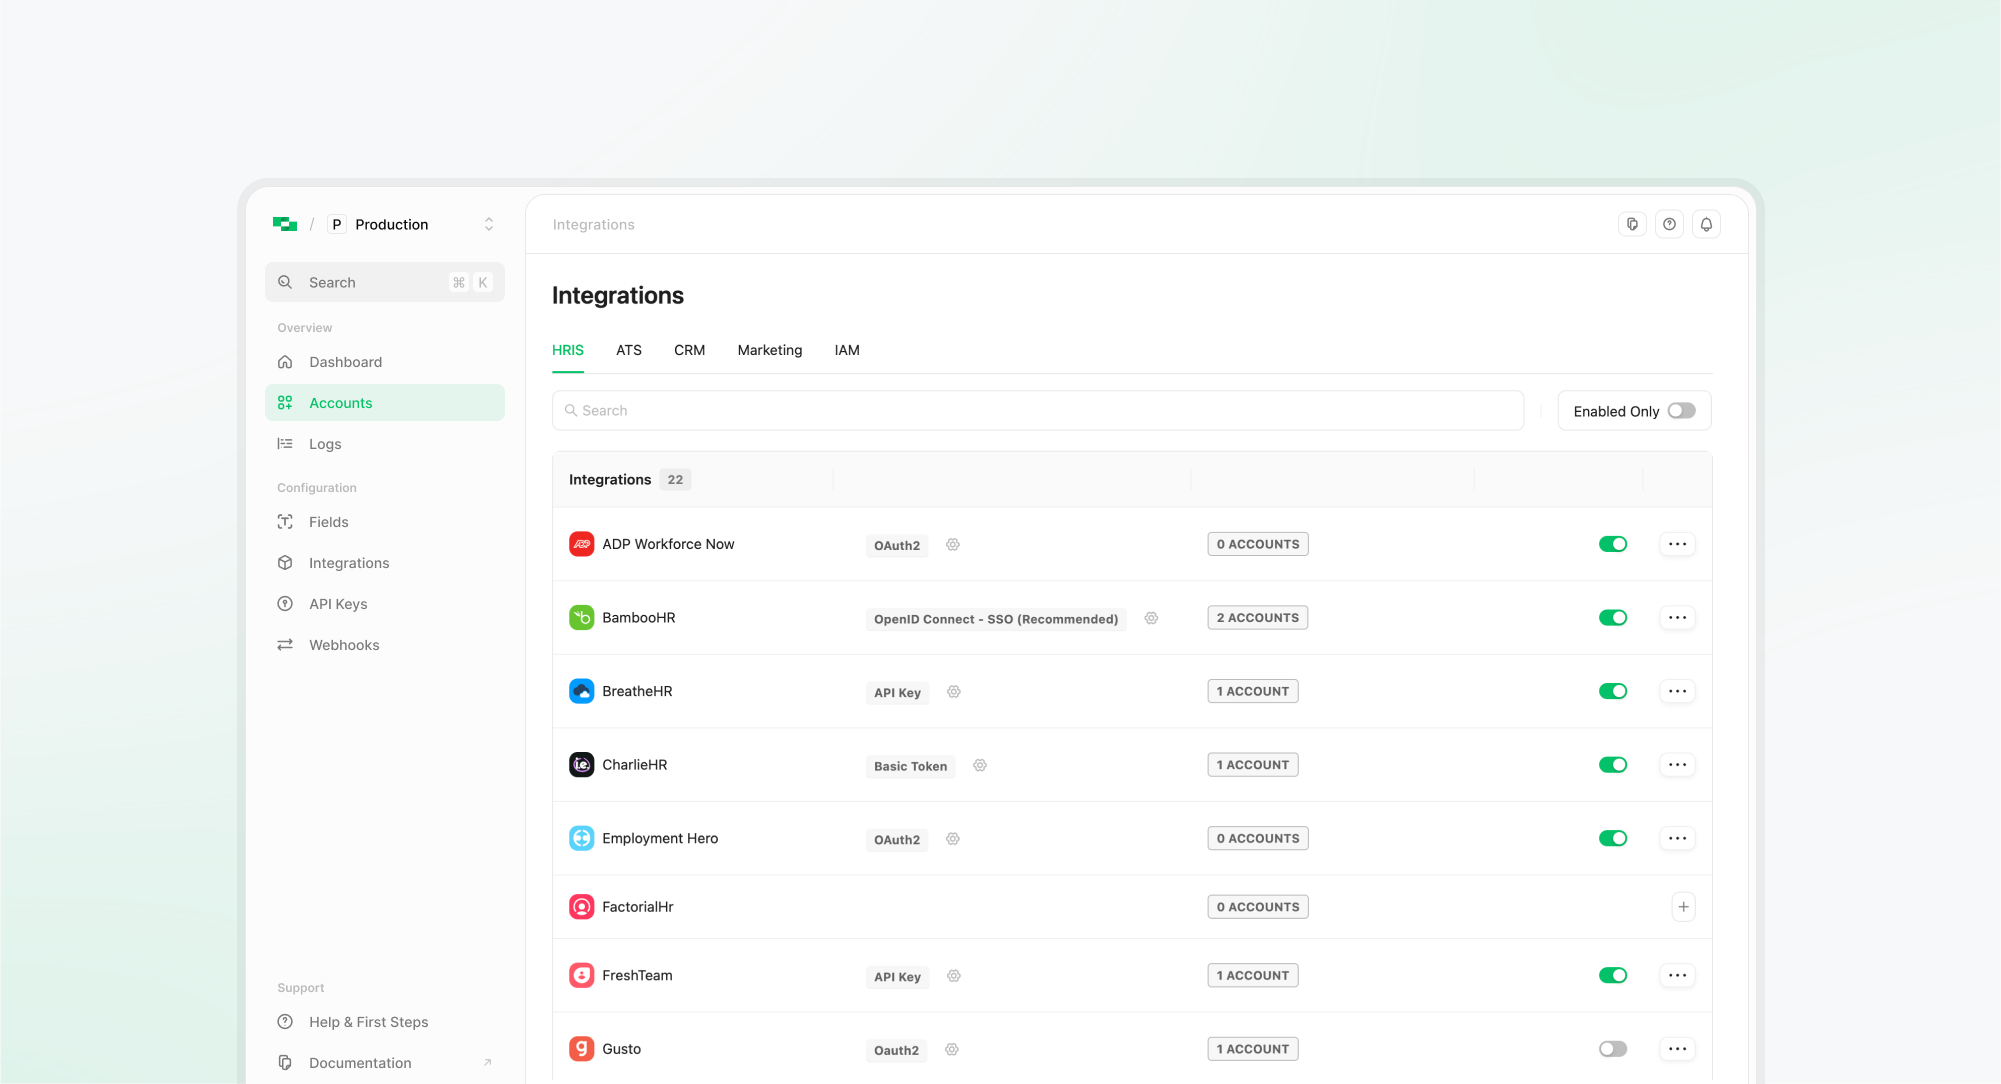
Quickly view, enable, or disable integrations with one-click setup for various authentication methods on the revamped integrations page.
Read about Integrations Page
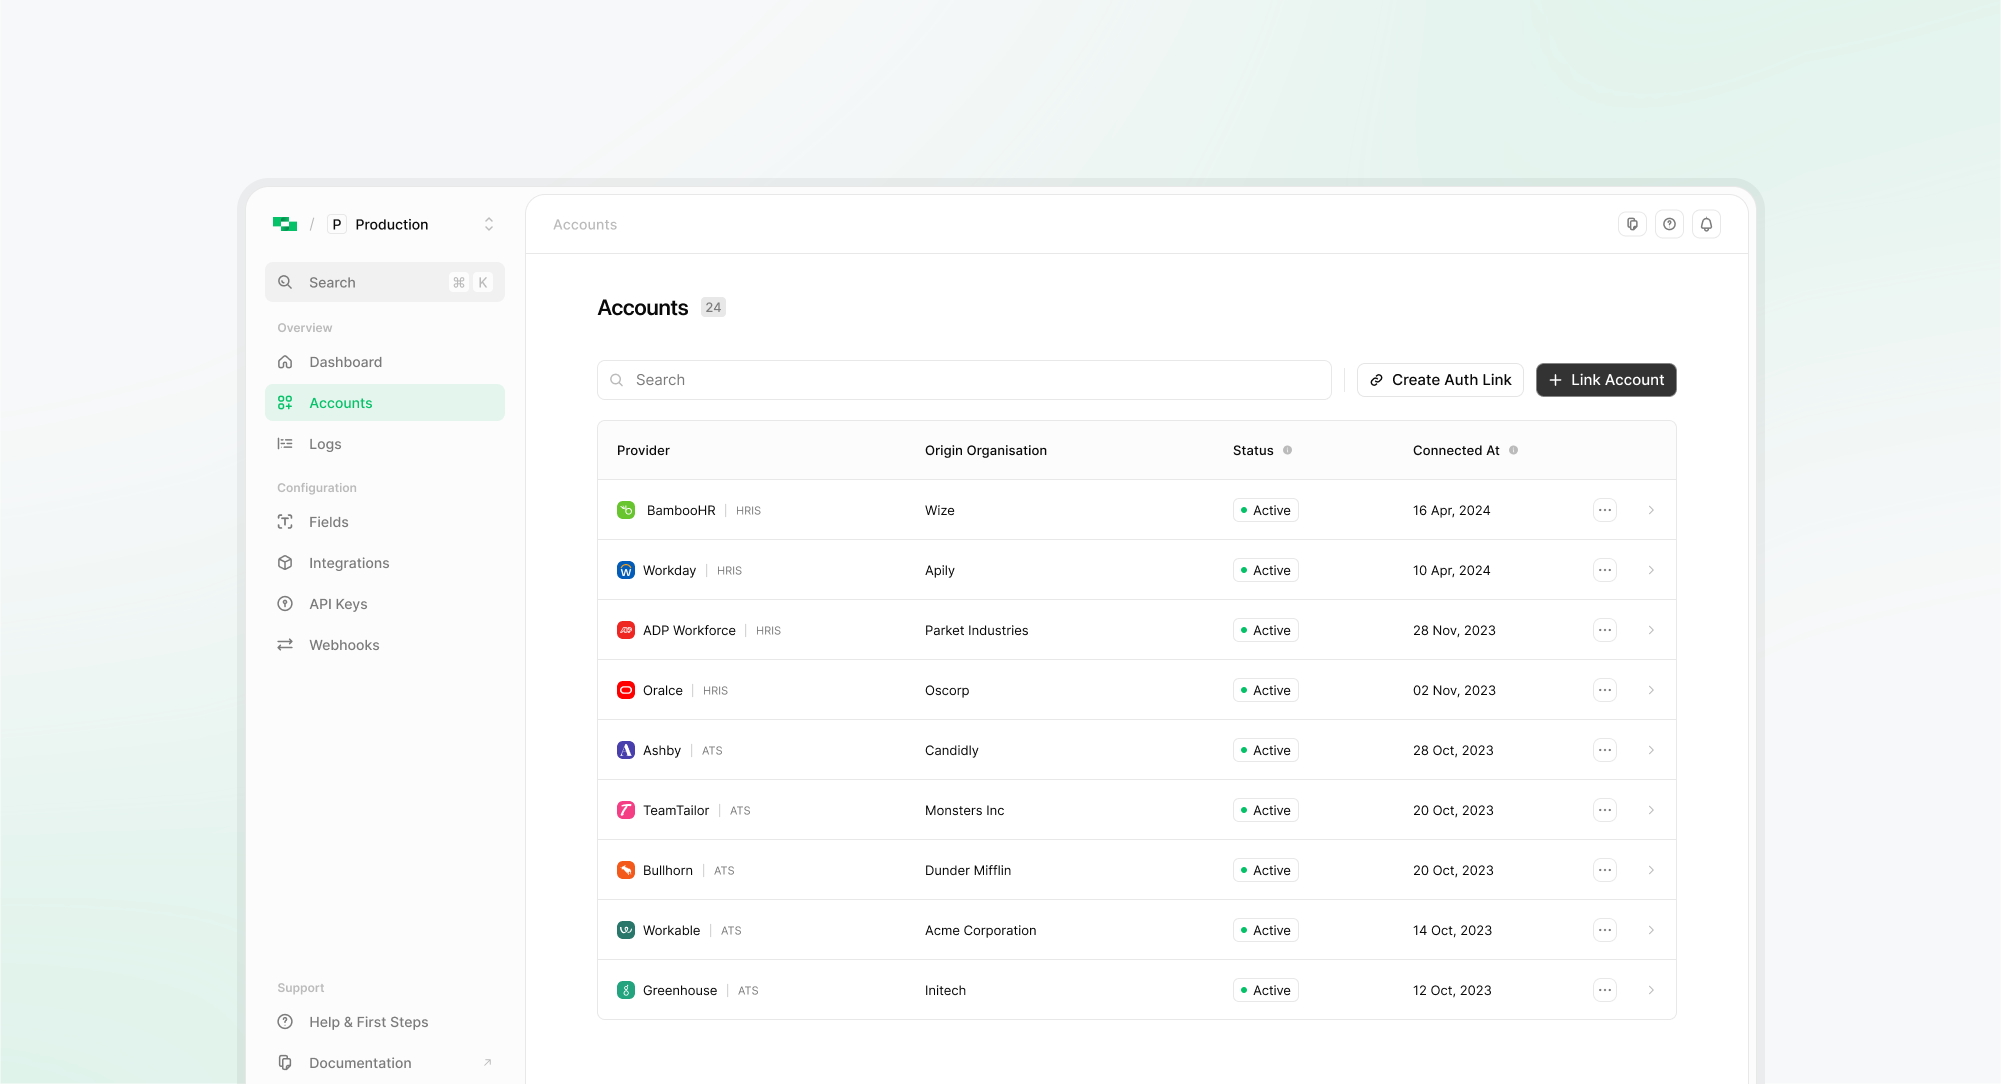
Complete redesign of the accounts section making it easier to filter and take action on linked accounts.
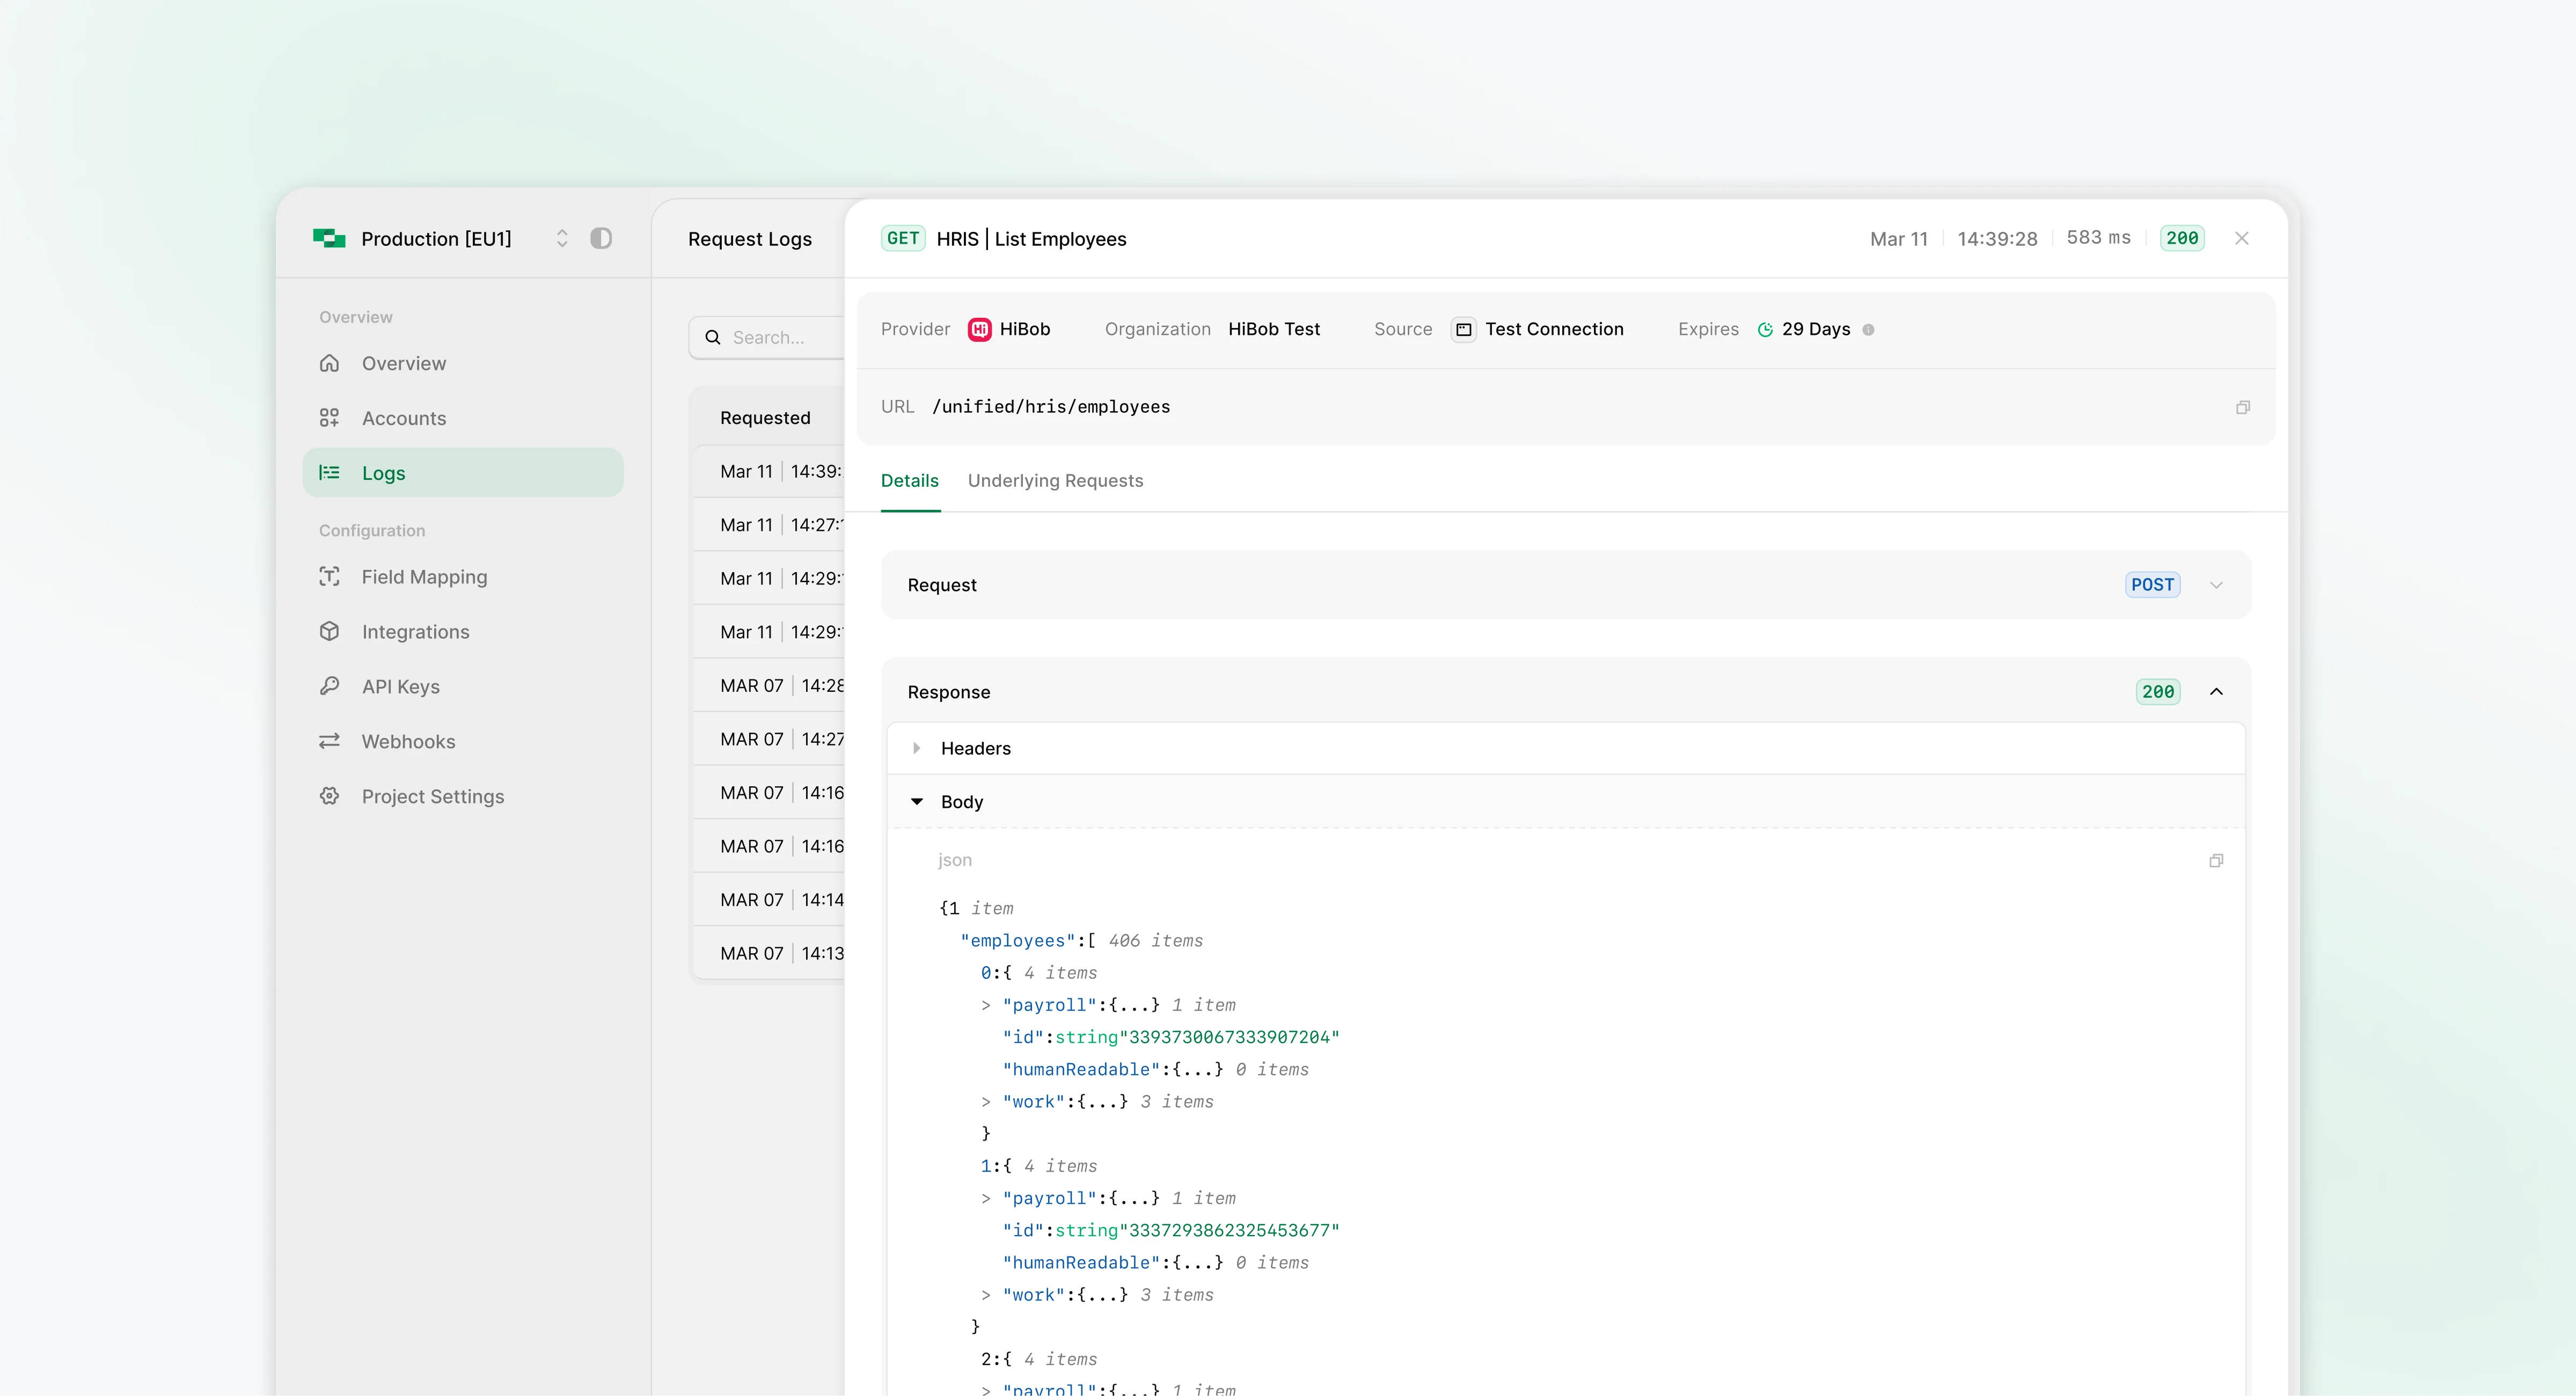
Read about Accounts SectionView calls to the StackOne API, see underlying calls, and filter by account, response code, connector, and source.
Read about Request Logs